
If you’ve moved from pfSense to OPNsense and want to replicate Squid and SquidGuard-style ad blocking and content filtering, this guide shows you how.
OPNsense includes a built-in Squid proxy and URL-list filtering functionality that can be used to block ads, malware, and other categories of content across your network. While the implementation differs slightly from pfSense, the end result is very similar.
In this guide, we’ll show you how to configure Squid, enable URL-list filtering, test that it’s working correctly, and optionally prevent users from bypassing the proxy.
Quick answer
OPNsense includes the functionality needed to replicate pfSense’s Squid and SquidGuard setup without installing additional packages.
To achieve similar filtering in OPNsense:
- Enable the built-in Squid proxy server
- Enable local caching
- Configure access control lists (ACLs)
- Import a URL blacklist
- Select filtering categories such as advertisements and malware
- Configure clients or devices to use the proxy
- Optionally create firewall rules to prevent users from bypassing the proxy
In our testing, this setup successfully blocked domains added to the blacklist and filtered advertisements using community-maintained URL lists.
How Squid filtering works in OPNsense
A proxy server essentially acts as a middleman between your device, such as a laptop, tablet, or smartphone, and the website or online service you are trying to access. Your in-transit data first goes through the proxy server before reaching its ultimate destination.
Proxy servers are helpful for a variety of reasons. One benefit of using a proxy server is that it can cache content, meaning it can save some remote content locally.
Proxies can perform content filtering. Content filtering means restricting access to specific domains or IP addresses. Content filtering also allows you to block online ads. Ads are not only annoying, but they also infringe on your privacy, use up your internet data, and can even carry dangerous malware.
We’re going to show you how to eliminate ads by replicating pfSense’s Squid and SquidGuard functionality in OPNsense. It’s actually somewhat simpler to configure in OPNsense because Squid Proxy is included in OPNsense’s base install, and the SquidGuard functionality (URL list-based blocking) is baked into OPNsense’s version of Squid.
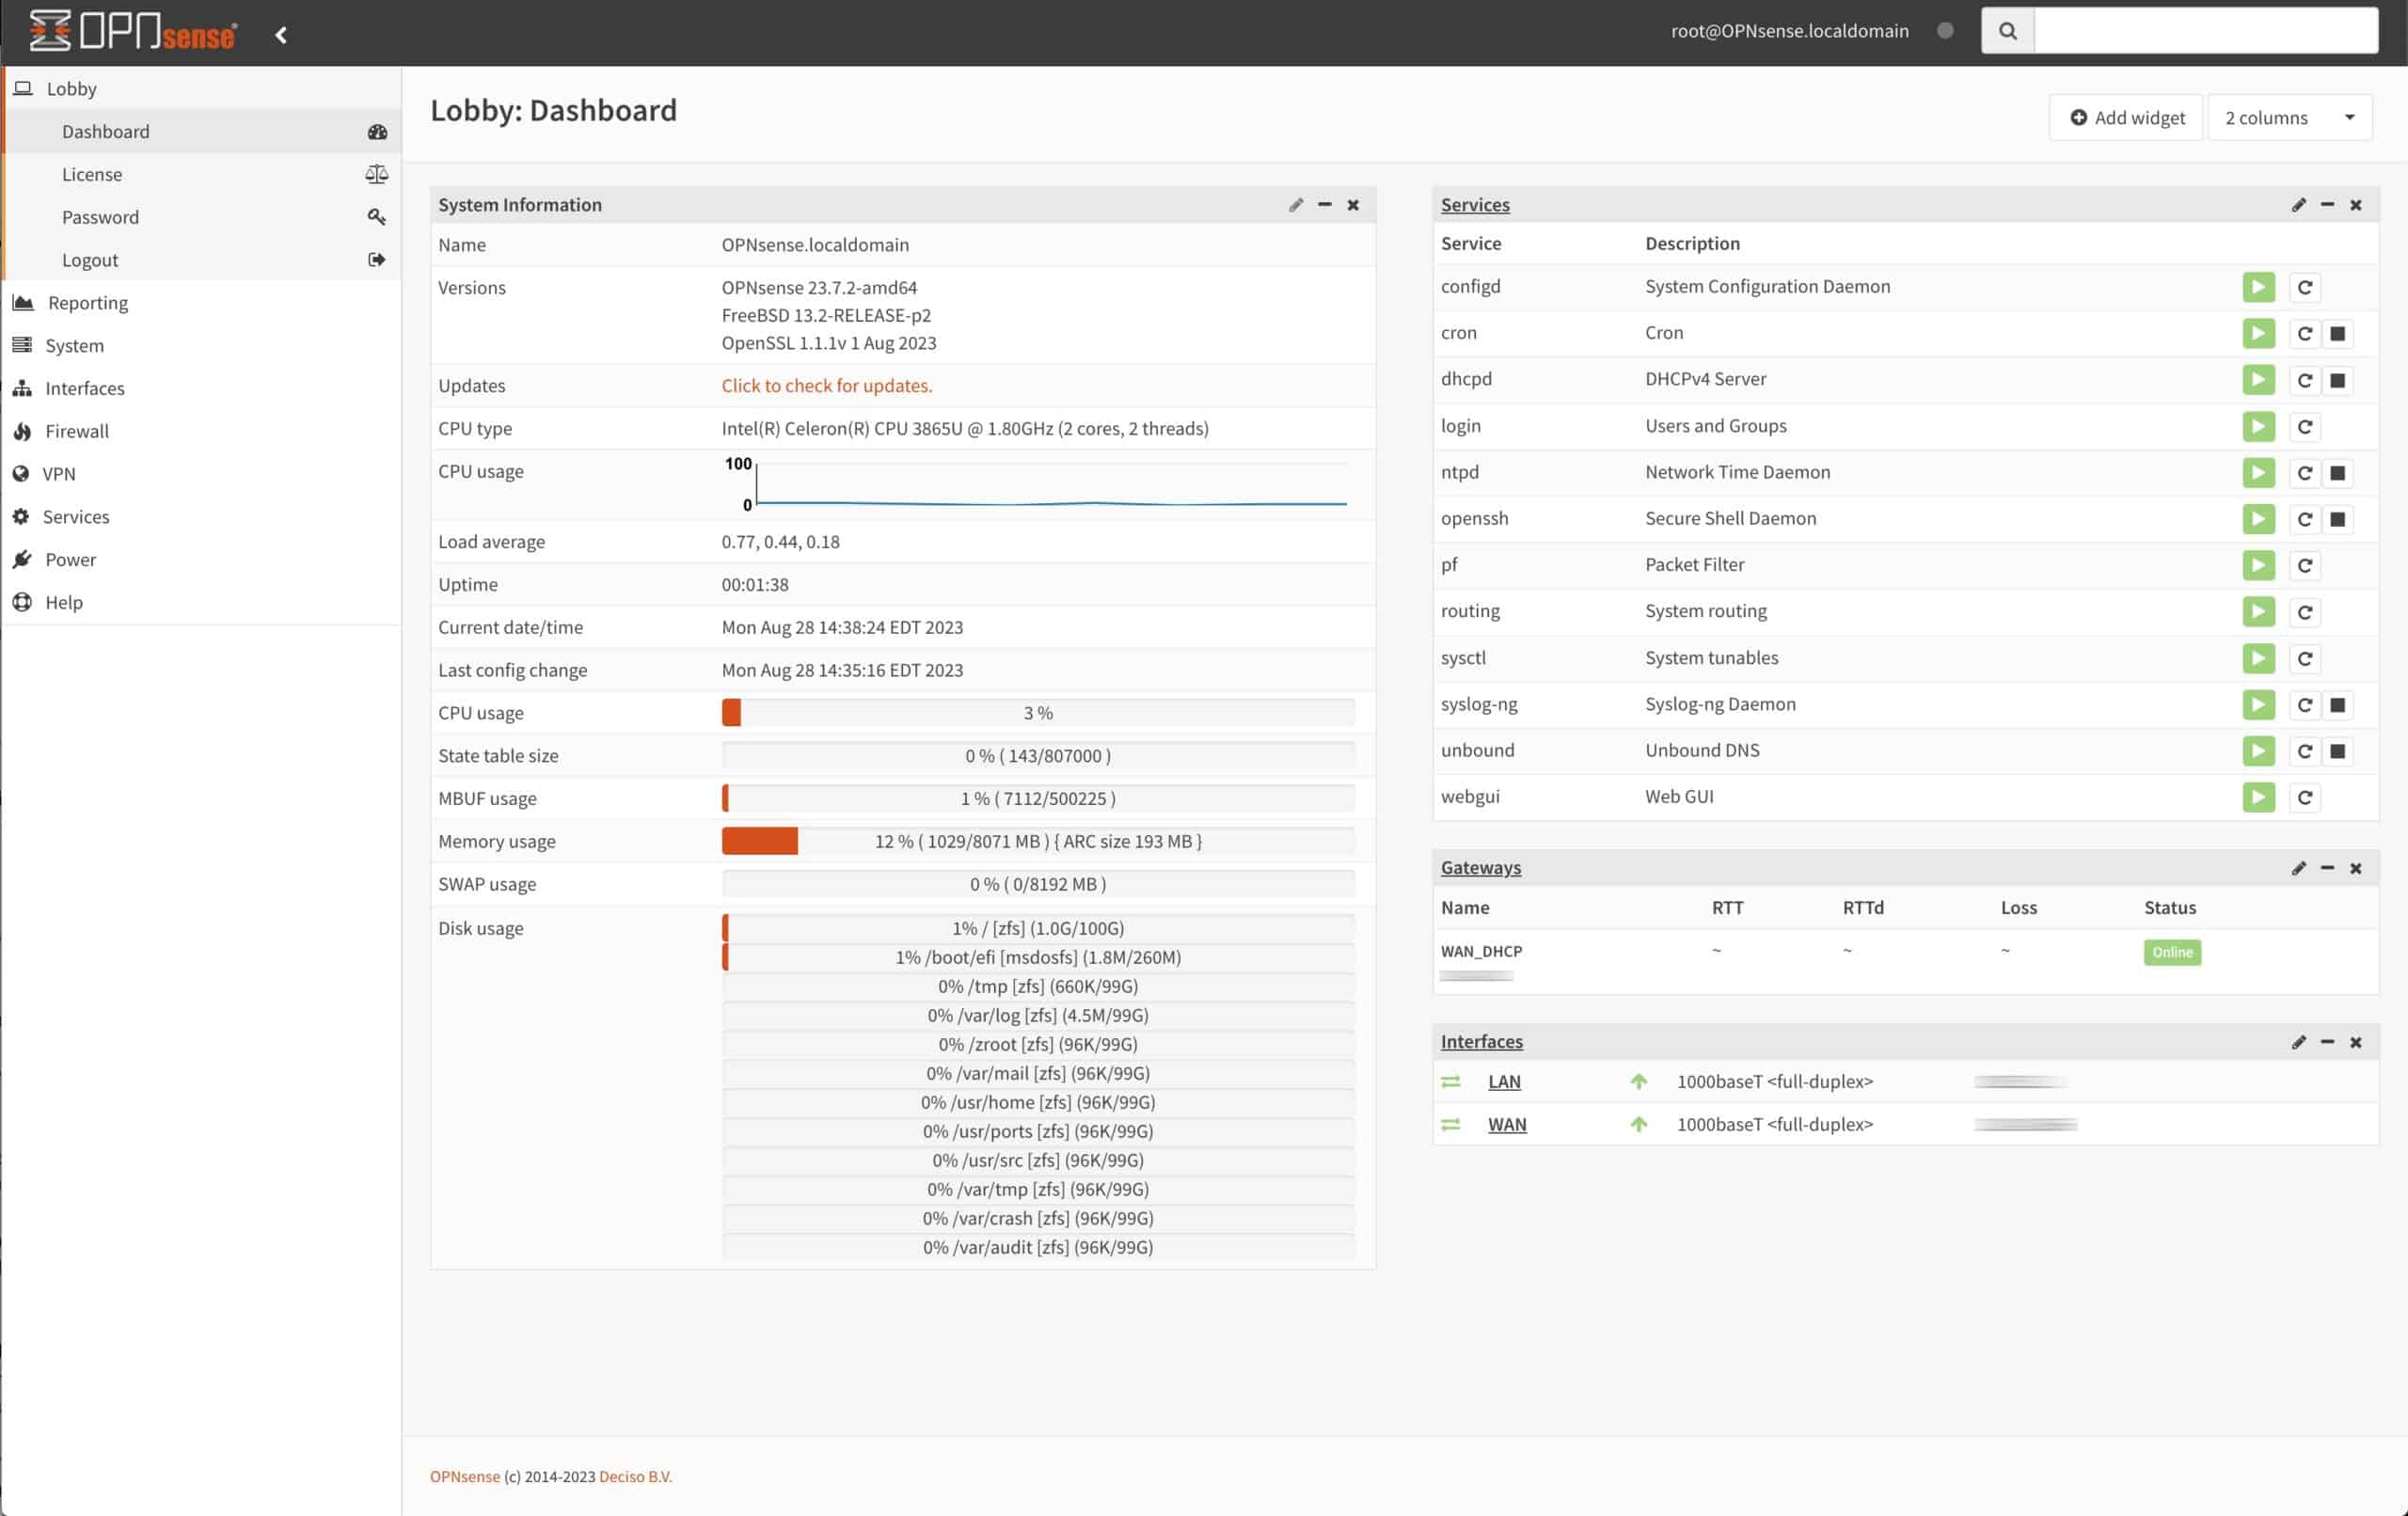
This guide assumes you have OPNsense set up with configured WAN and LAN interfaces. We’re also assuming that you can access the GUI. Also, as we go through this tutorial, we’ll focus only on the necessary sub-menus rather than reviewing every single one. Any settings not explicitly mentioned should be kept at their default values.
Squid configuration
General Proxy Settings
Because Squid is included in OPNsense’s base install, there’s no need to install any plugins. We can start configuring our proxy server straight out of the box.
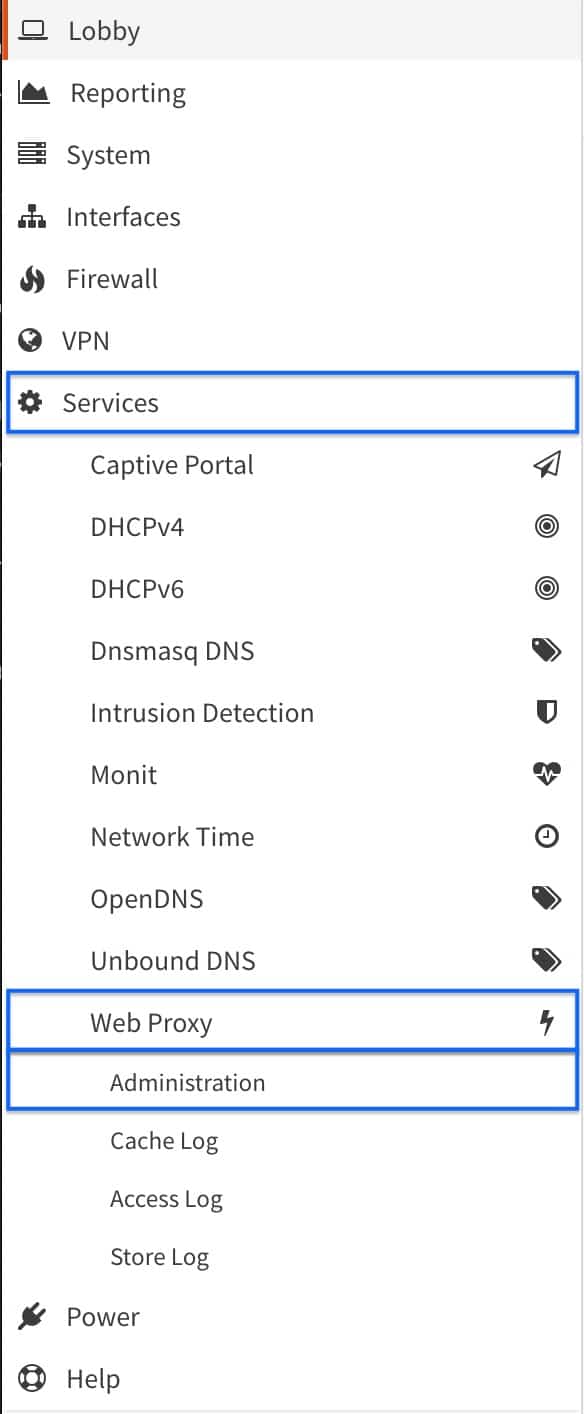
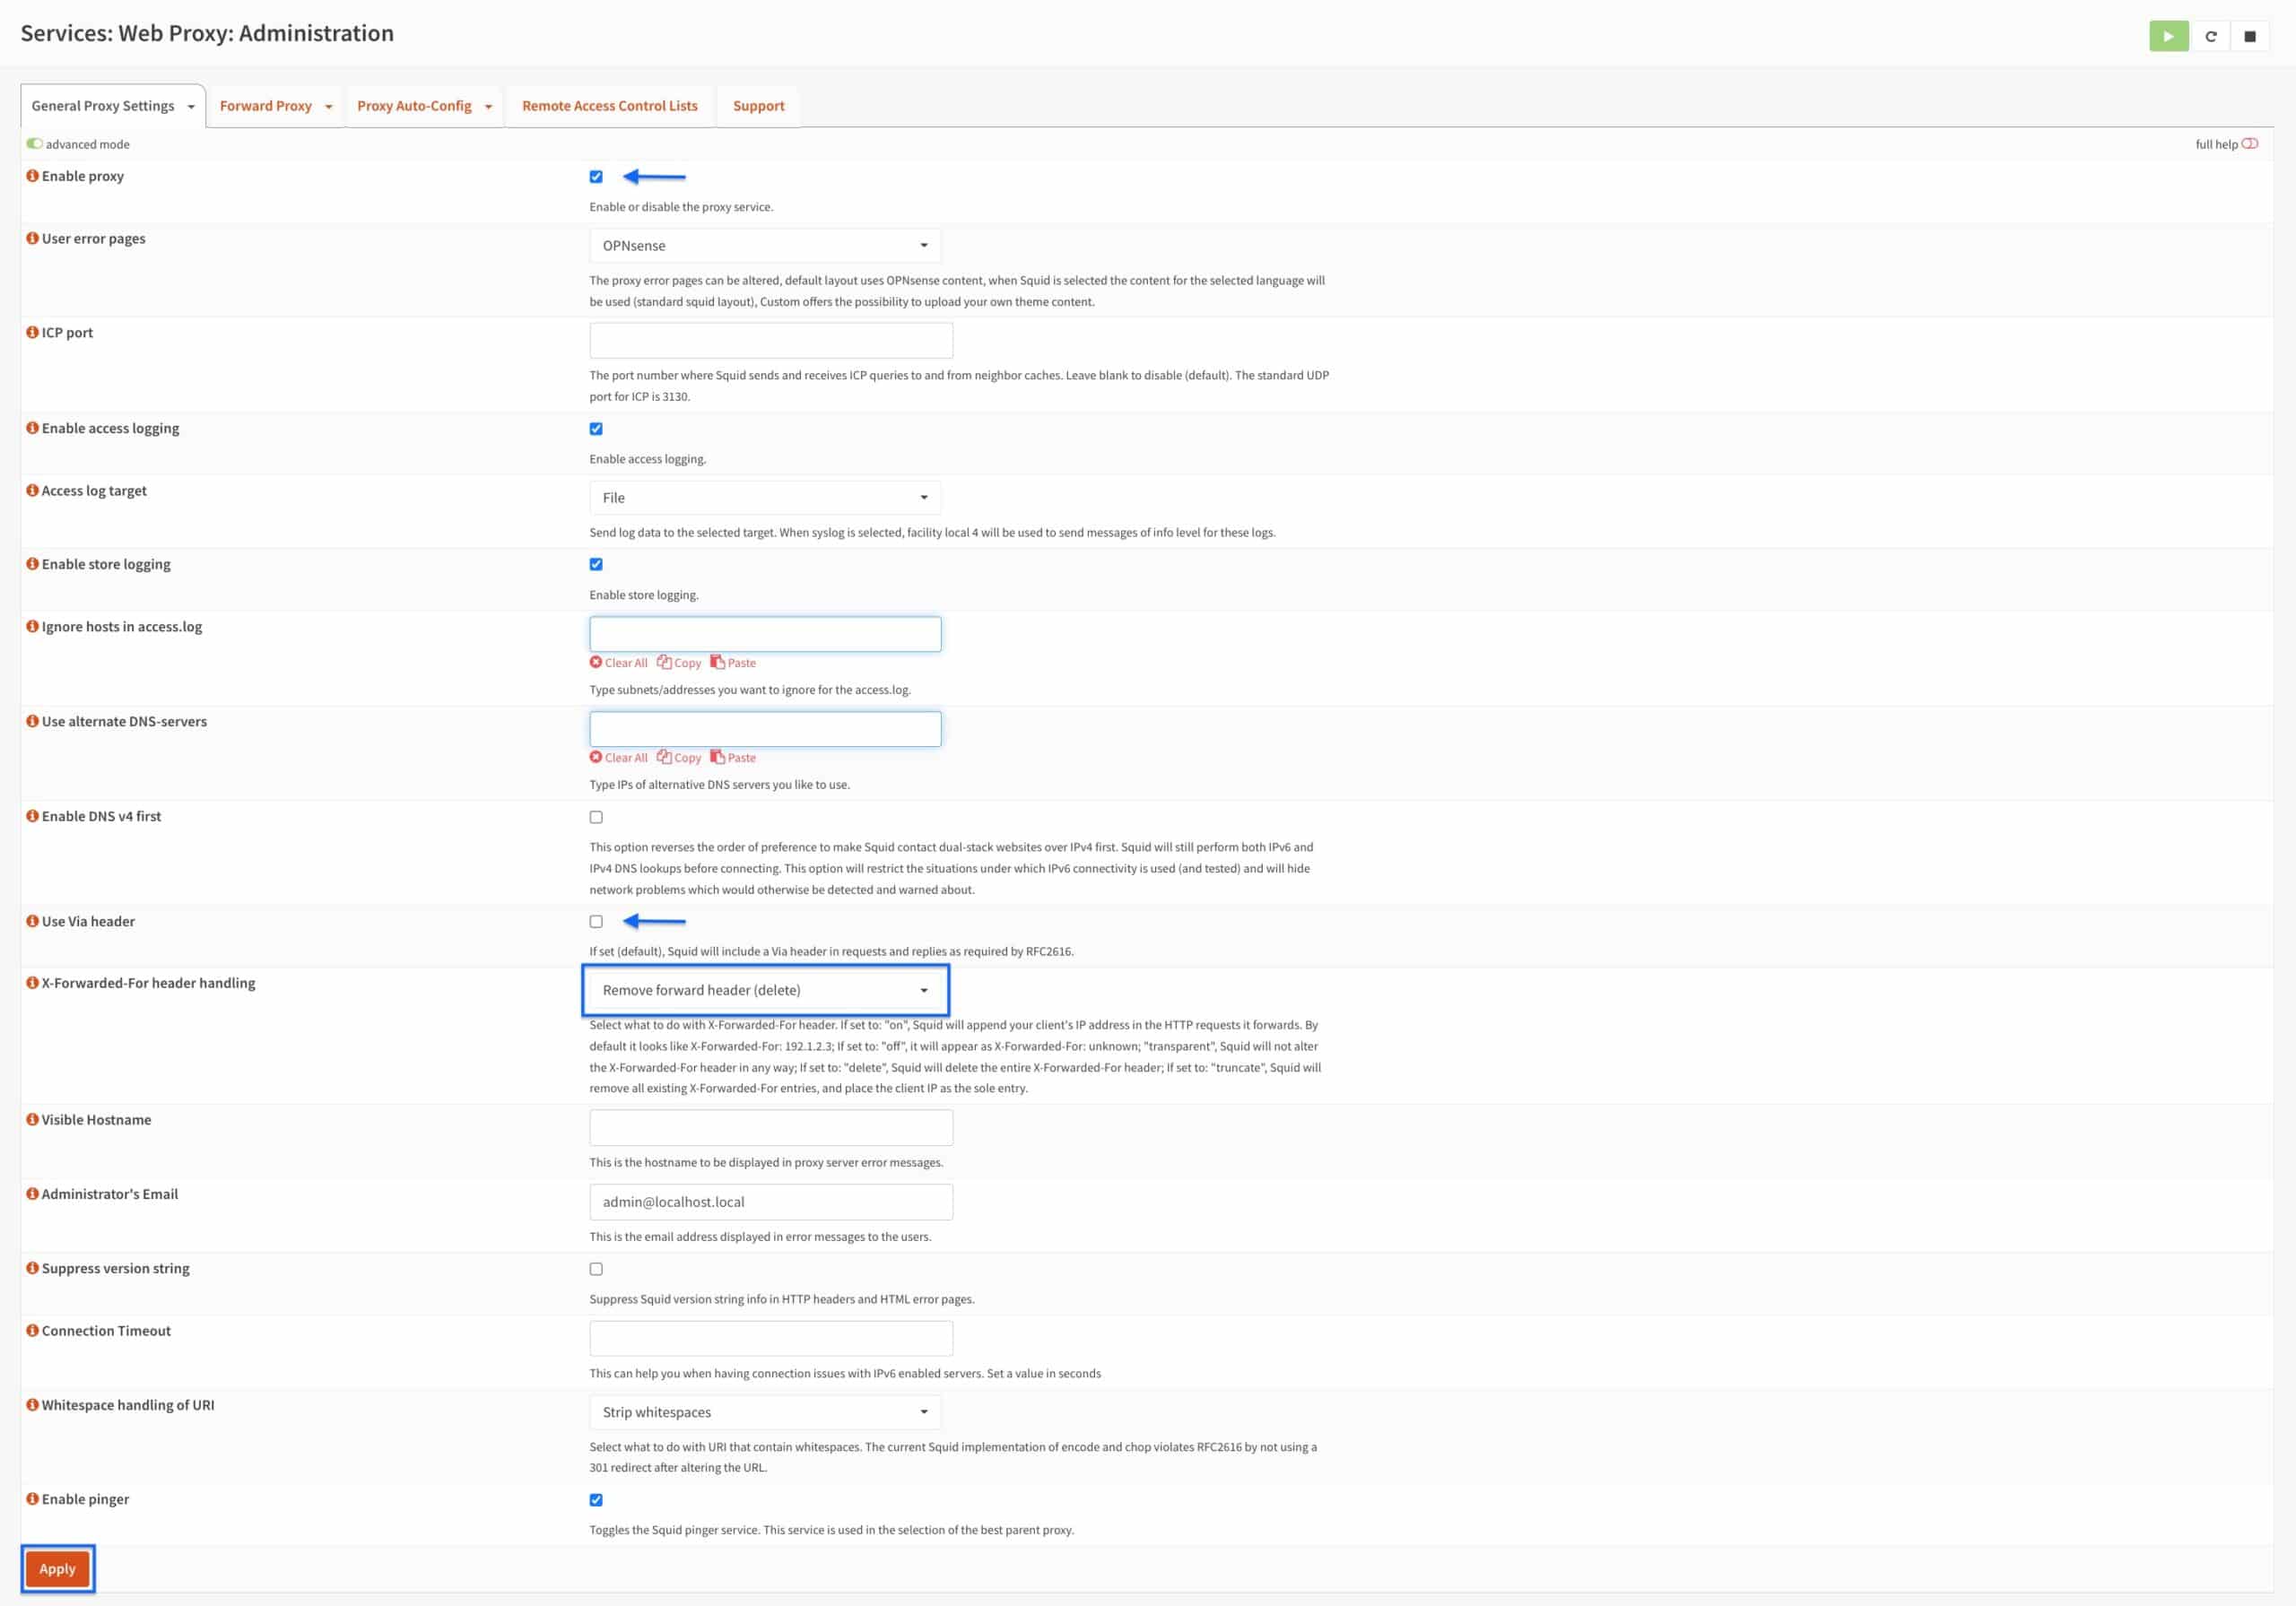
- From the side menus, go to Services > Web Proxy > Administration. This takes you to the Web Proxy Administration page.
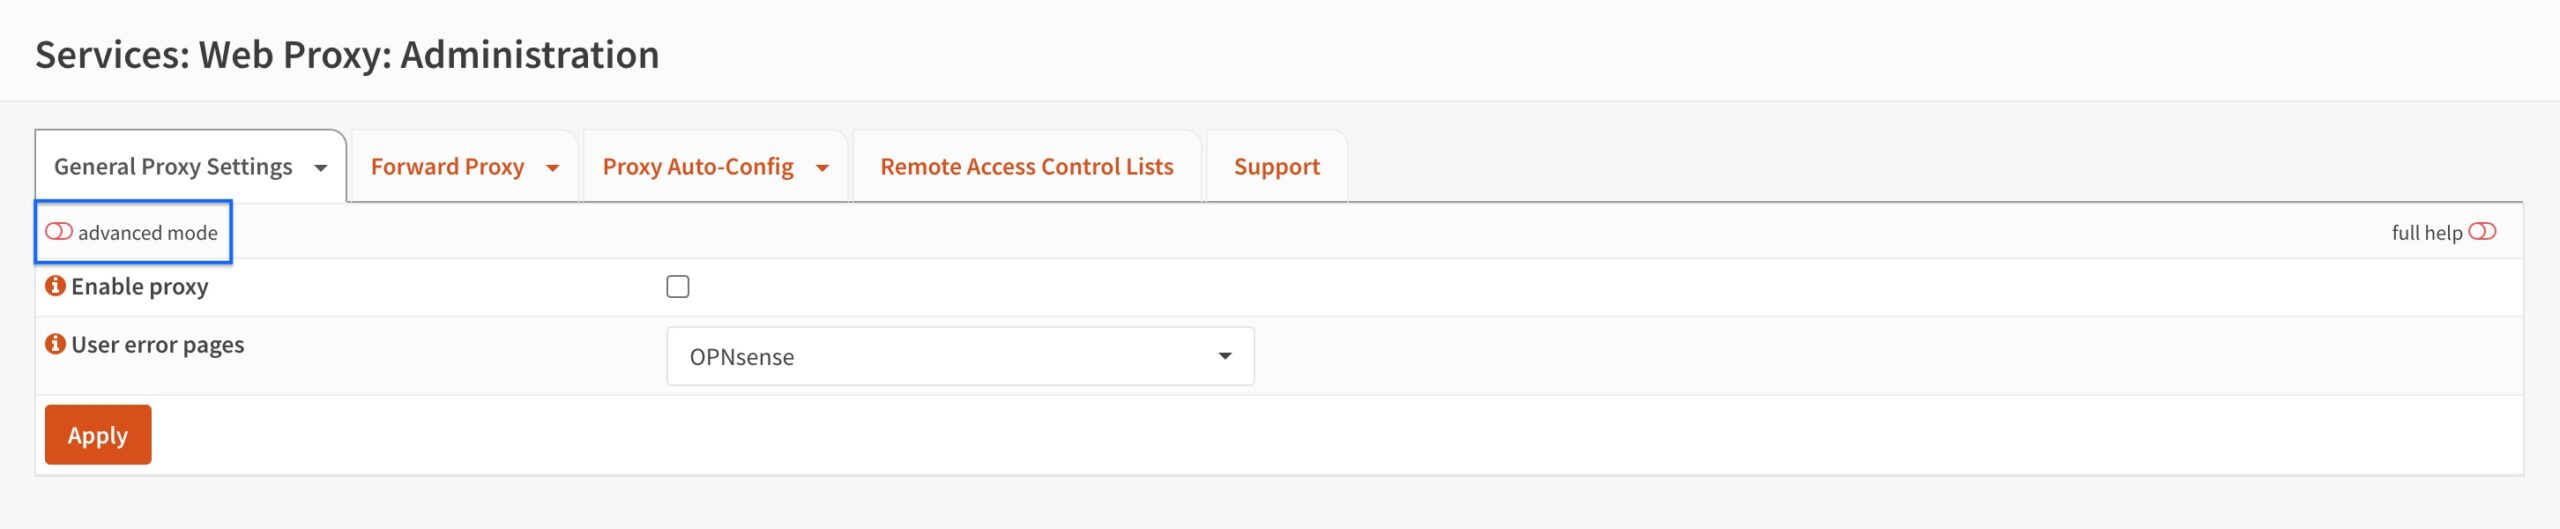
- We’ll start by clicking the advanced mode switch on the top left. This will display all of the settings available on this page.
- Tick the Enable proxy box.
- Untick the Use via header box (for privacy).
- Select Remove forward header (delete) from the X-Forwarded-For header handling drop-down menu.
- Click Apply.
Local Cache Settings
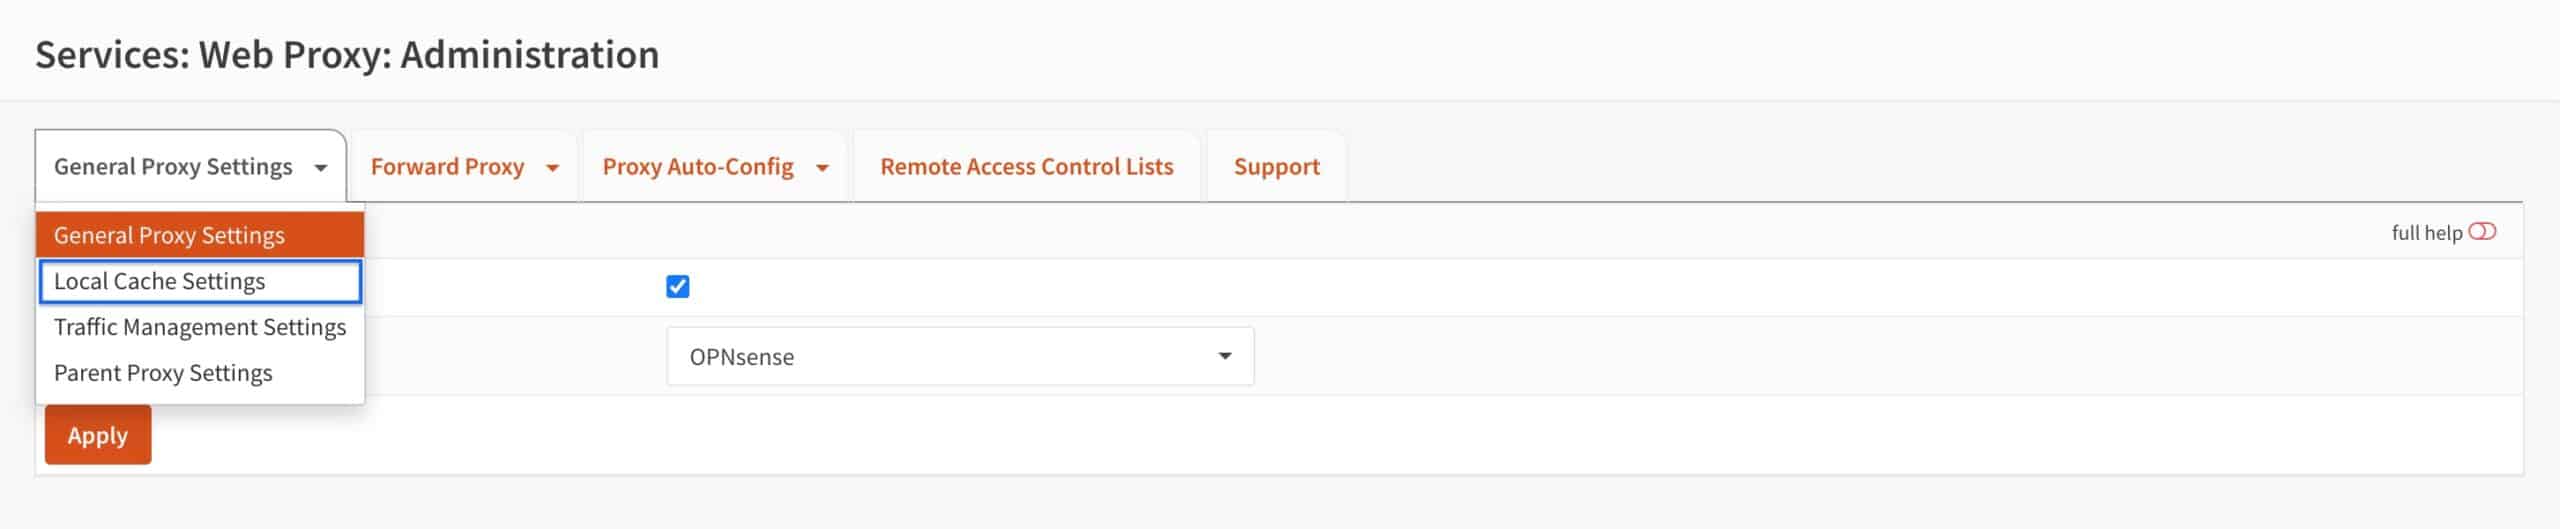
- Select Local Cache Settings from the General Proxy Settings tab drop-down menu. The Local Cache Settings page is displayed.
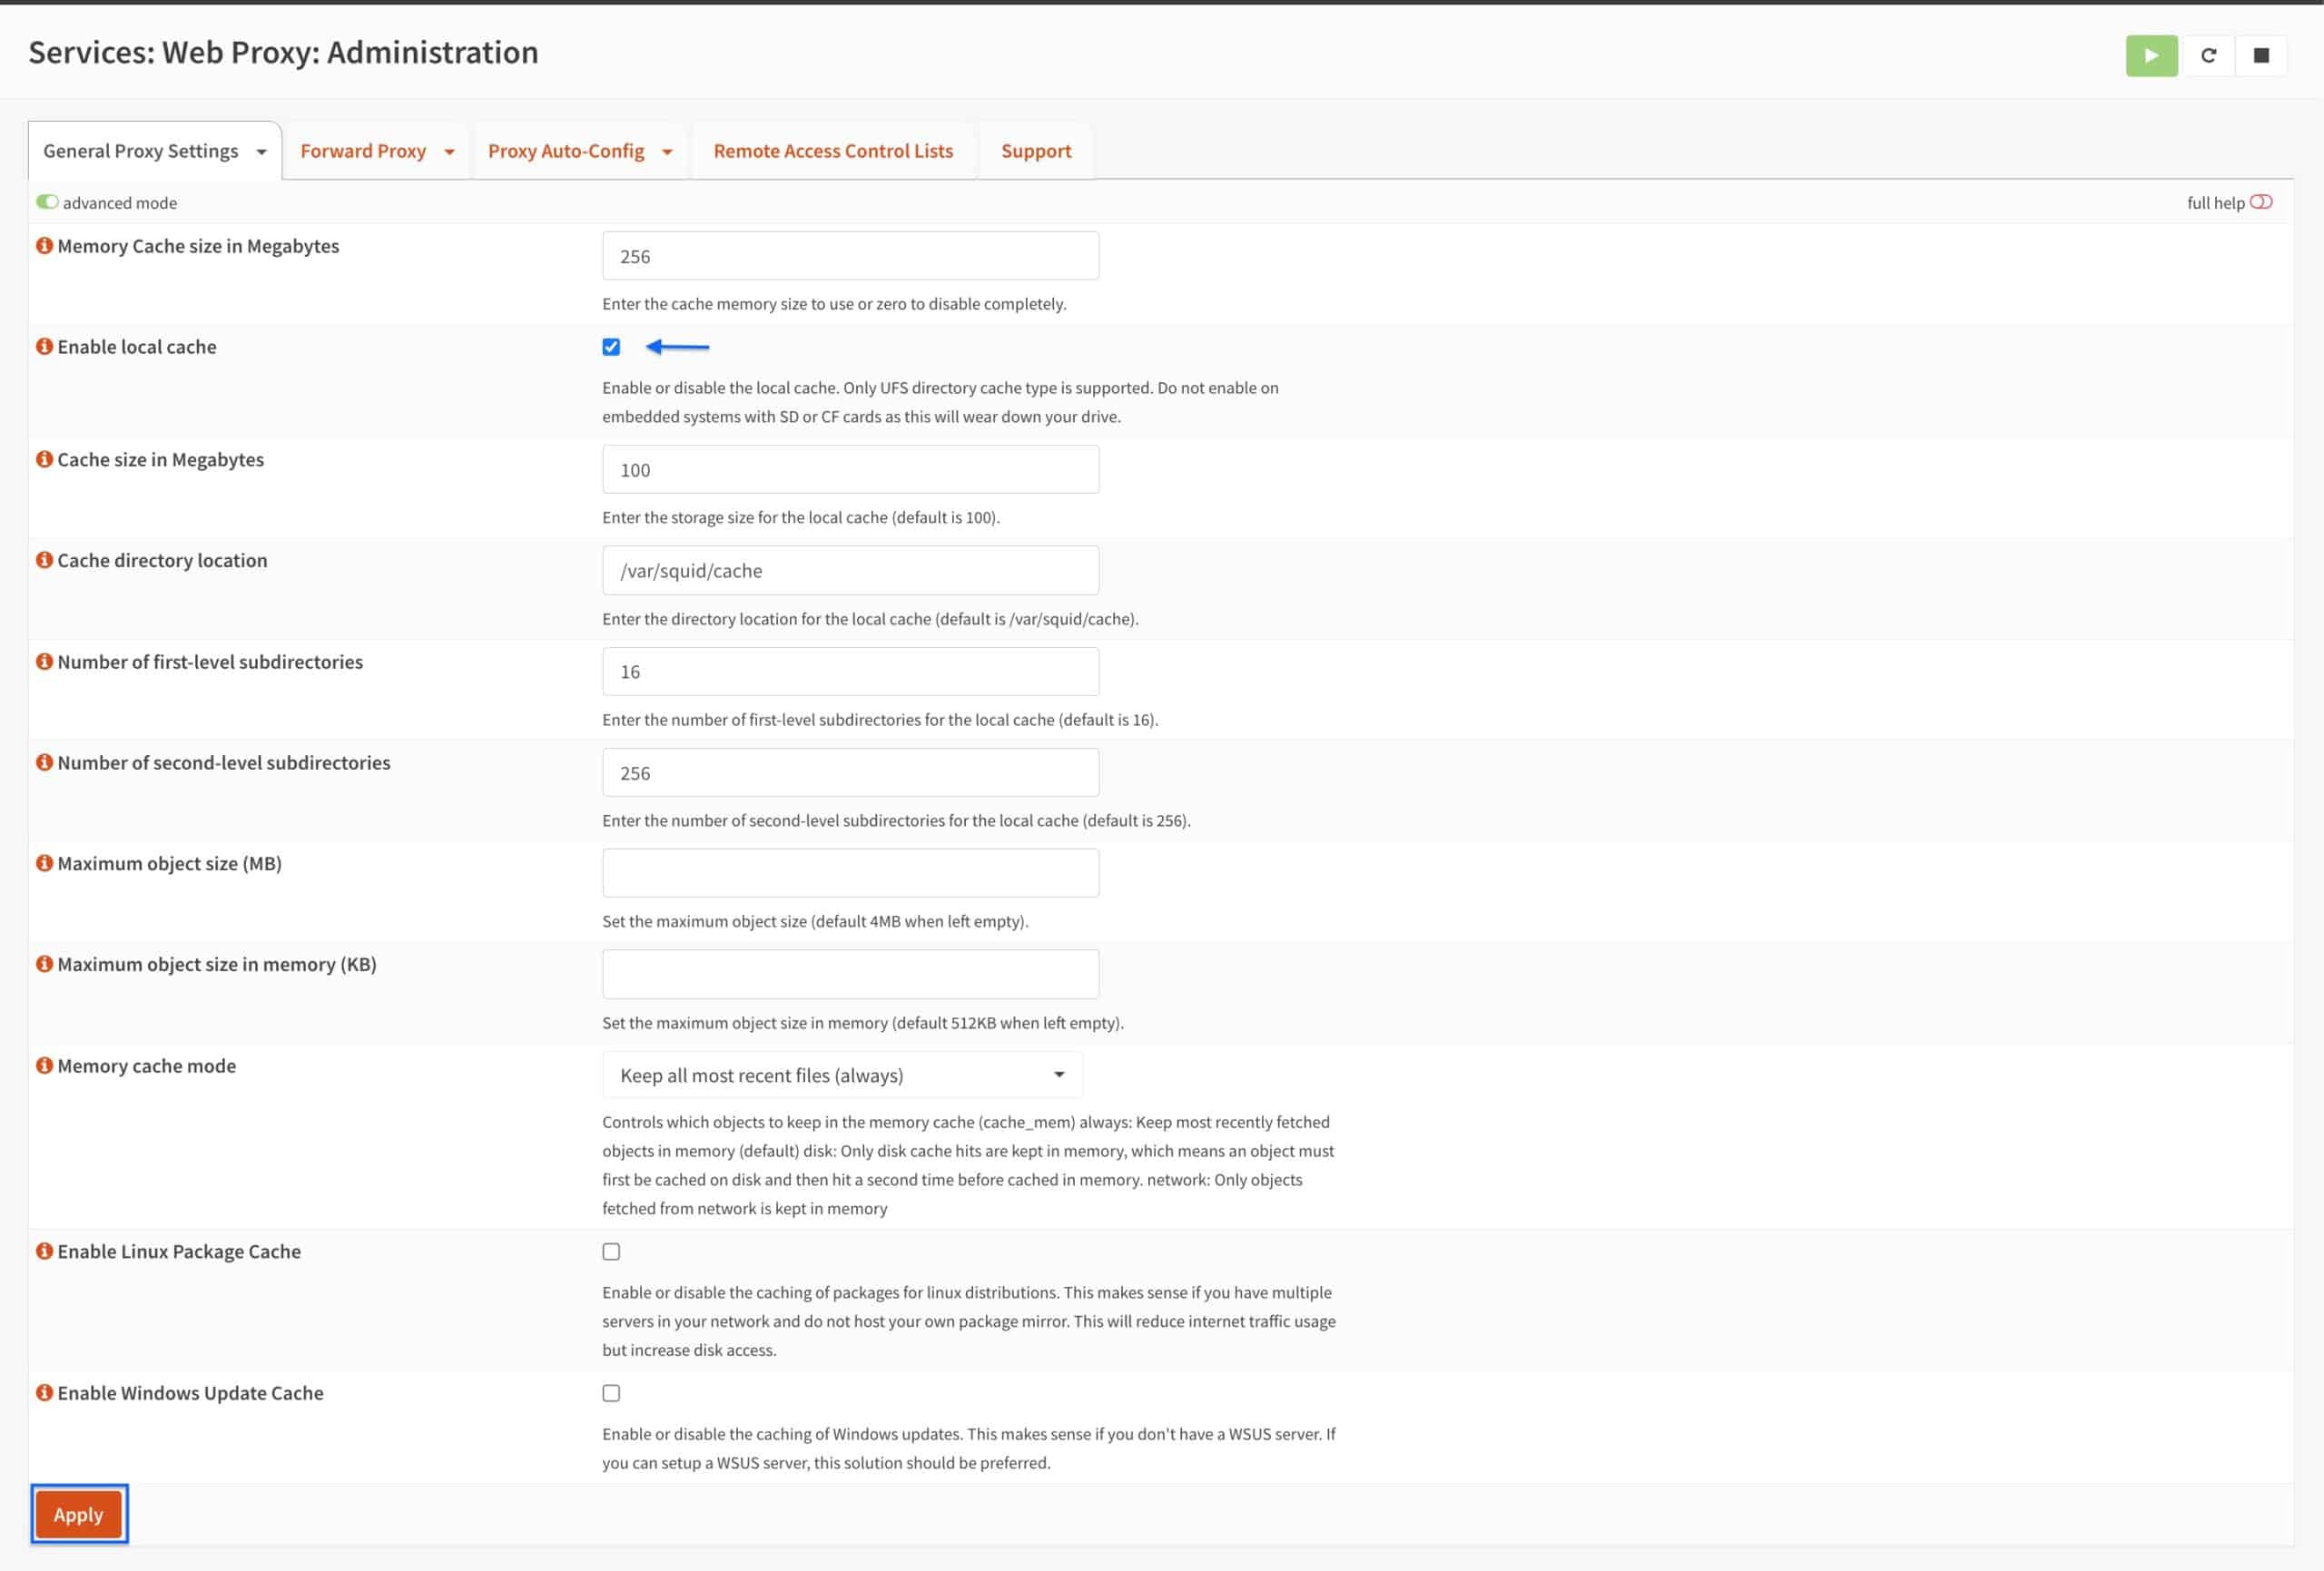
- Tick the Enable local cache box.
- Click Apply.
Forward Proxy
- Select the Forward Proxy tab. The General Forward Settings page is displayed.
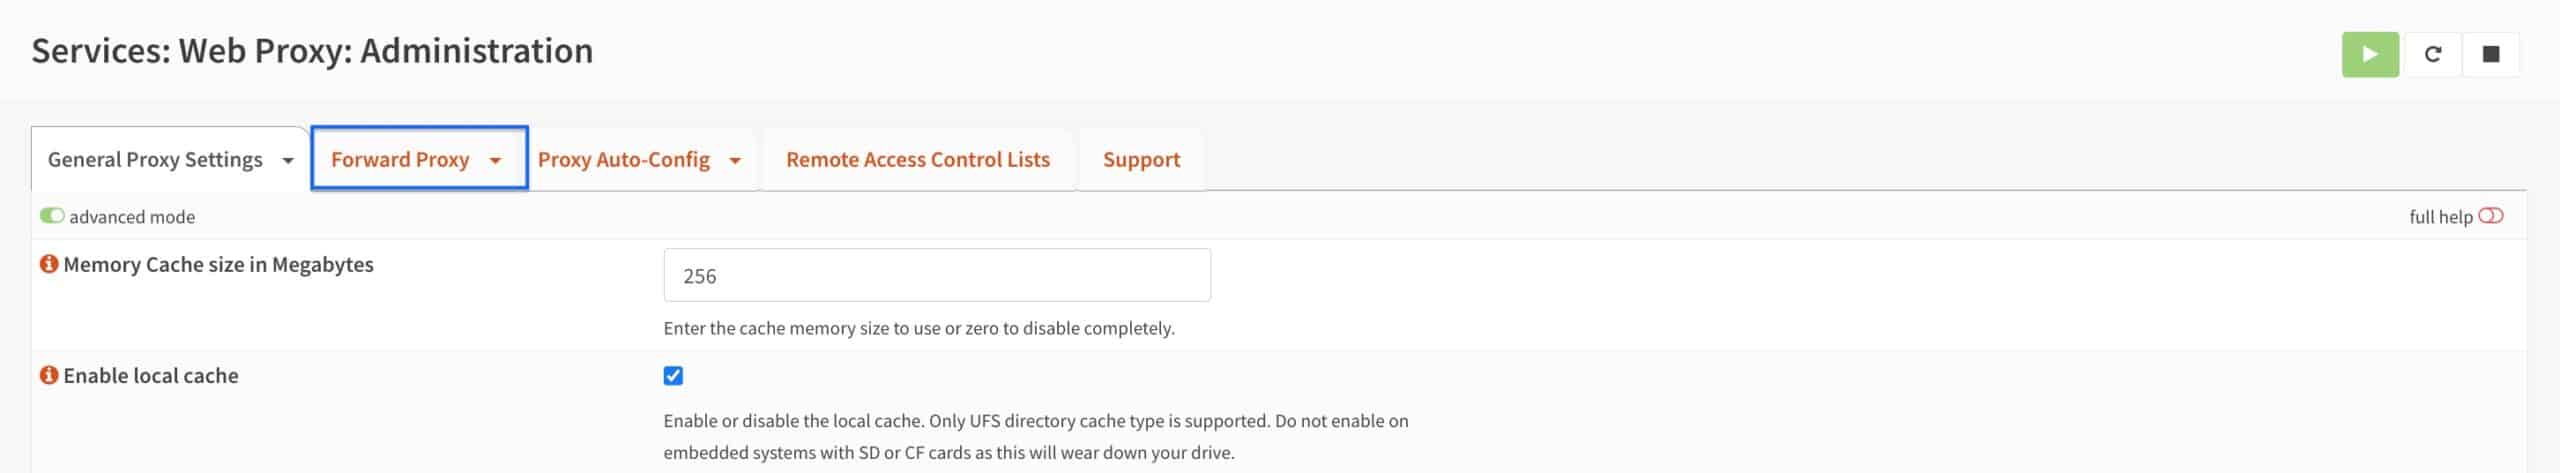
- From the Proxy Interfaces drop-down menu, select LAN (and any other LAN-type interfaces you want to proxy).
- Click Apply.
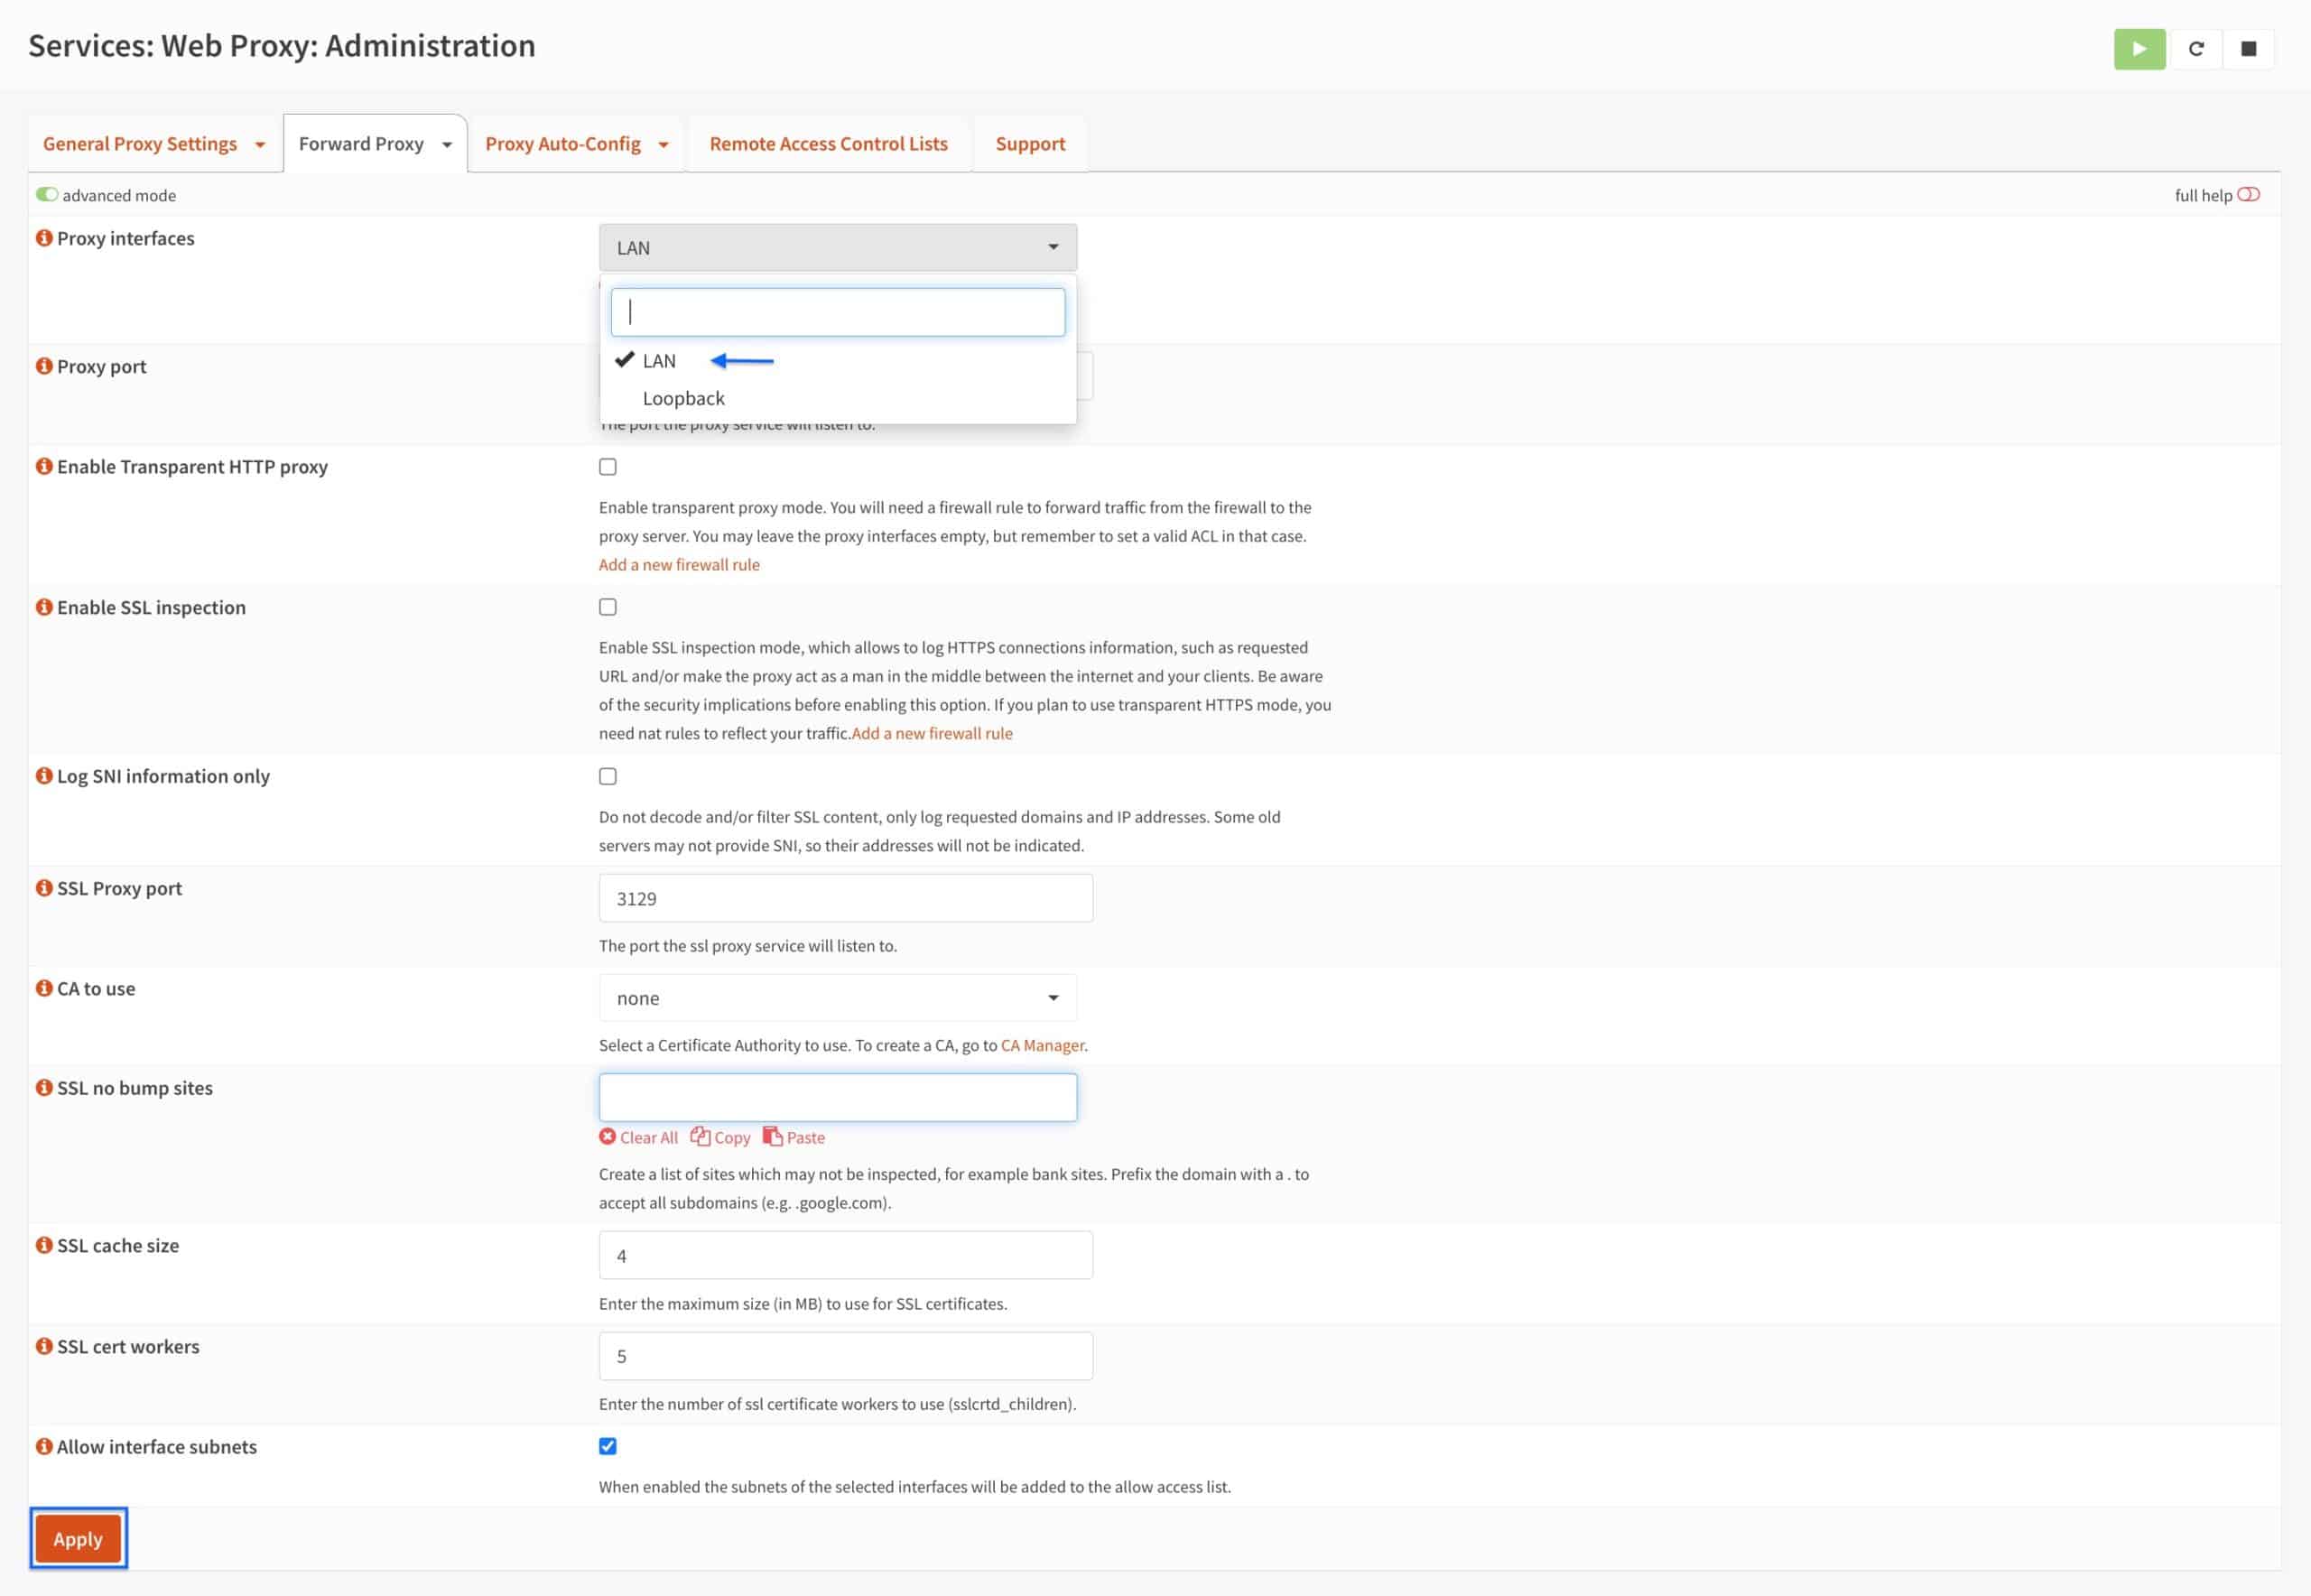
There are two settings on this page that we won’t be enabling, but that are still worth mentioning in the context of setting up a proxy server.
Enable Transparent HTTP proxy
Squid supports both explicit and transparent proxy modes.
This guide uses explicit mode because it supports both HTTP and HTTPS traffic. Transparent mode requires less client configuration but is generally less useful for modern web filtering because most websites use HTTPS.
Enable SSL Inspection
Squid can inspect HTTPS traffic by decrypting and re-encrypting connections using its own certificate. While this enables deeper filtering, it also introduces privacy, trust, and certificate-management concerns. We won’t be enabling SSL inspection in this guide.
Access control list
Squid is now configured. Our config is very basic at this stage, but Squid is enabled and working. It’s only configured for caching. Before we configure Squid for URL-list-based filtering (SquidGuard), we’ll need to give Squid domains to block. This is done from the Access Control List page.
- From the Forward Proxy tab drop-down menu, select Access Control List. The Access Control List page is displayed.
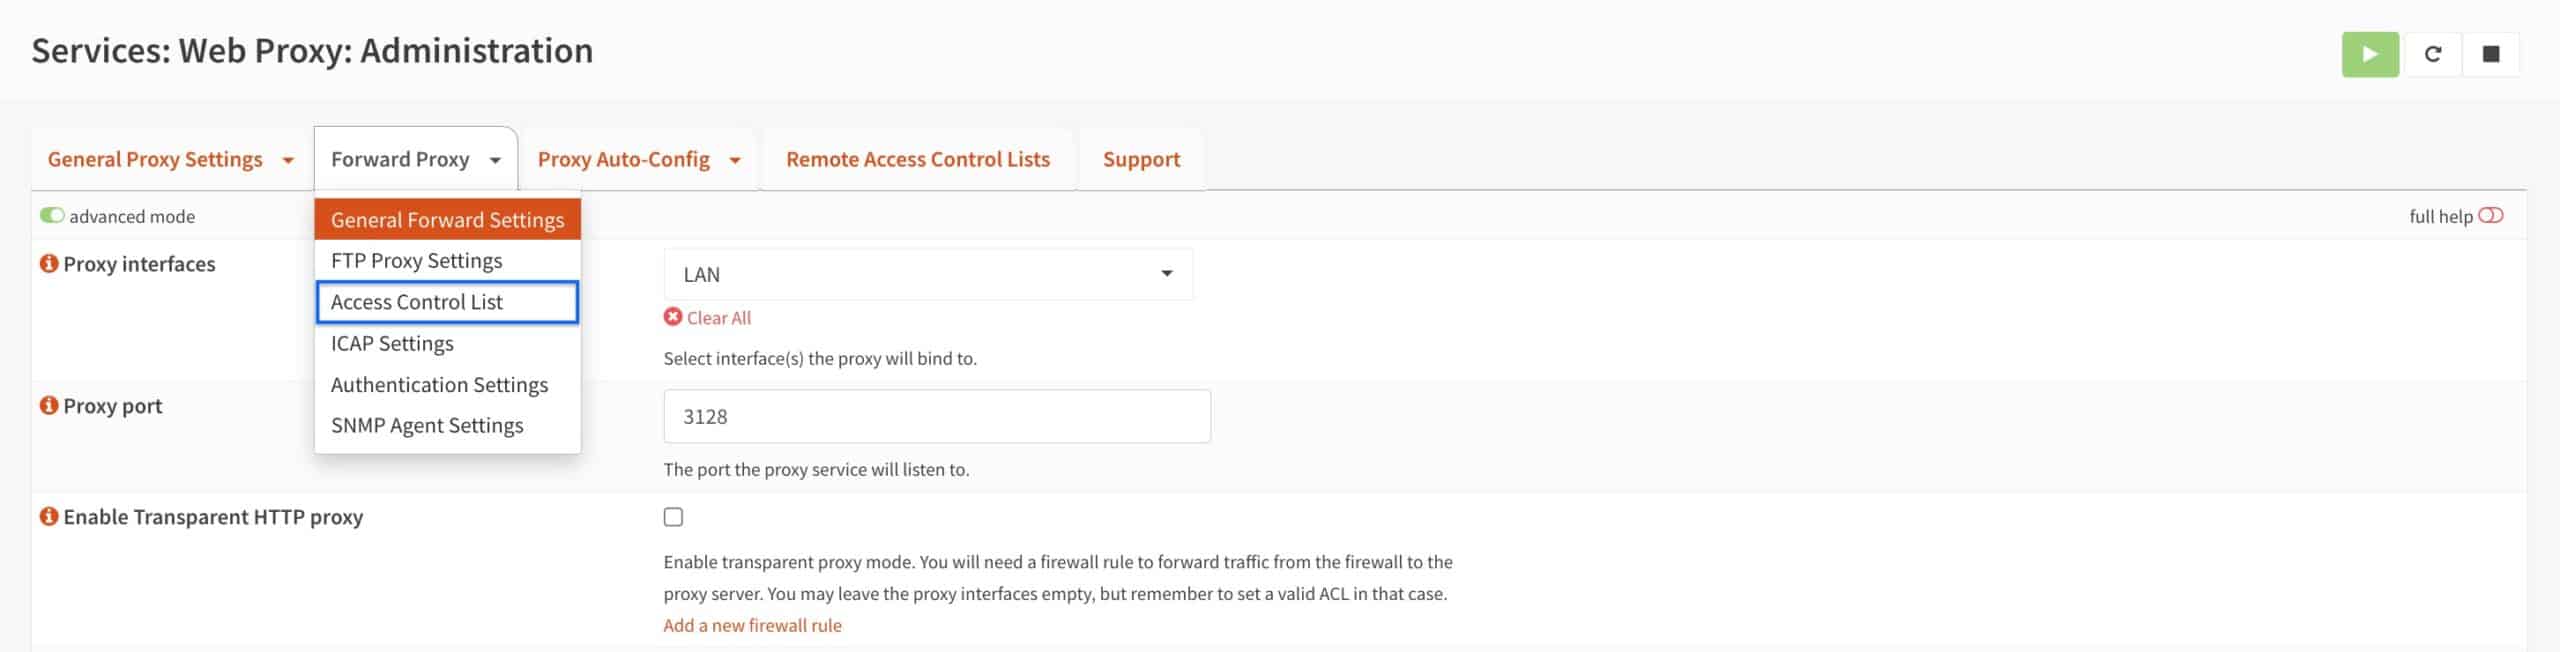
- The Access Control List page hosts multiple boxes in which we can define what to filter out.
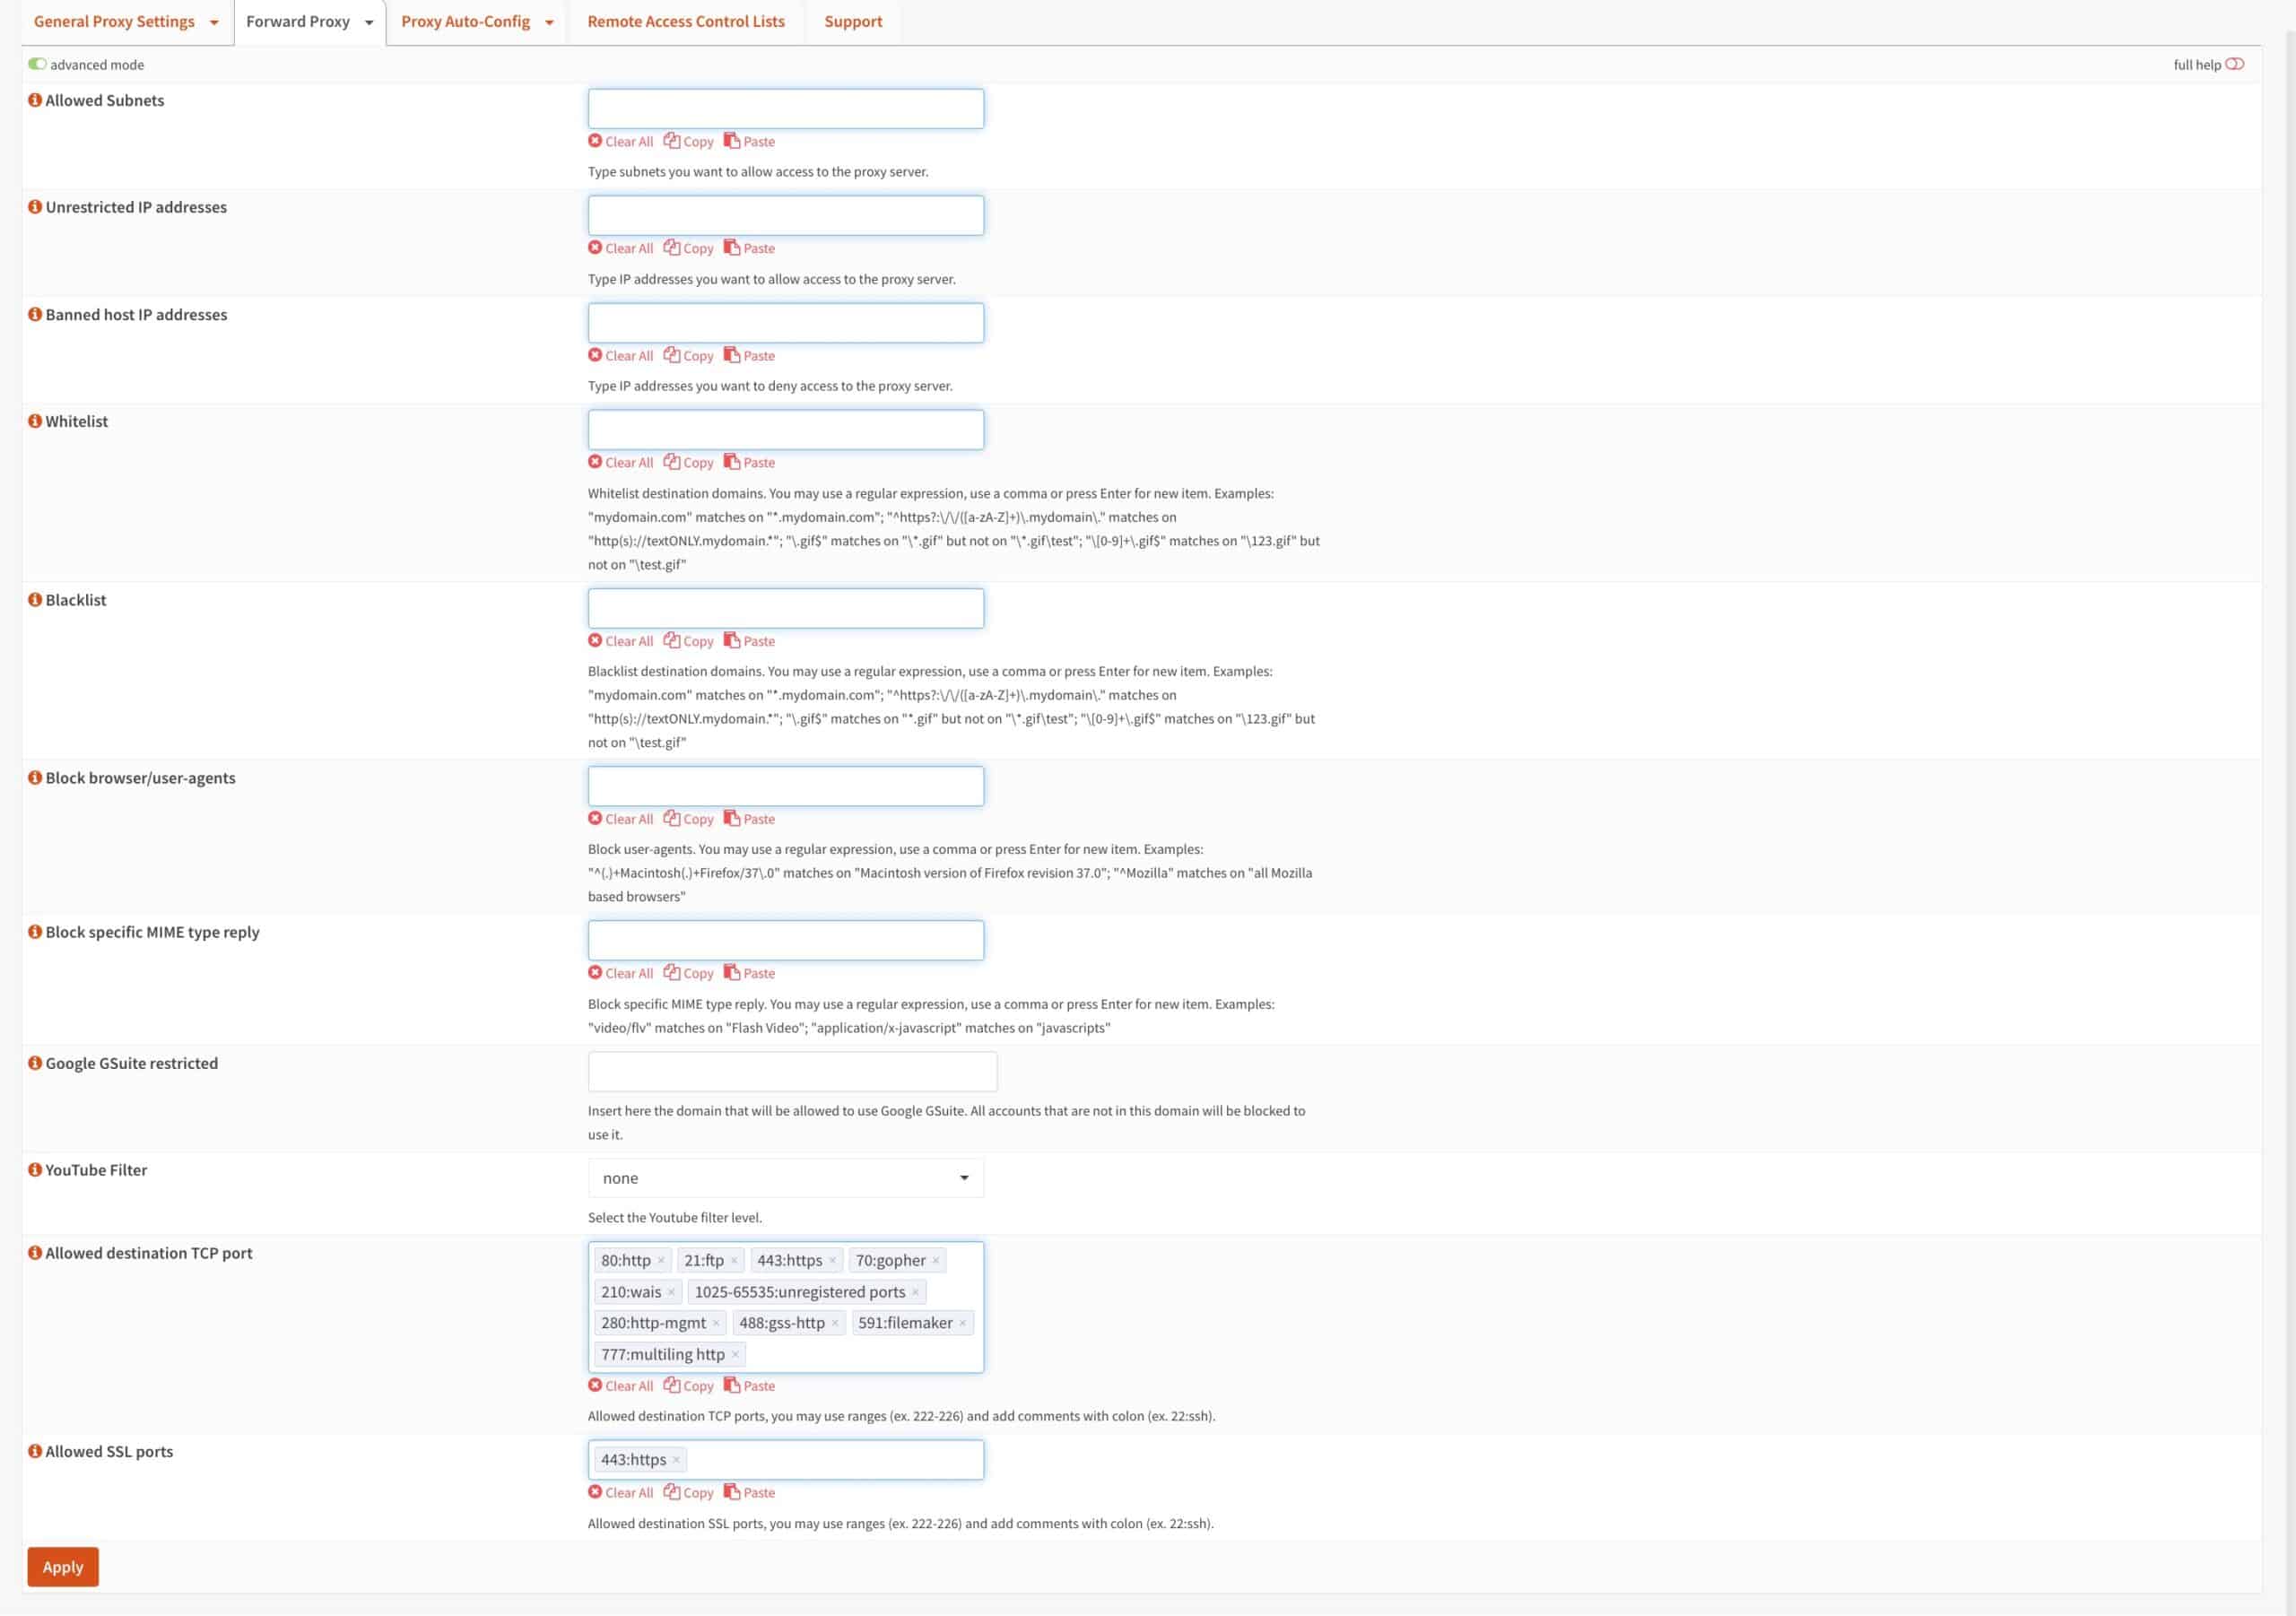
The Access Control List page contains options for:
- Allowing or denying specific subnets and IP addresses
- Creating domain whitelists and blacklists
- Blocking applications based on user agents
- Restricting MIME types
- Limiting destination ports
- Applying YouTube and Google Workspace restrictions
For this guide, we’ll focus only on domain blacklisting because it provides a simple way to verify that Squid is working before configuring URL-list filtering.
Testing Squid
Blacklisting an entry
To test our Squid installation and make sure everything is working correctly before moving on to the next steps, we’re going to enter a domain in the Blacklist box. If we set things up correctly, Squid should block any attempts to access that domain.
- On the Access Control List page, enter facebook.com in the Blacklist box and click Apply.
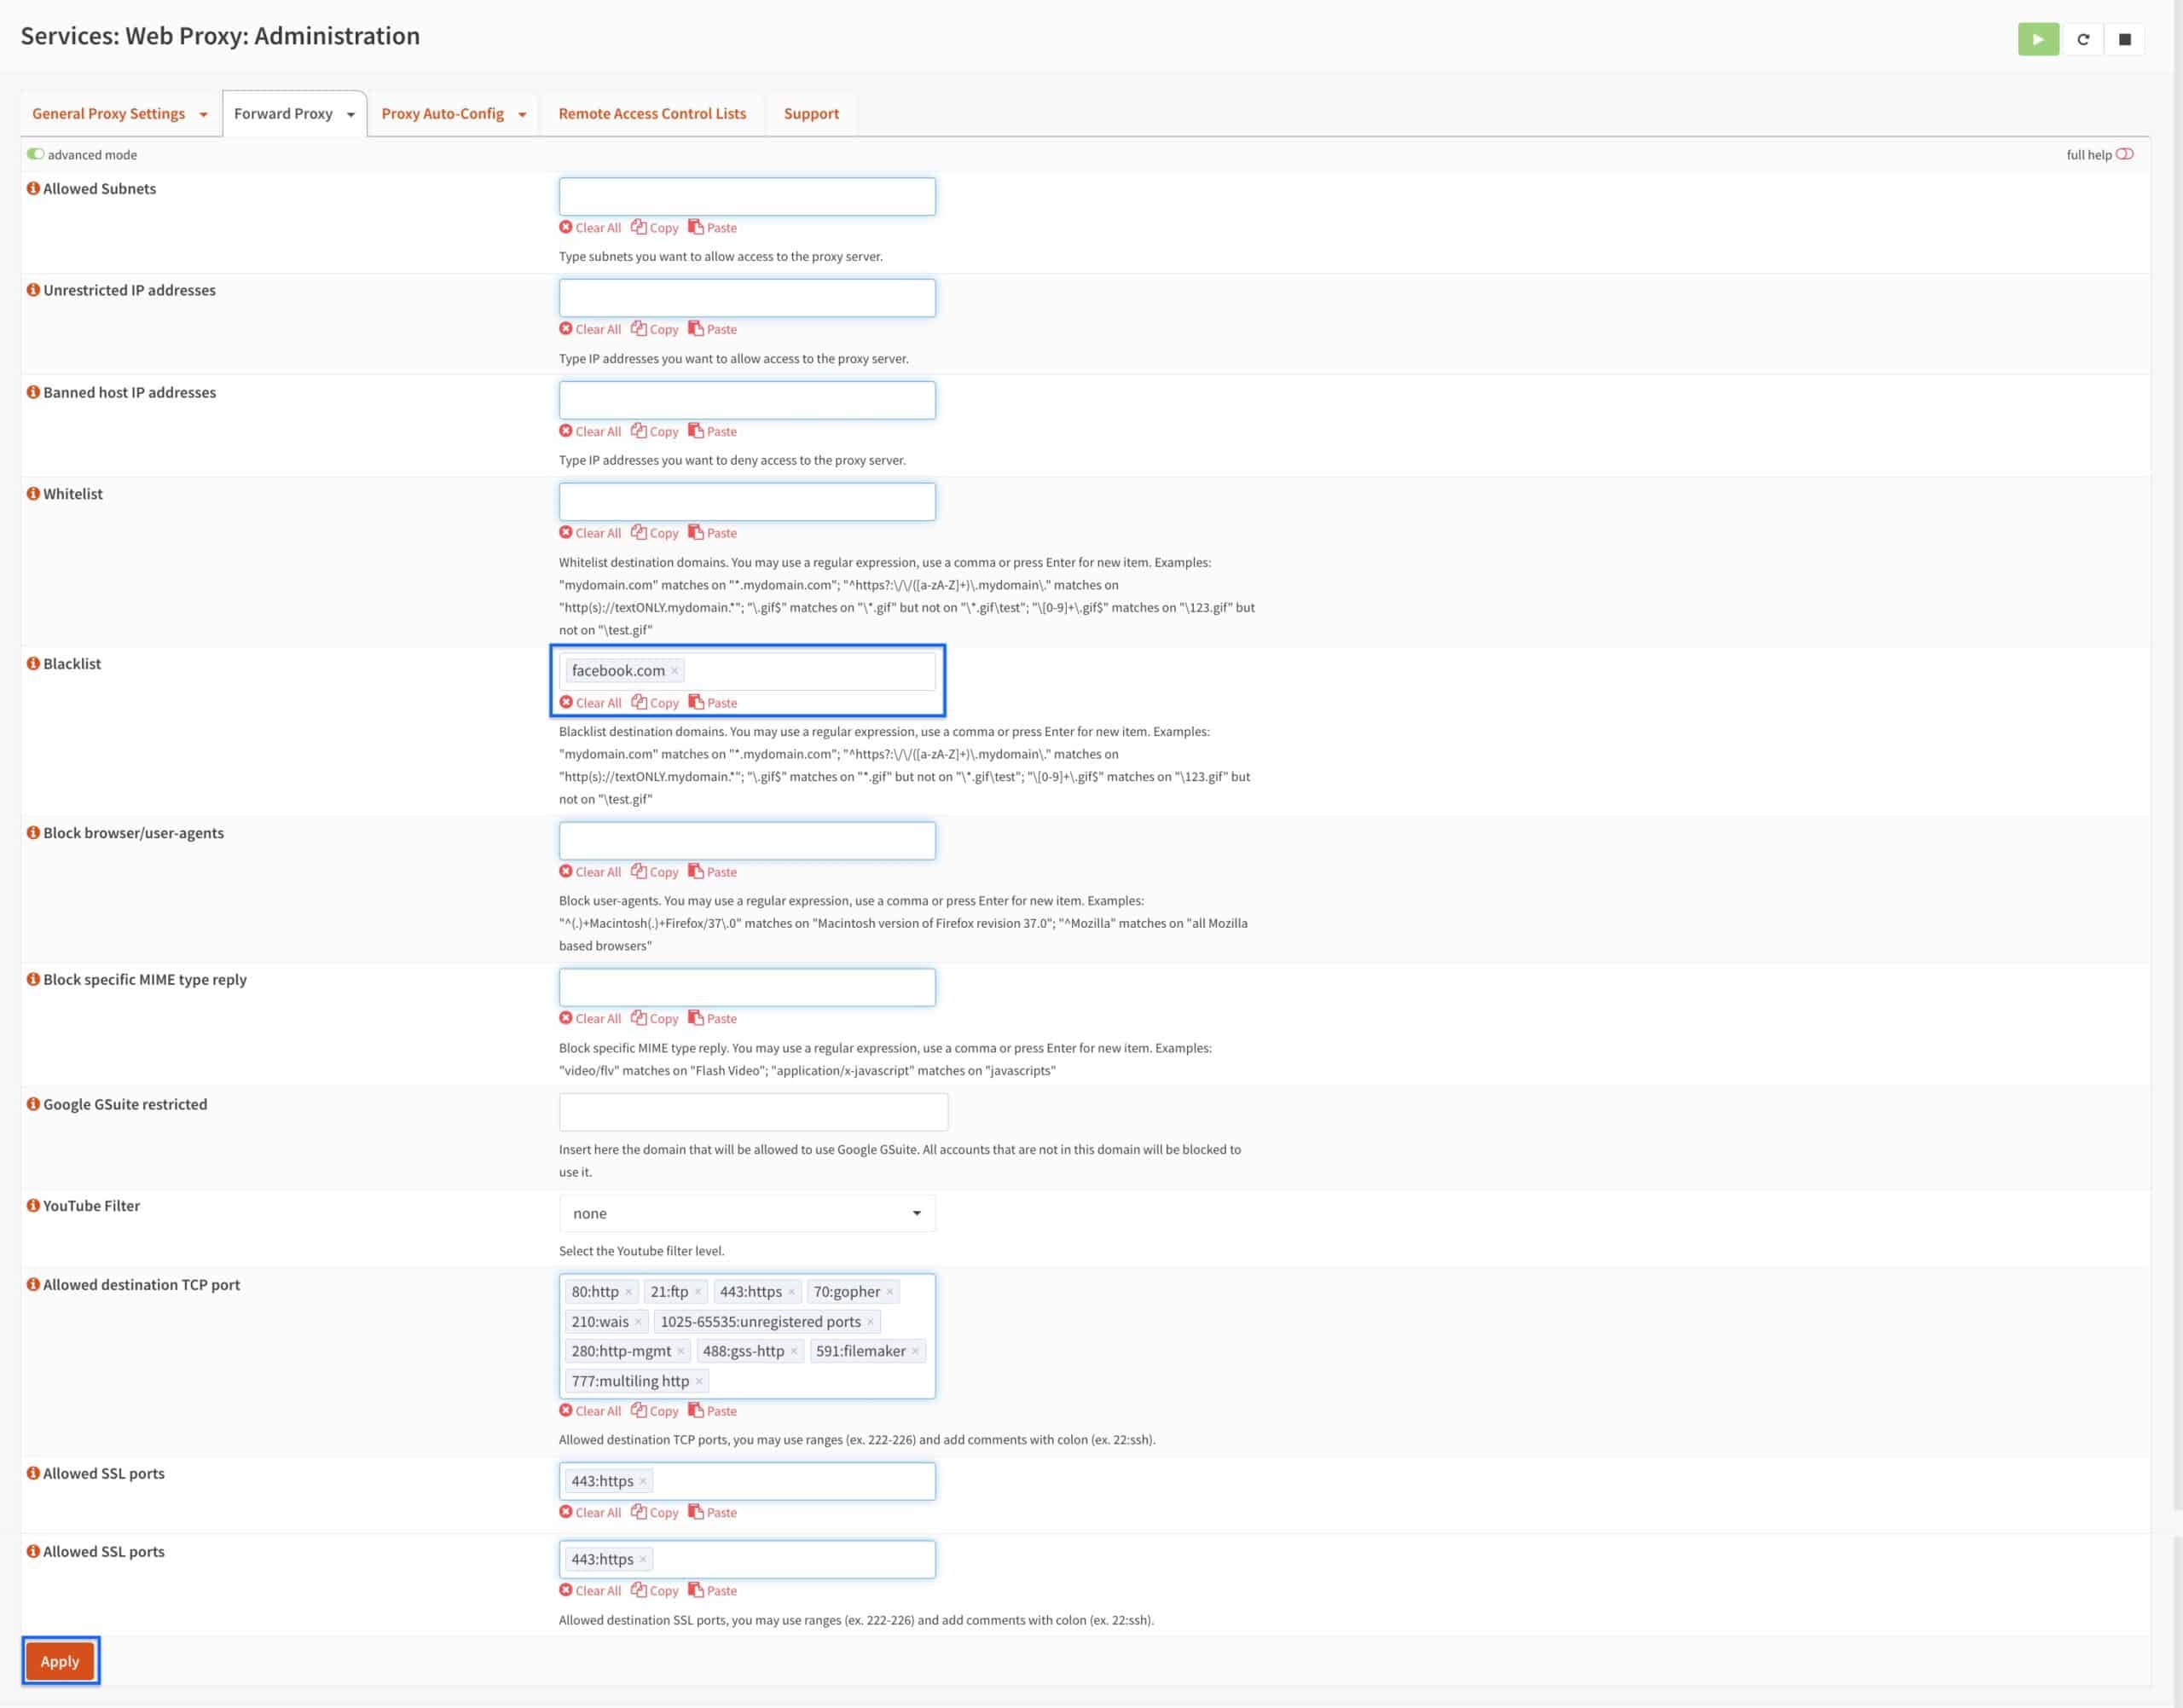
We’ve configured Squid to block facebook.com. The next thing we need to do is configure our web browser to use the proxy server so we can see if it’s working properly. If it is, Squid should block access to facebook.com.
Configuring Firefox to use Squid
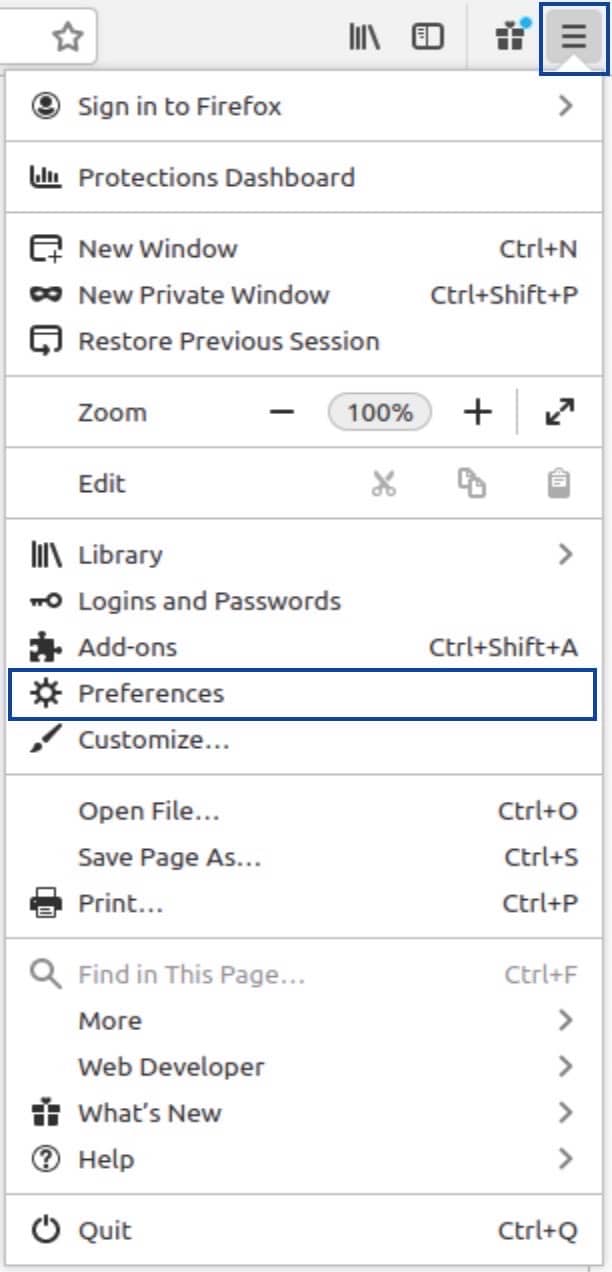
- Launch Firefox and click the Settings icon at the top right of the UI. Select Preferences (or Options in Windows). This displays the General Settings page.
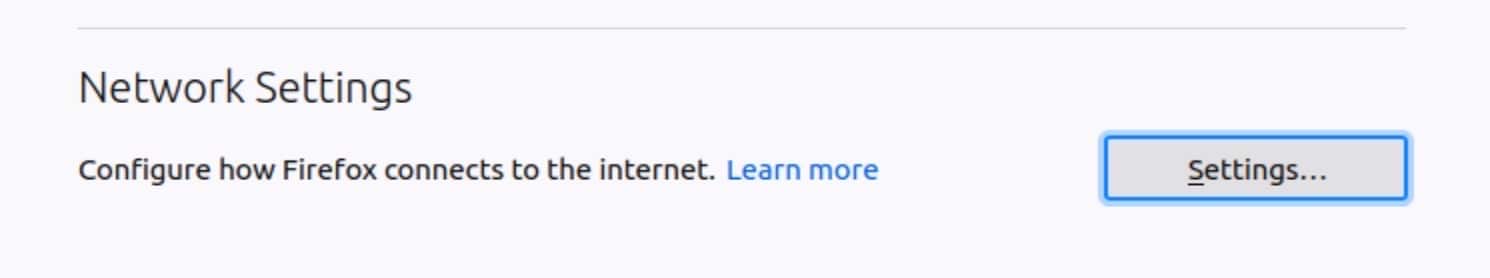
- Scroll down the General Settings until you see Network Settings, and click the Settings button.
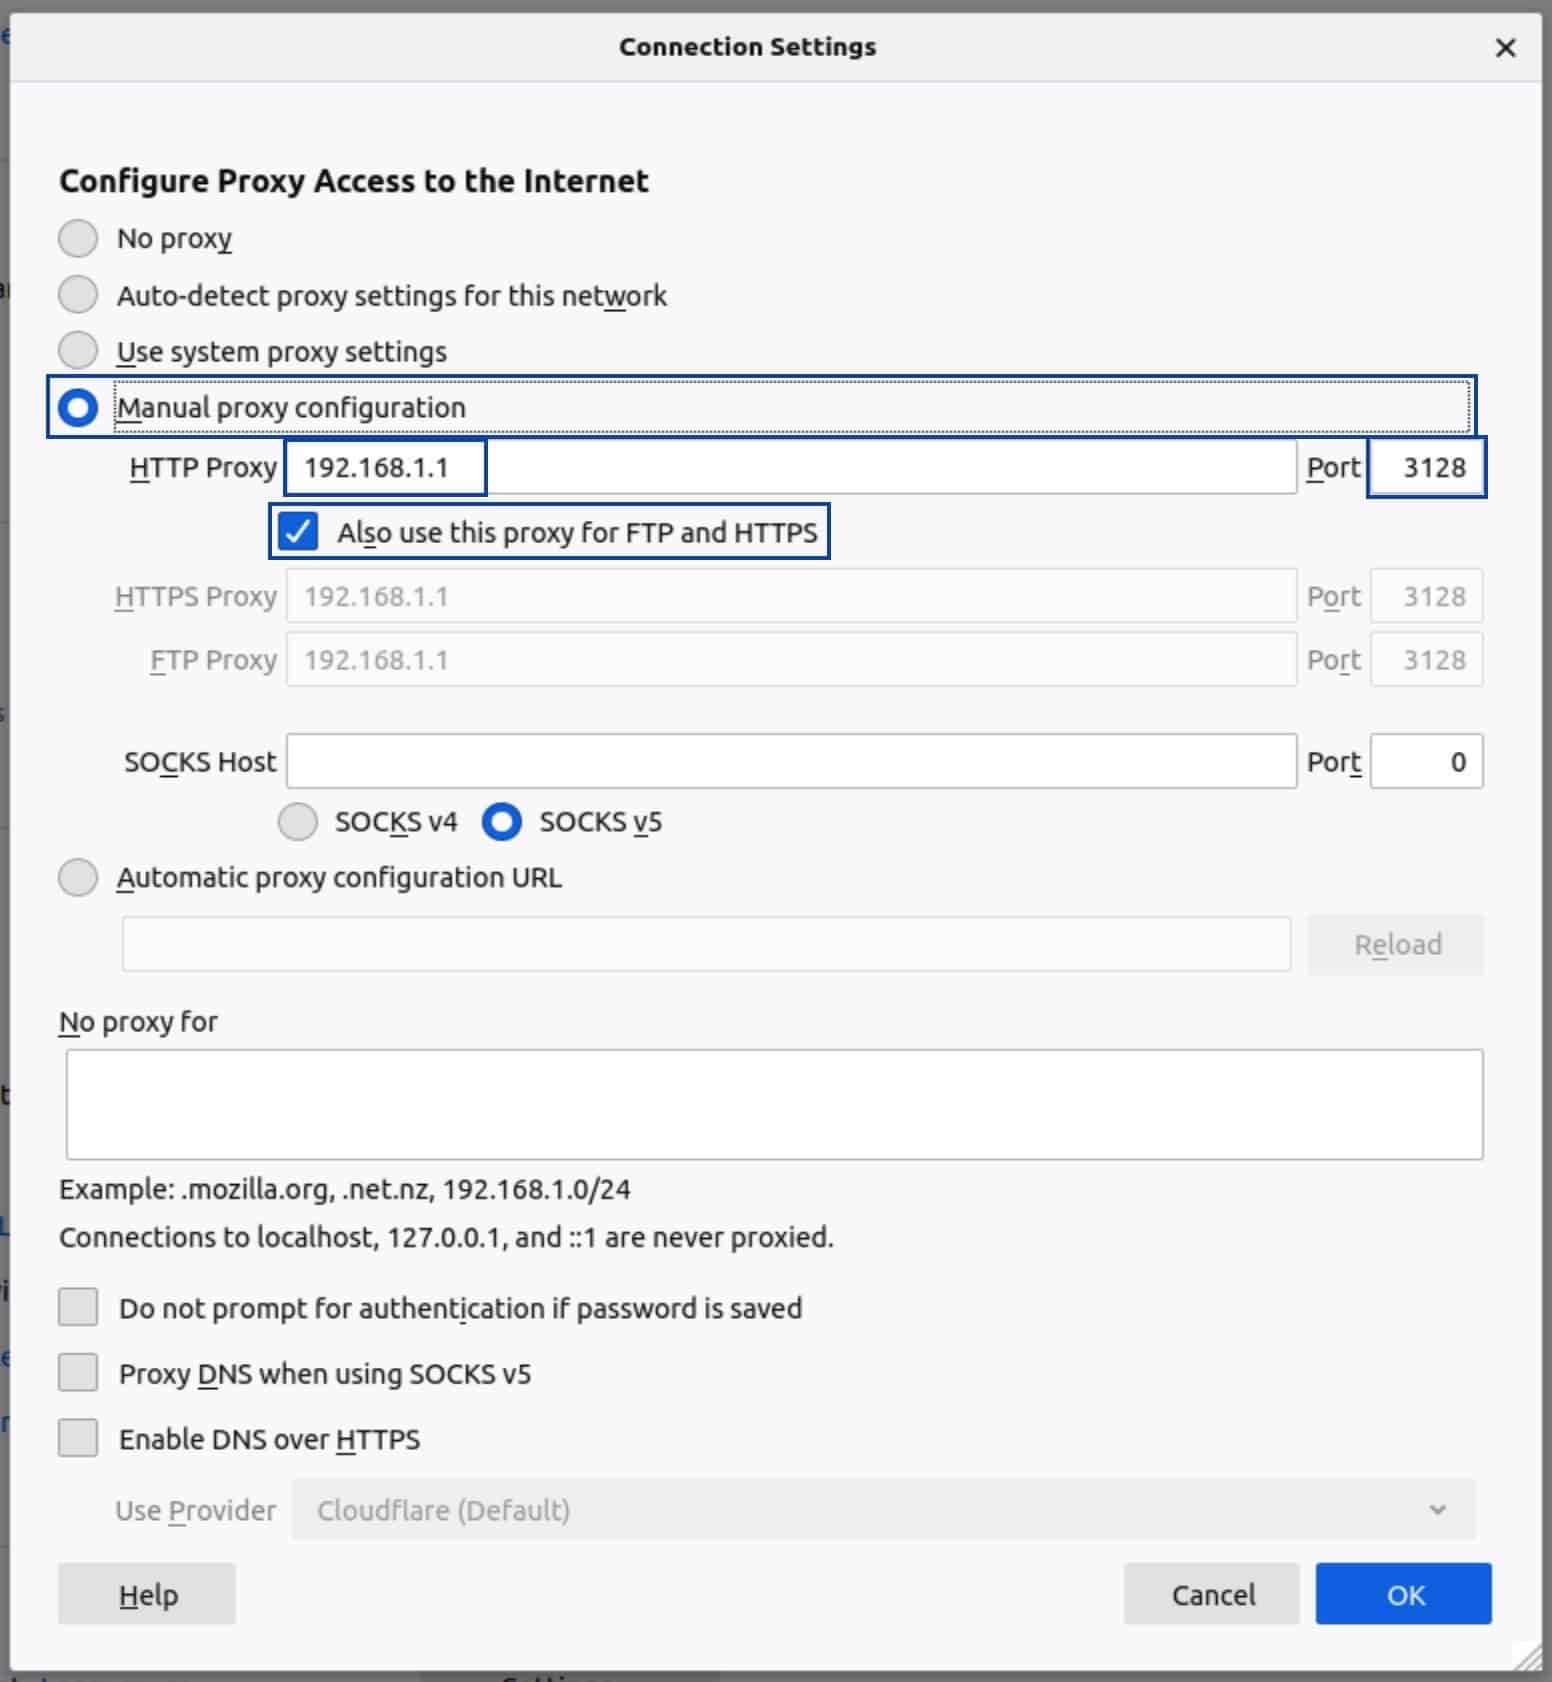
- Select Manual Proxy Configuration.
- In the HTTP Proxy box, enter your OPNsense box’s IP address. The default is 192.168.1.1.
- Enter 3128 in the Port field.
- Check the Also use this proxy for FTP and HTTPS box.
- Click OK at the bottom of the menu, and exit the Settings page.
Now, when I try to access facebook.com – whether over HTTP or HTTPS – I get the following error:
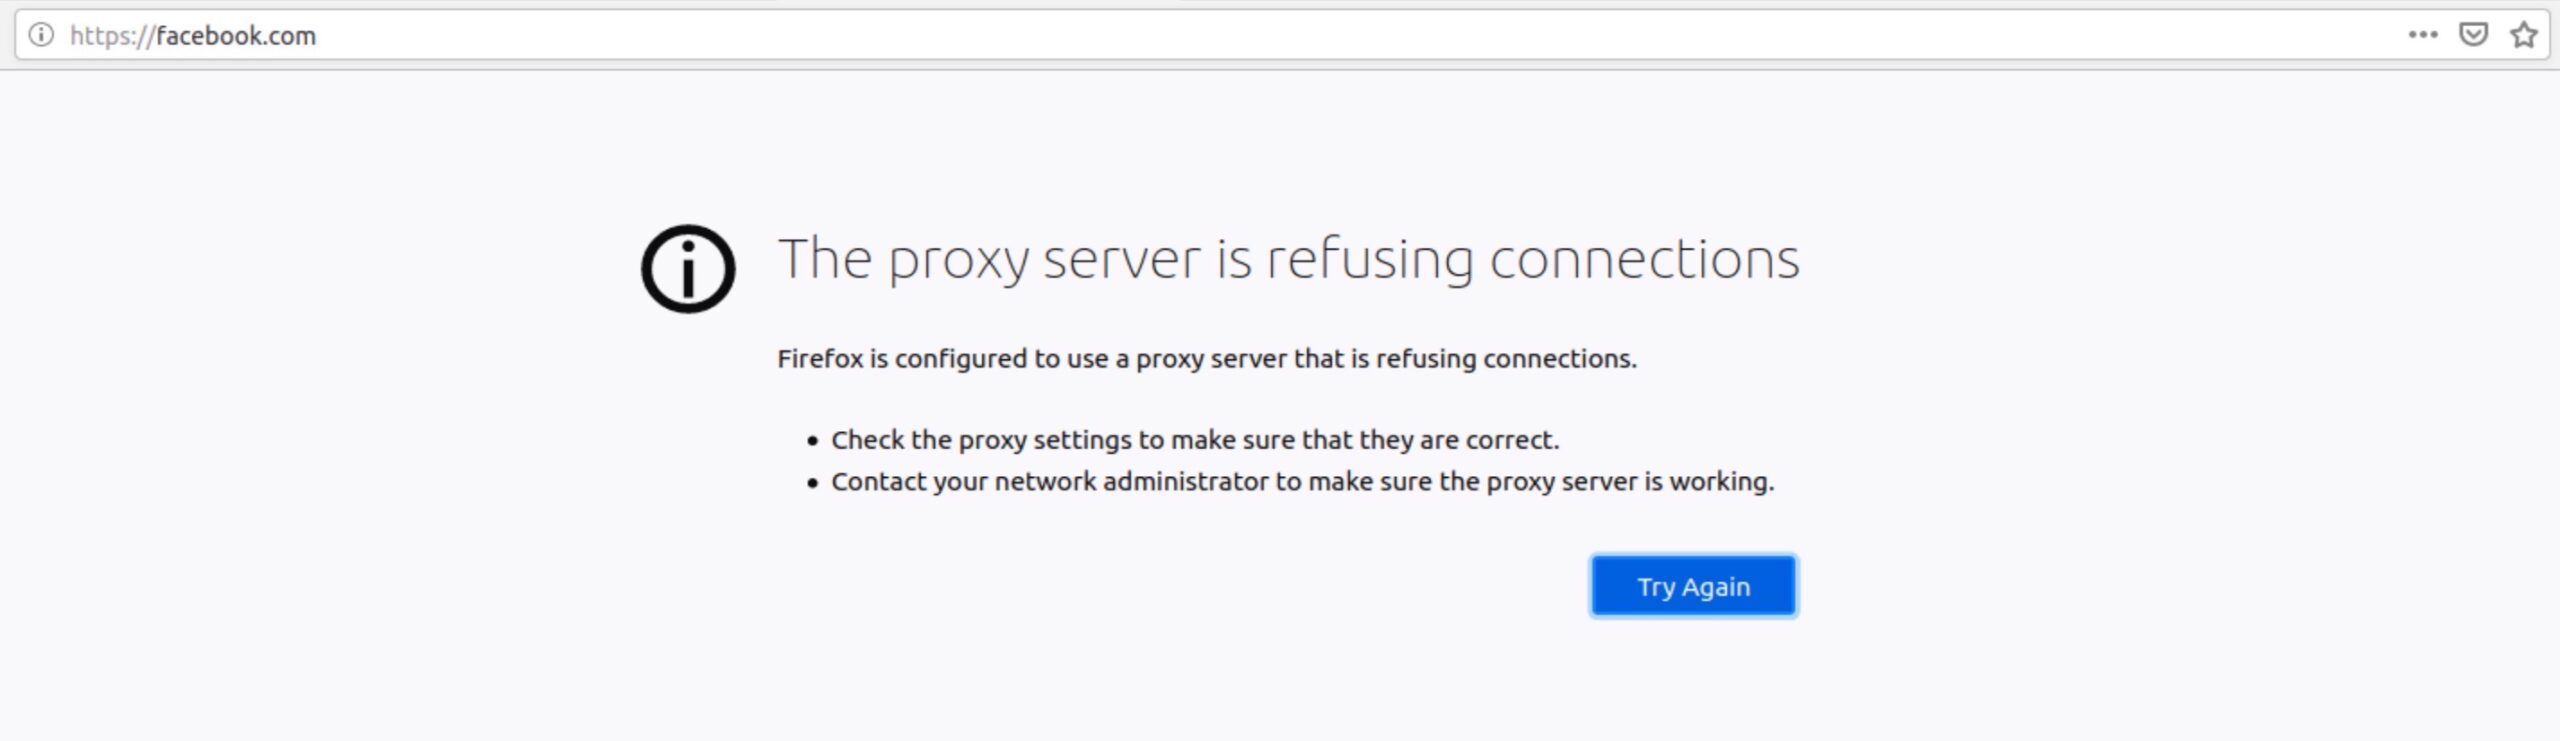
And that’s exactly what I wanted. Squid is working properly.
The SquidGuard part
So our proxy server is working and configured to block Facebook, but if we were to block ads this way, we’d have to add a massive amount of domains to Squid’s Blacklist. This is far from ideal.
That’s what SquidGuard is for. In pfSense, you need to install the SquidGuard package to get that functionality. But, as mentioned previously, it’s baked into OPNsense’s Squid implementation. We can configure URL list-based filtering straight from Squid’s settings.
Configuring URL list-based filtering in Squid
- From the Squid settings pages, select the Remote Access Control Lists tab. The Remote Access Control Lists page is displayed.
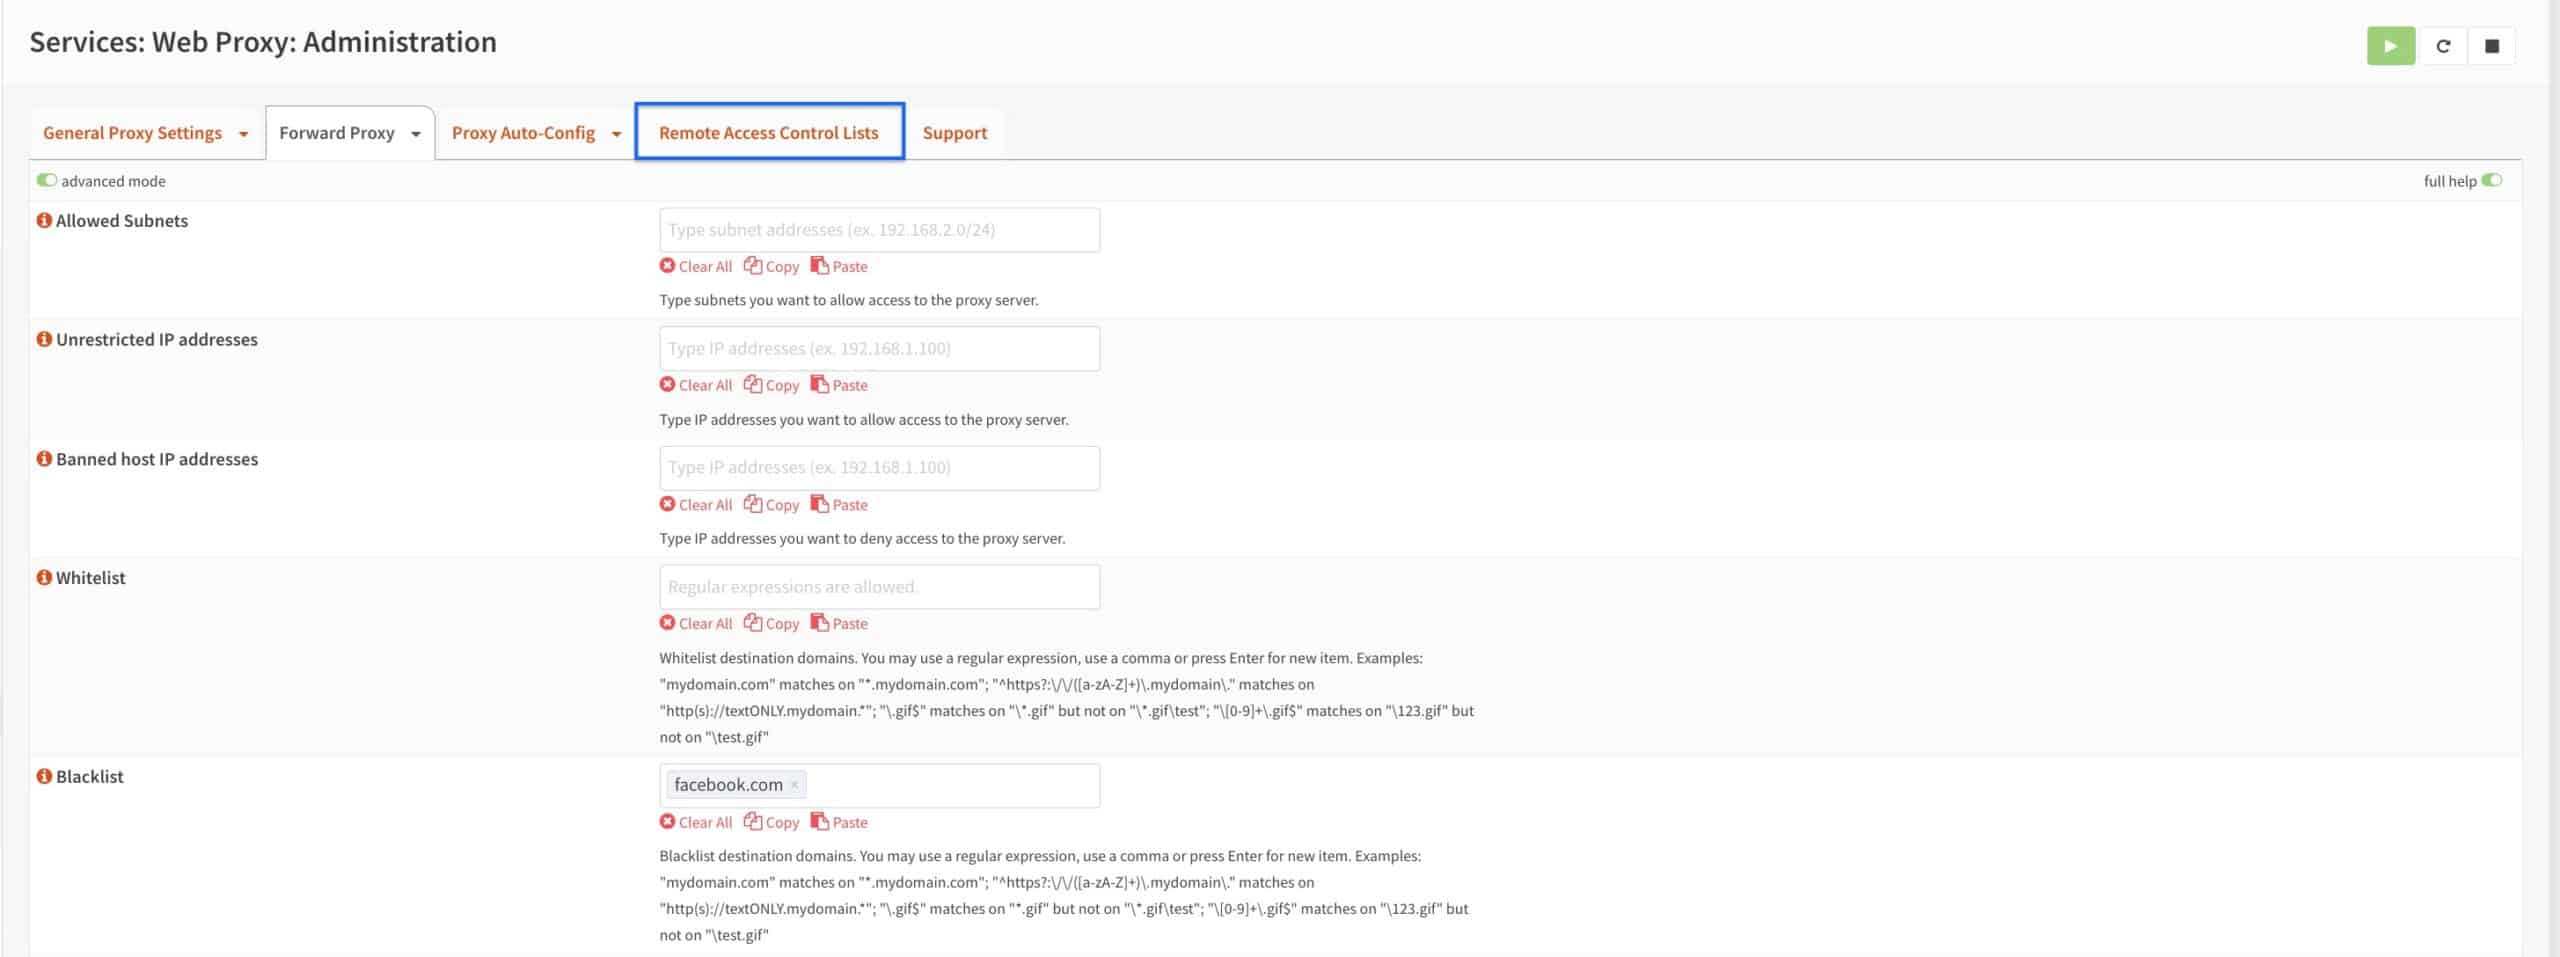
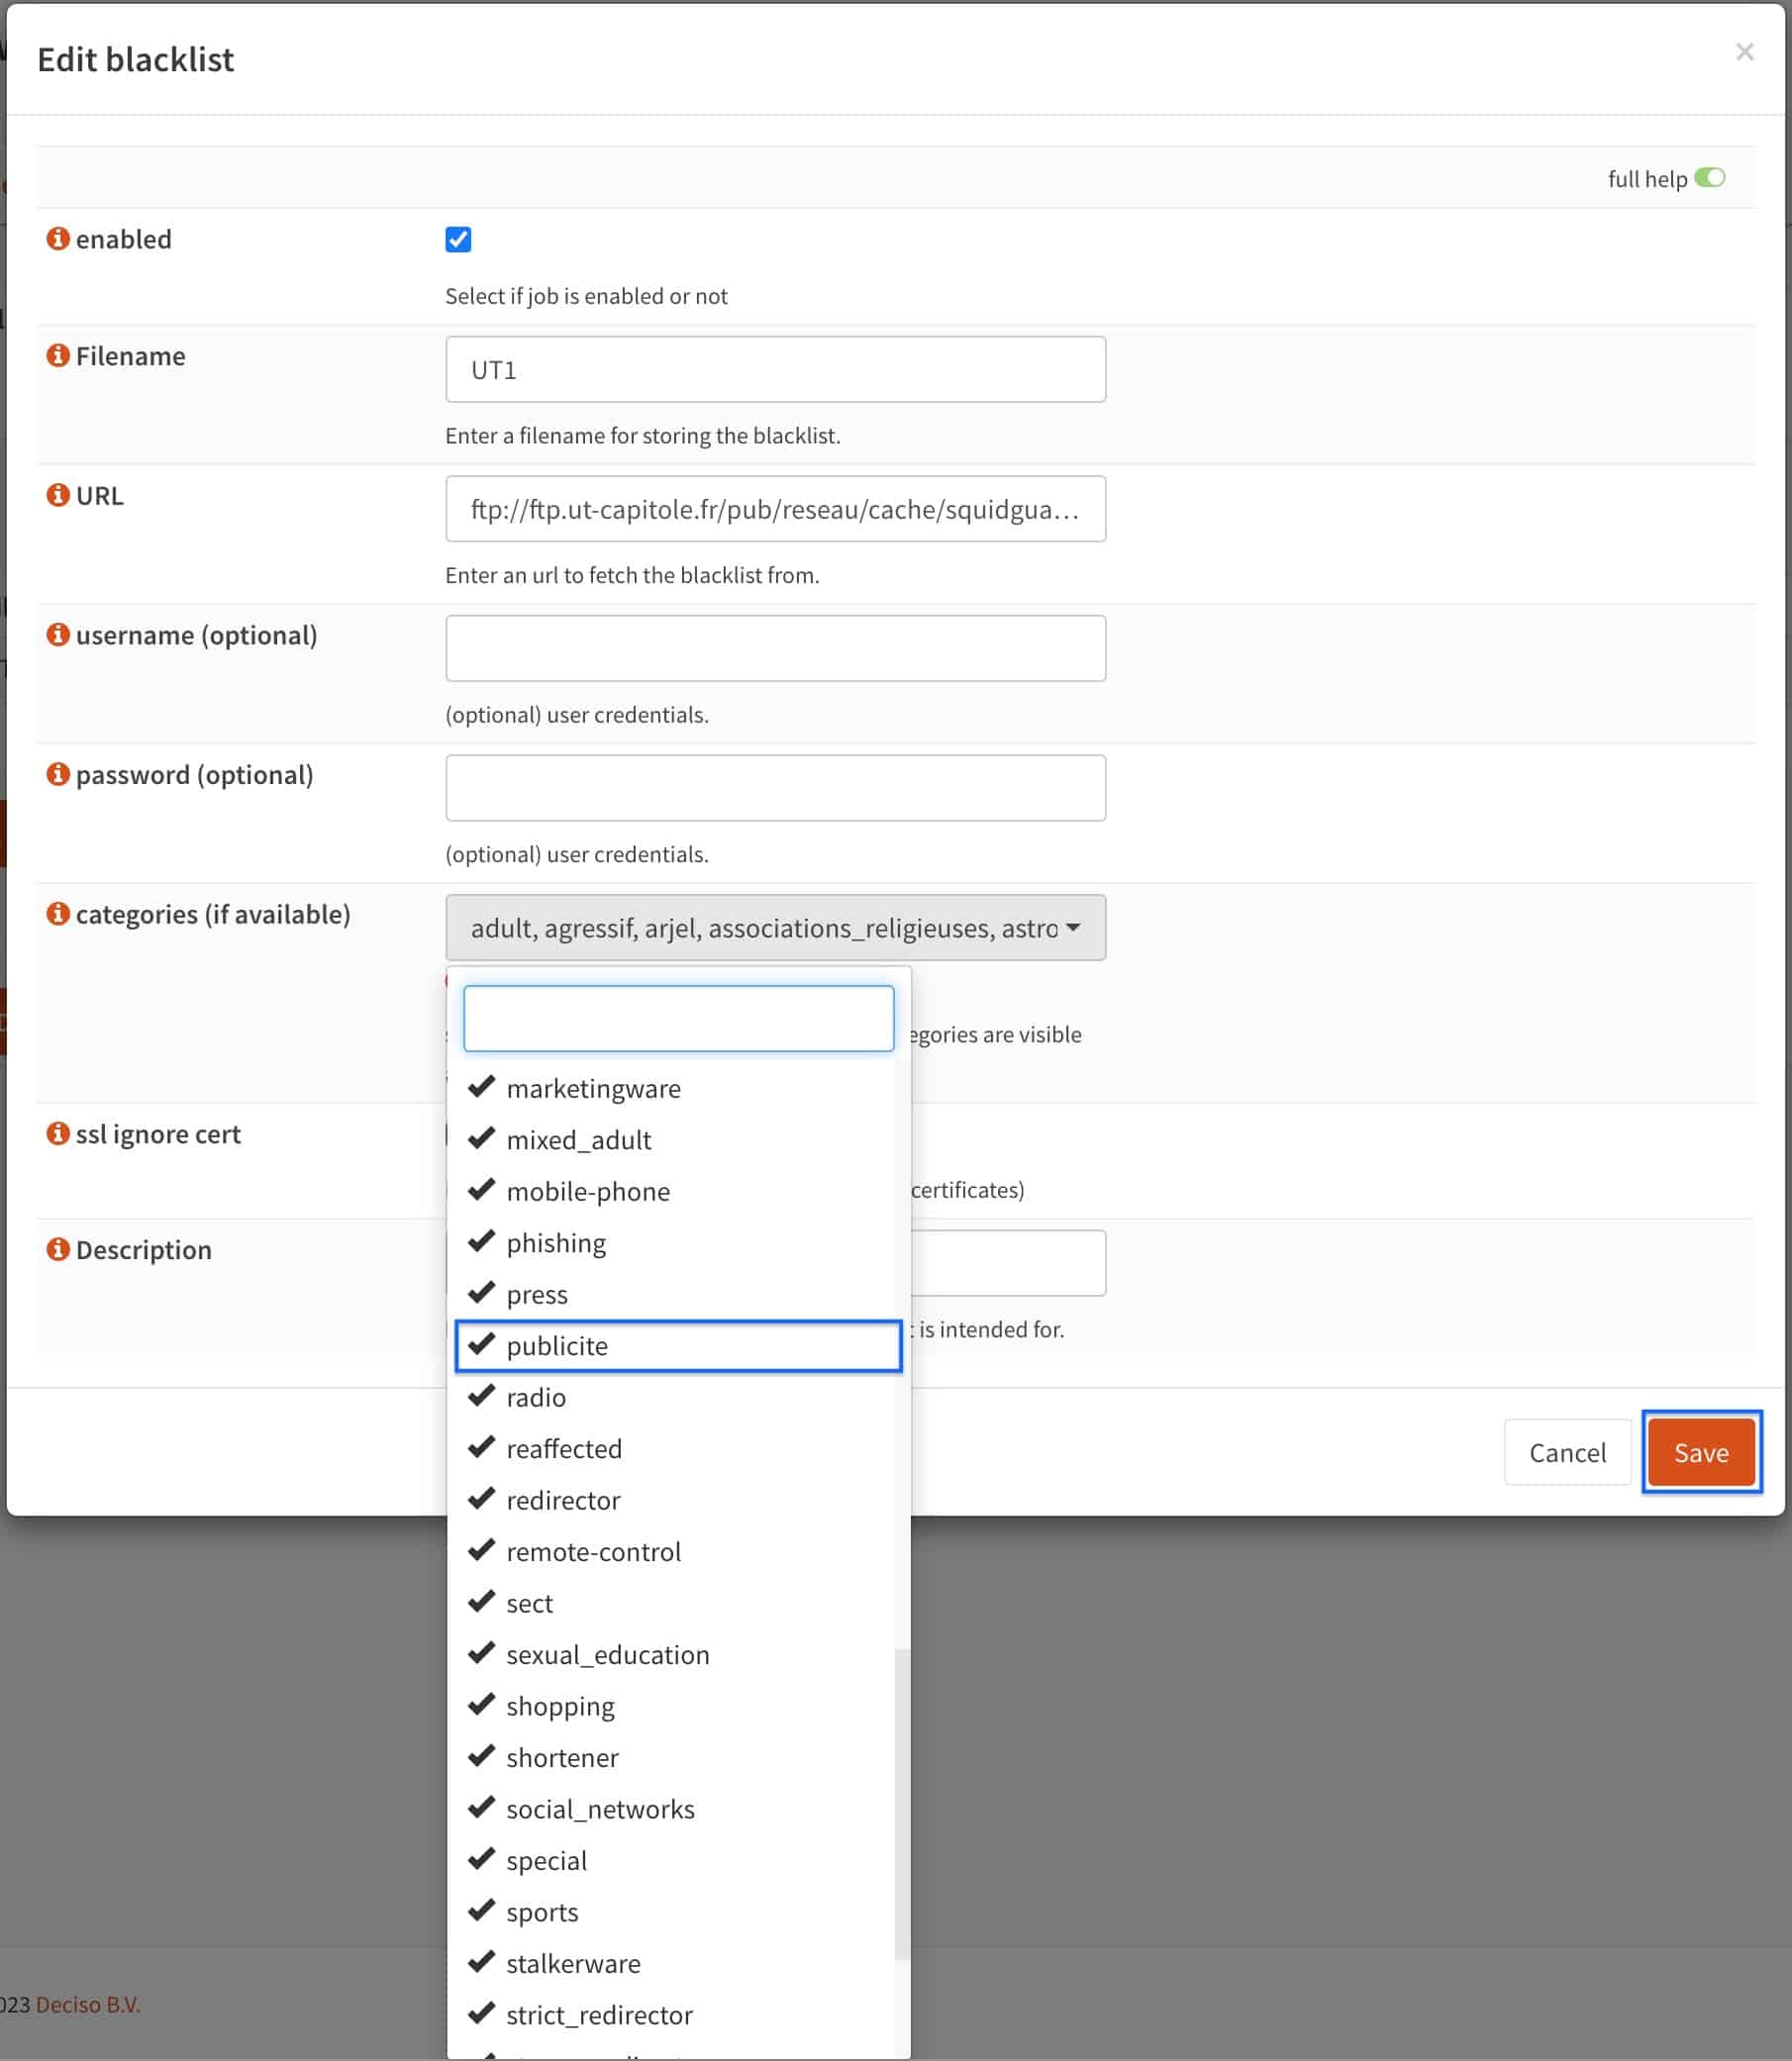
- The page is empty by default. Click on the + sign to add a new remote access control list.
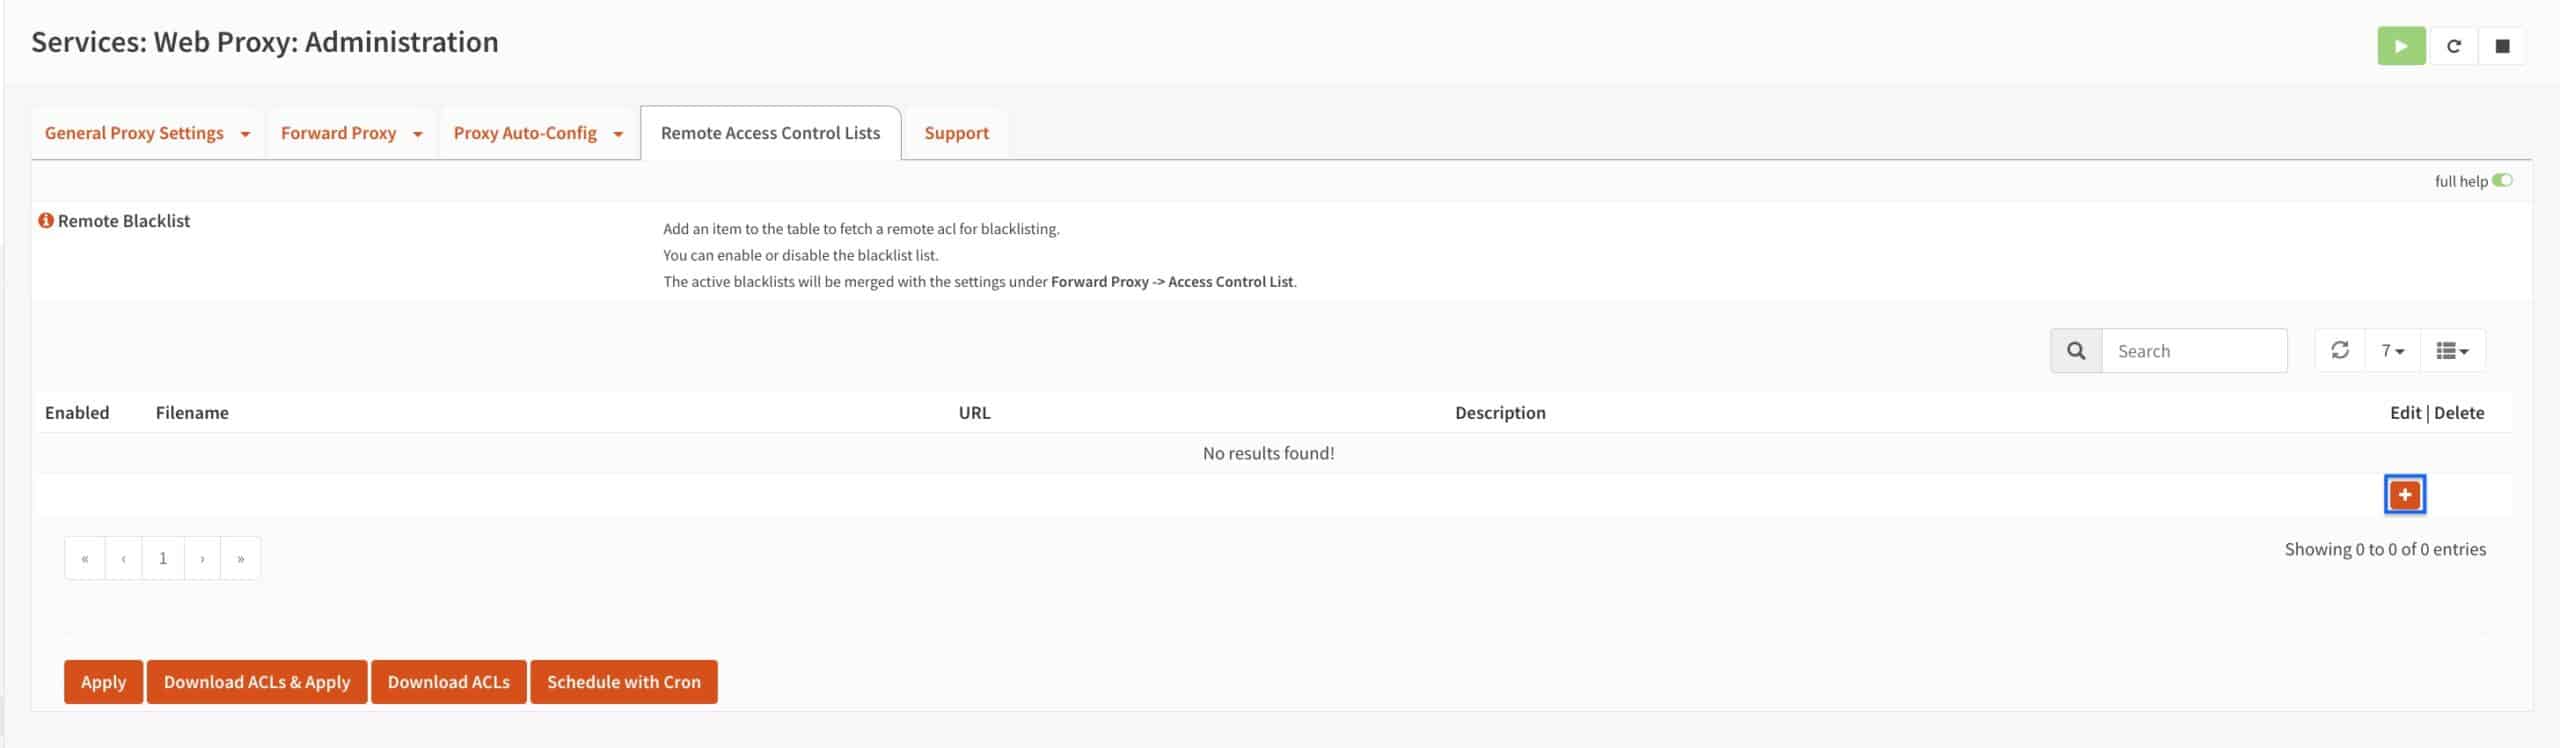
- Tick the enabled box.
- Provide a name for your list in the Filename field.
- Copy and paste the following URL into the URL field: ftp://ftp.ut-capitole.fr/pub/reseau/cache/squidguard_contrib/blacklists.tar.gz.
- Enter a description for your list in the Description field (optional).
- Click Save.
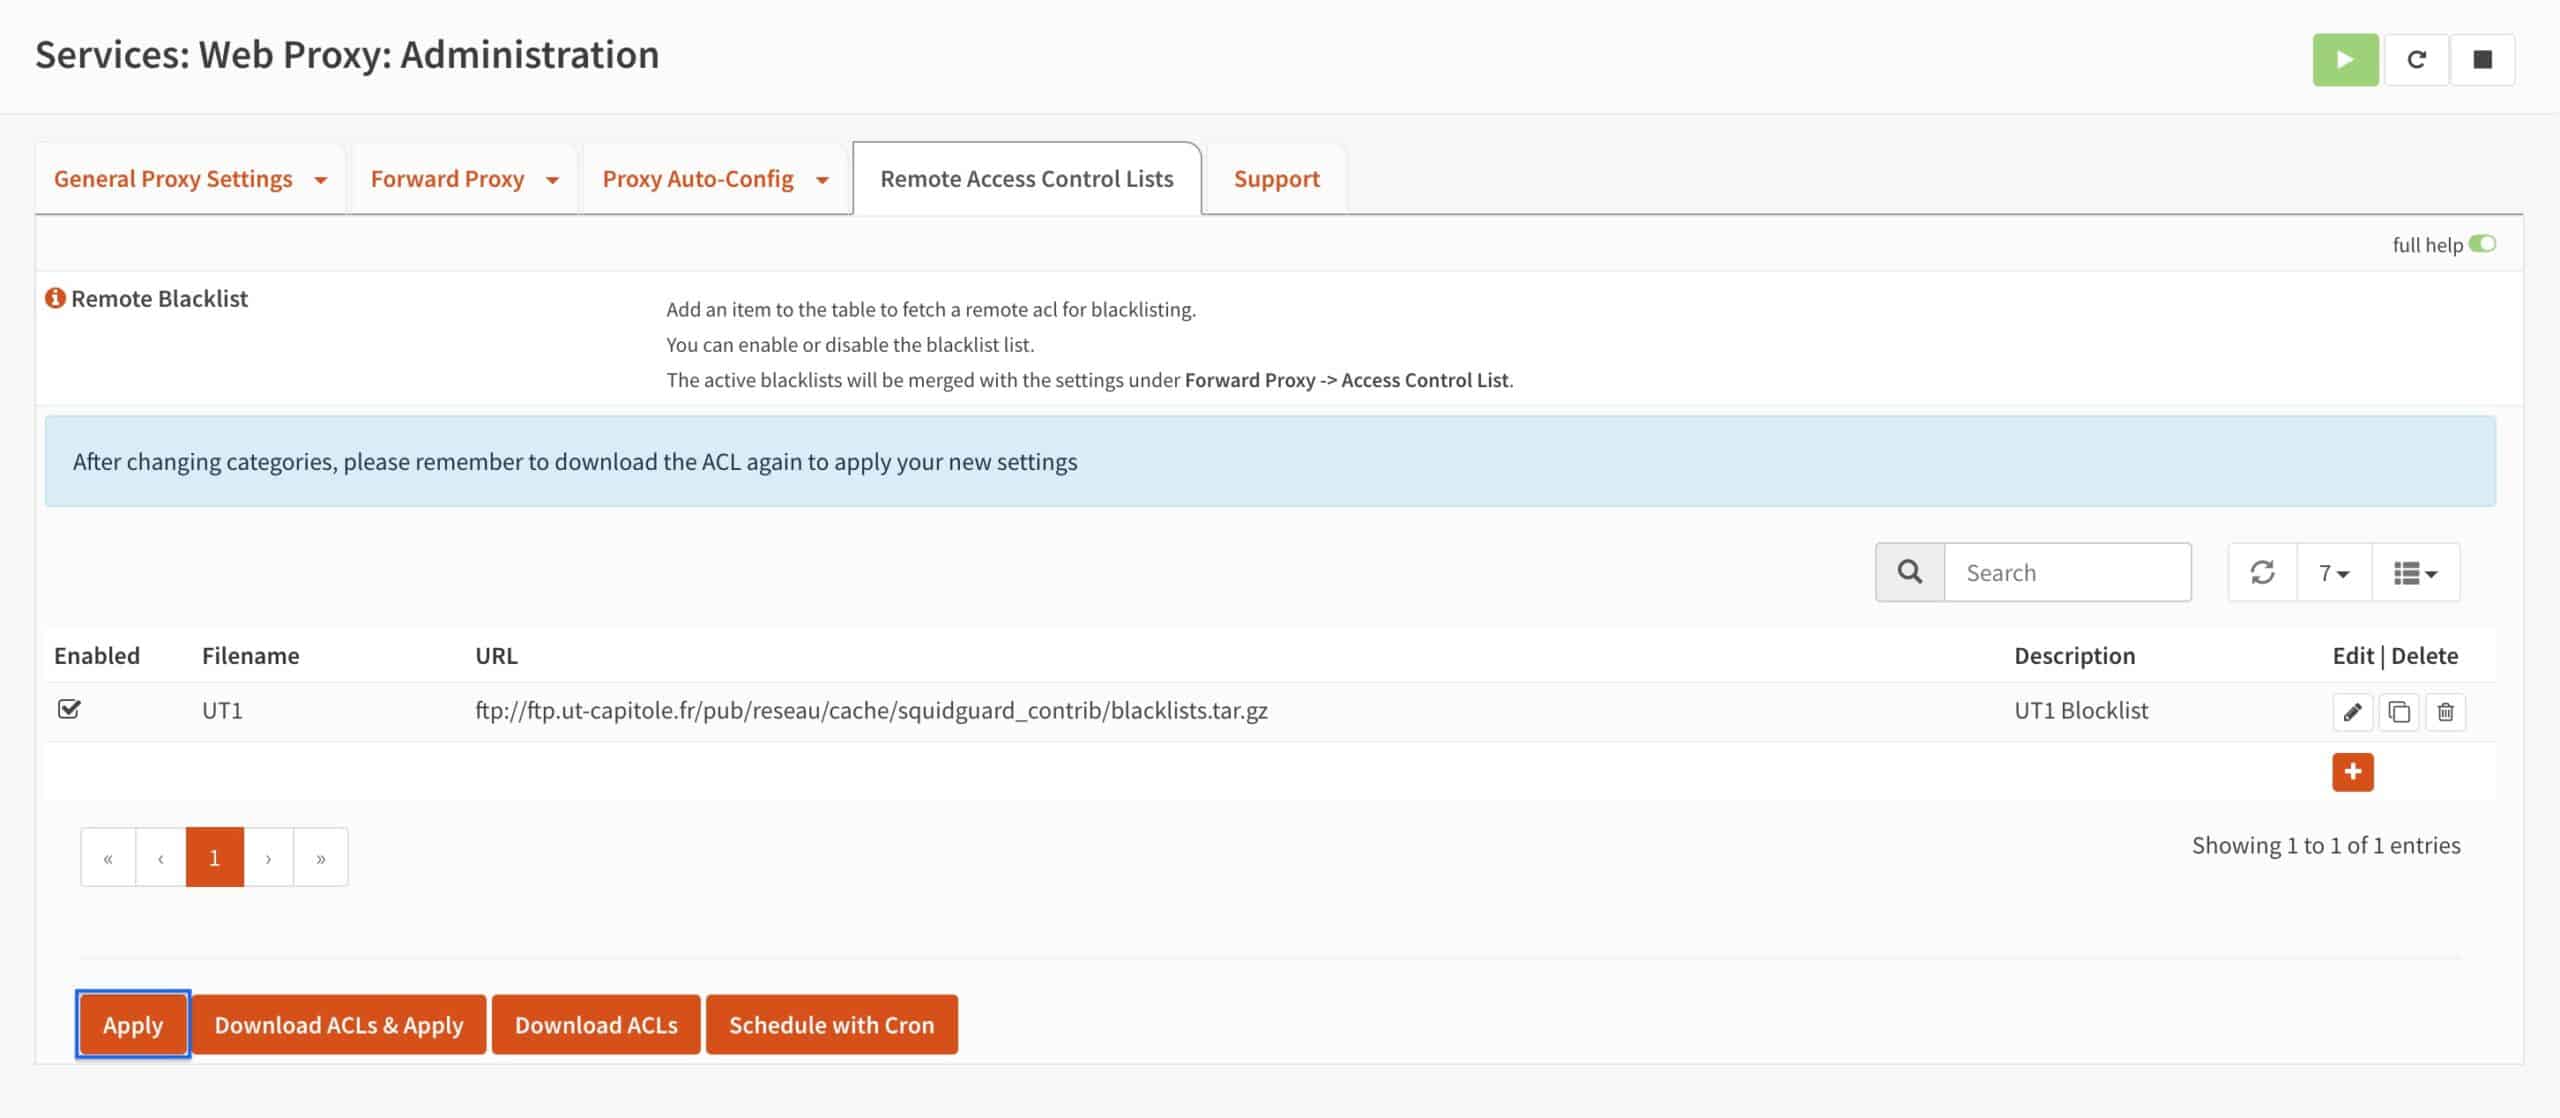
- You’re taken back to the main Remote Access Control Lists page, and we can see that our list has been created. Click Download ACLs to download our list.
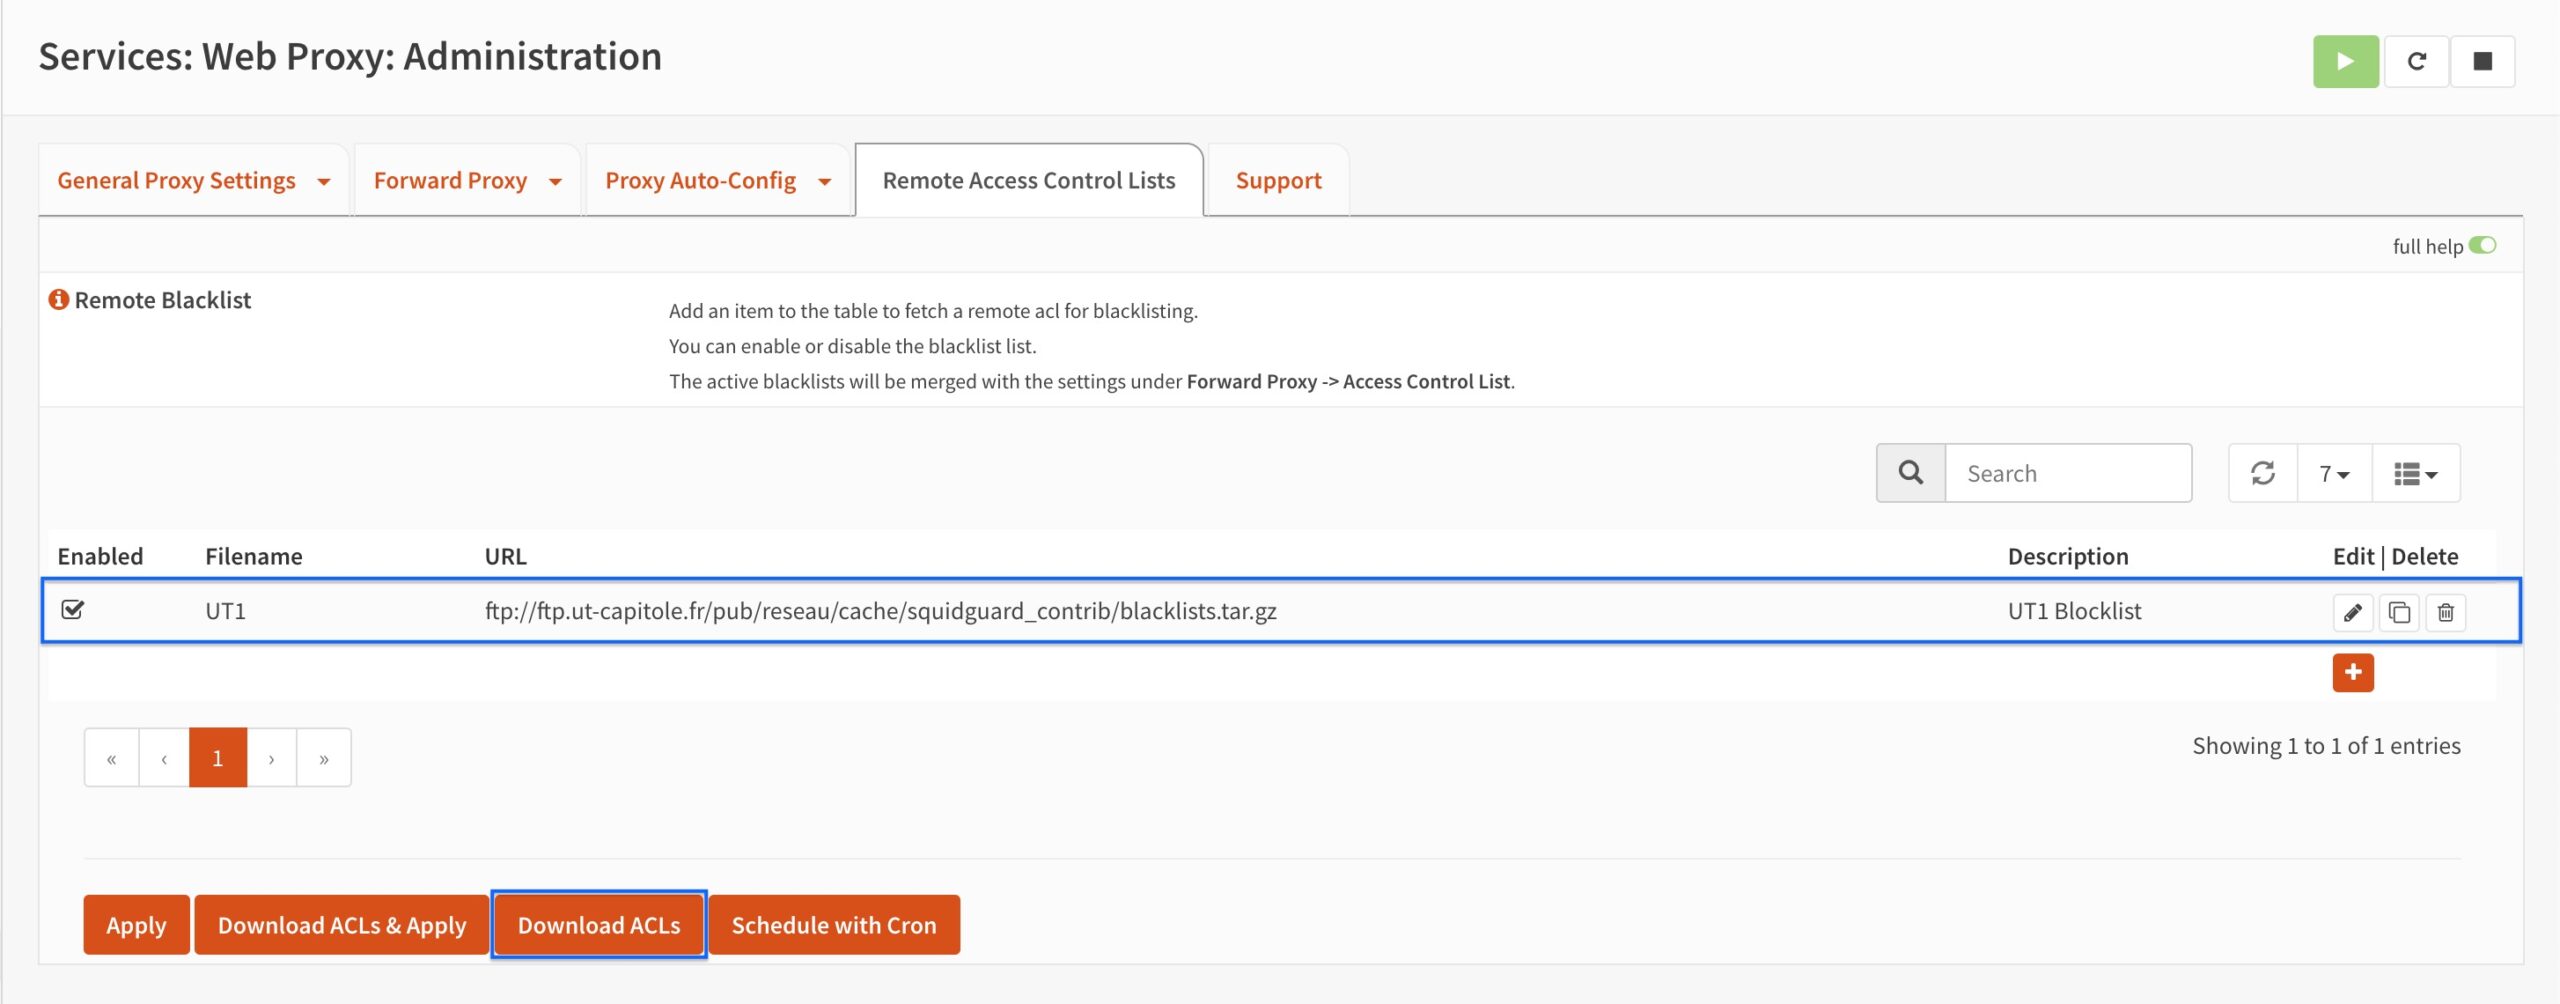
- Once the list has been downloaded (the spinning dotted circle disappears), click on the pencil icon to edit the ACL.
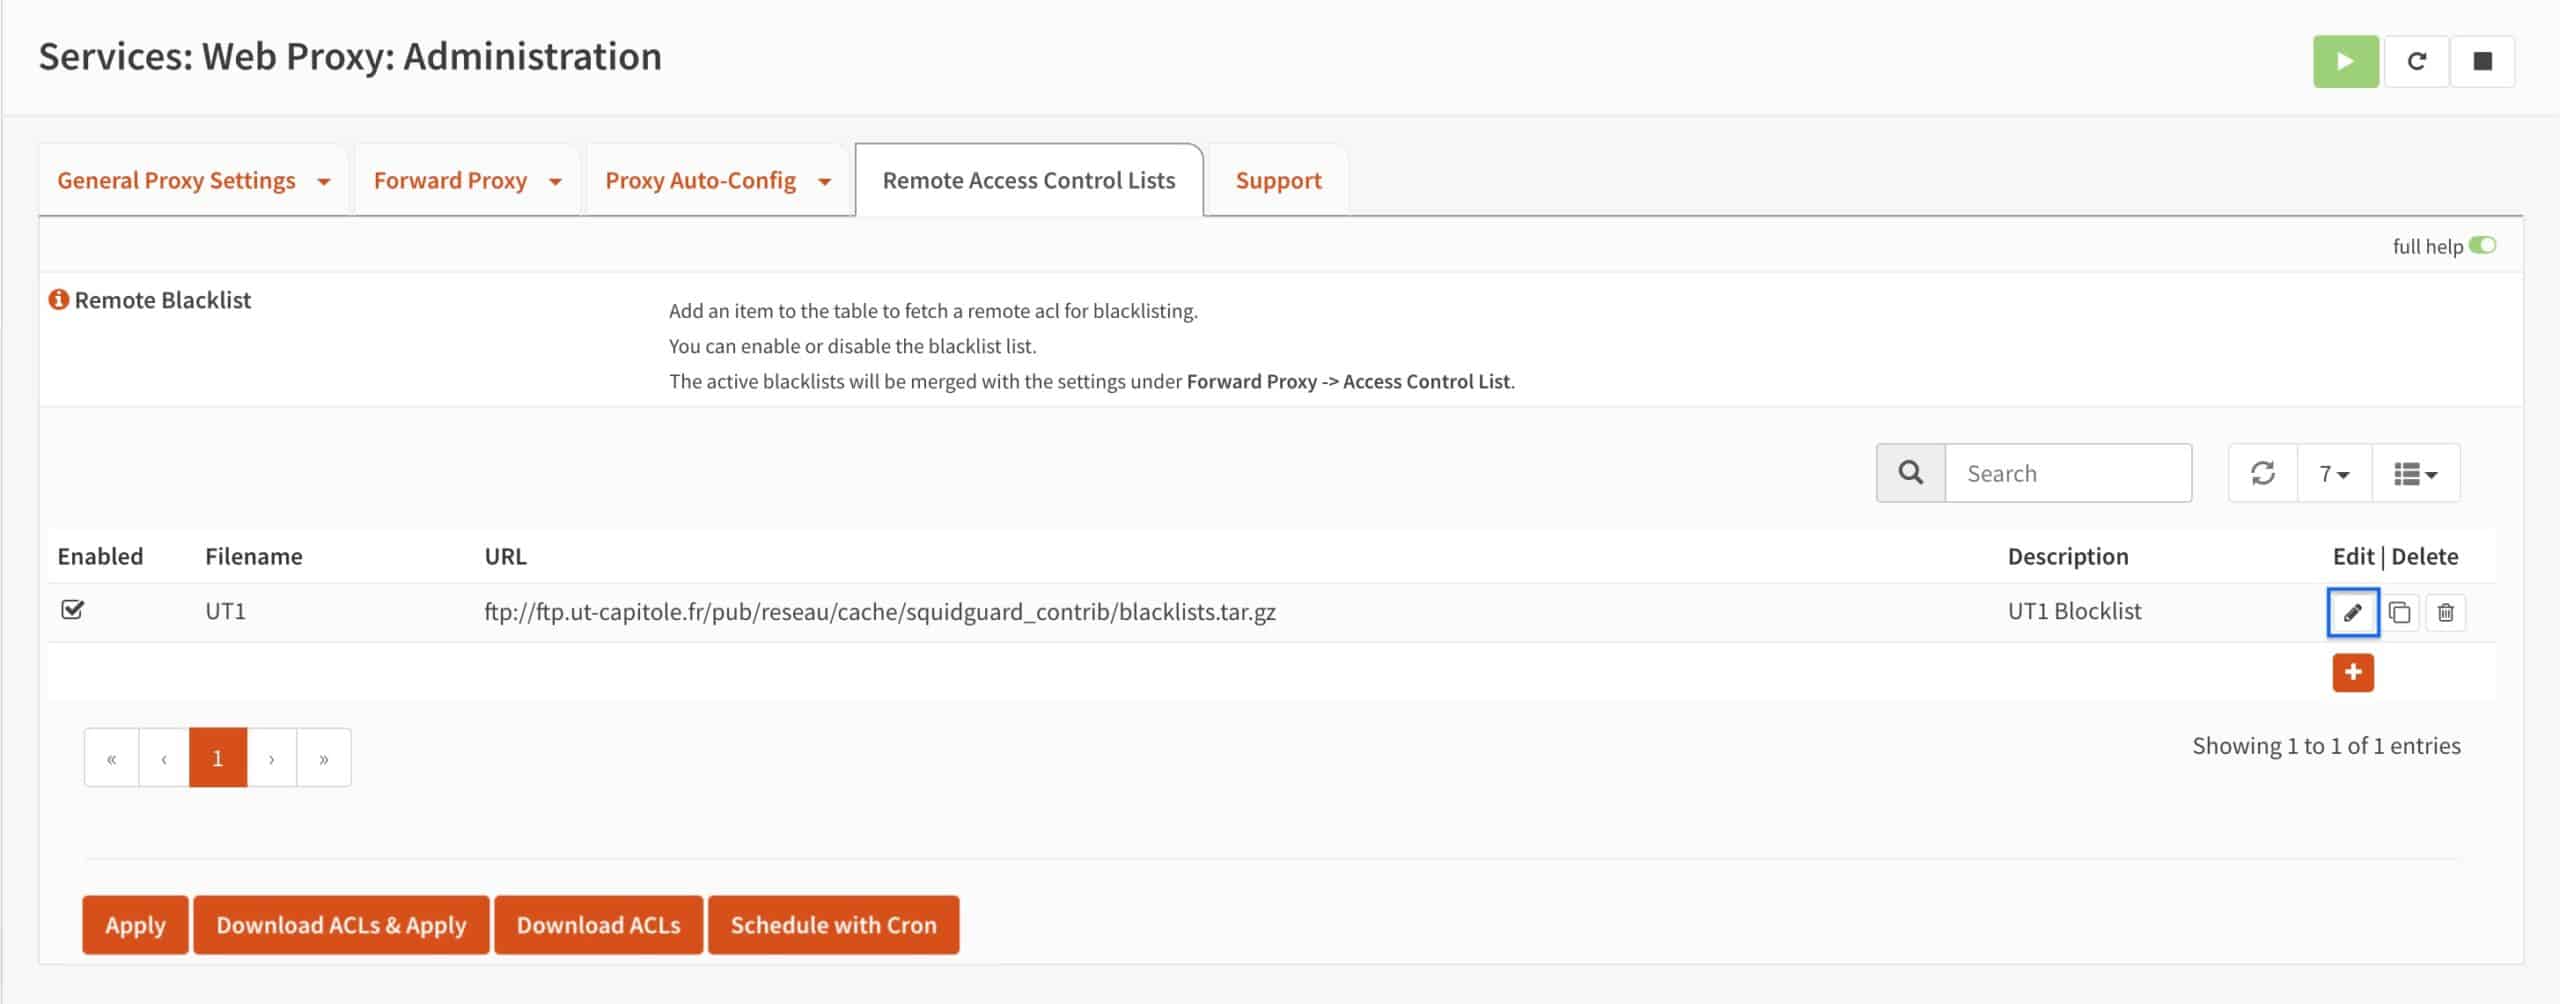
- Click on the categories drop-down menu. By default, all categories are selected. That may lead to over-blocking. Unselect all of the categories you wish to allow. Just make sure that publicite (advertisement in French) remains selected, as ad blocking is what we’re trying to achieve here. When done, click Save. You’re taken back to the main Remote Access Control Lists page.
- Click Apply.
Testing the setup
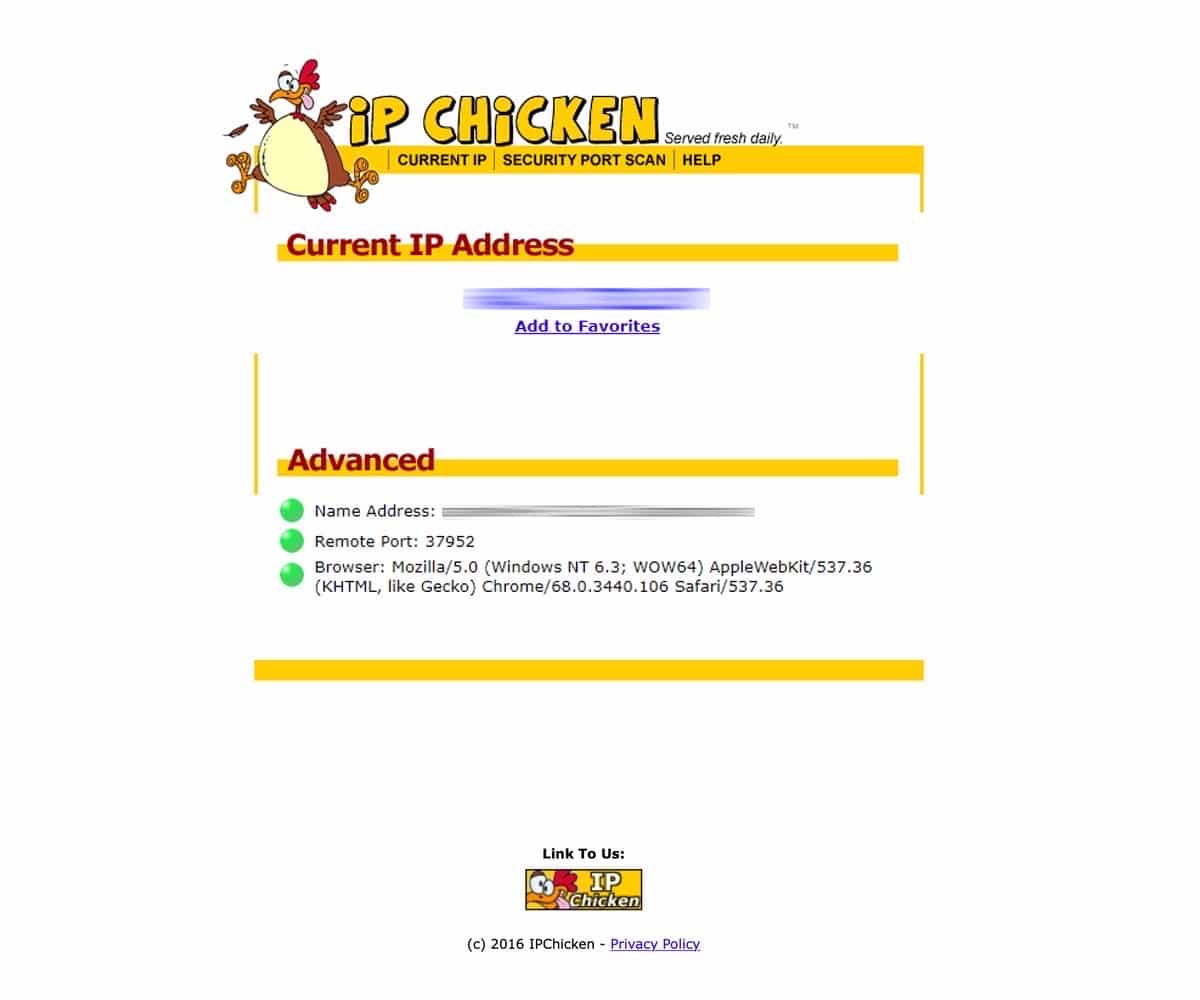
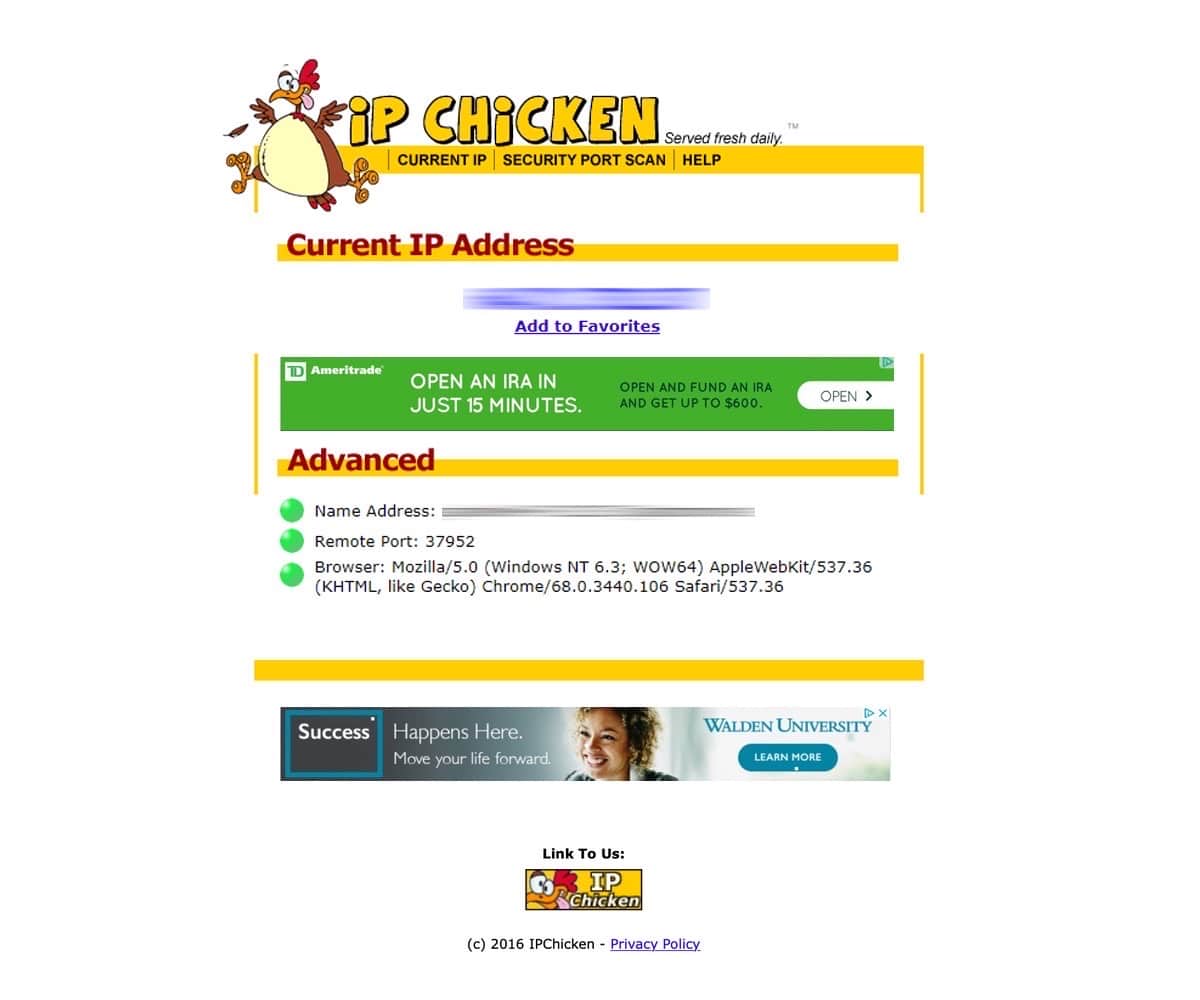
We’ve now configured Squid and integrated SquidGuard’s functionality for blacklist filtering. Because I already configured my browser to use the proxy in our previous test, if I access a webpage that displays ads, they should be filtered.
With Squid enabled:
With Squid disabled:
Great, it works. But as things are set up now, Squid will only filter my browser’s traffic. What if I wanted to filter ads out system-wide? That’s what I’m going to show you now. We’re going to configure our device(s) to send all their traffic through the proxy server. This means all your apps will benefit from Squid’s ad-blocking. I’m going to show you how to set this up on Windows, macOS, Linux, iOS, and Android.
Configuring system-wide content filtering on client devices
Reset the browser settings
First, we need to undo the manual proxy settings we applied to Firefox in our previous test.
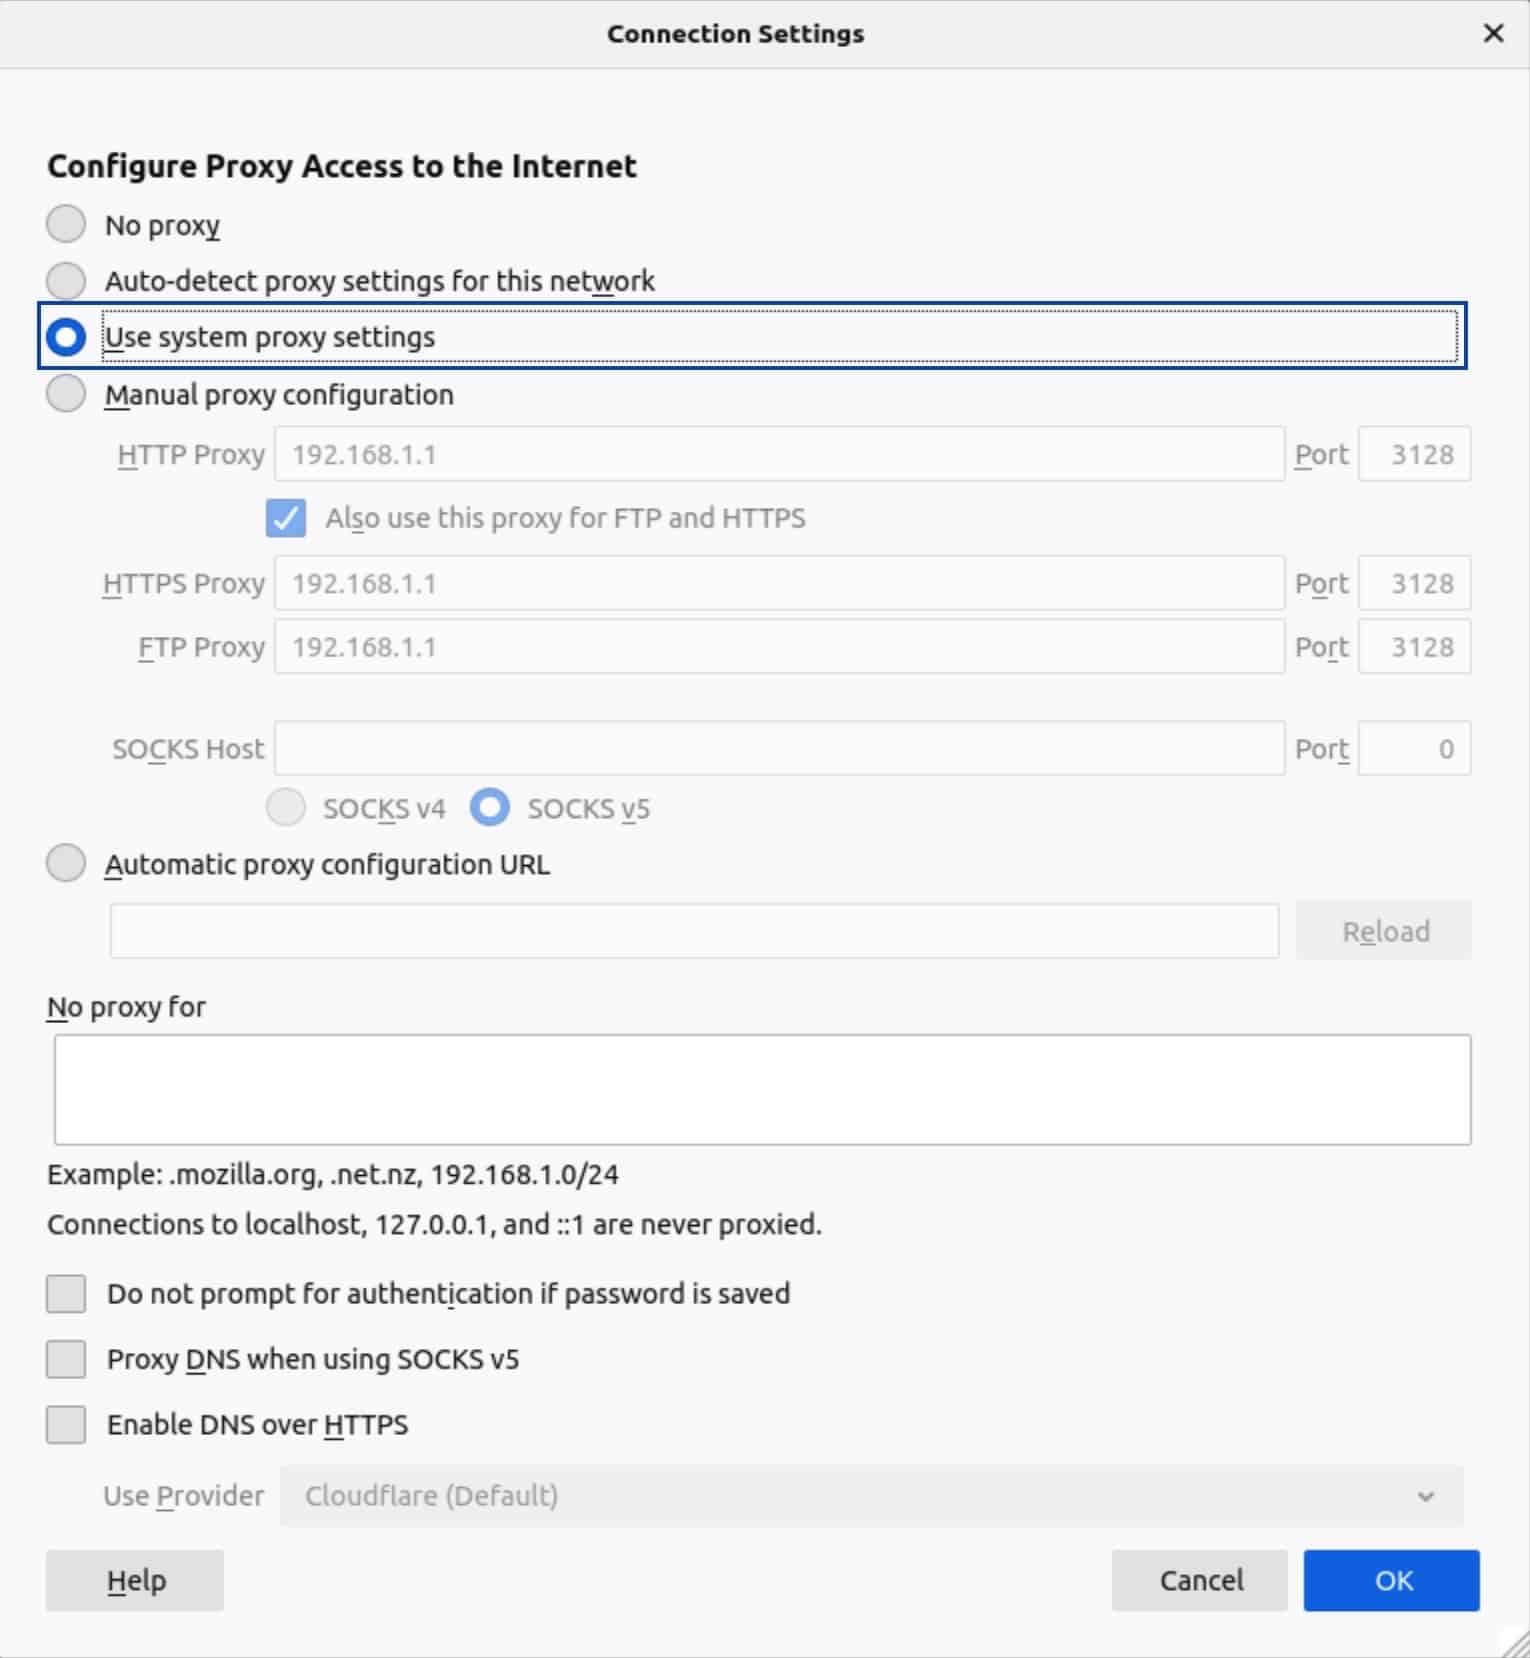
- Access the Network Settings in Firefox’s preferences, and select Use system proxy settings. This tells Firefox to use the system’s (your device) proxy settings as its own.
- Click OK at the bottom of the menu and close the Settings page.
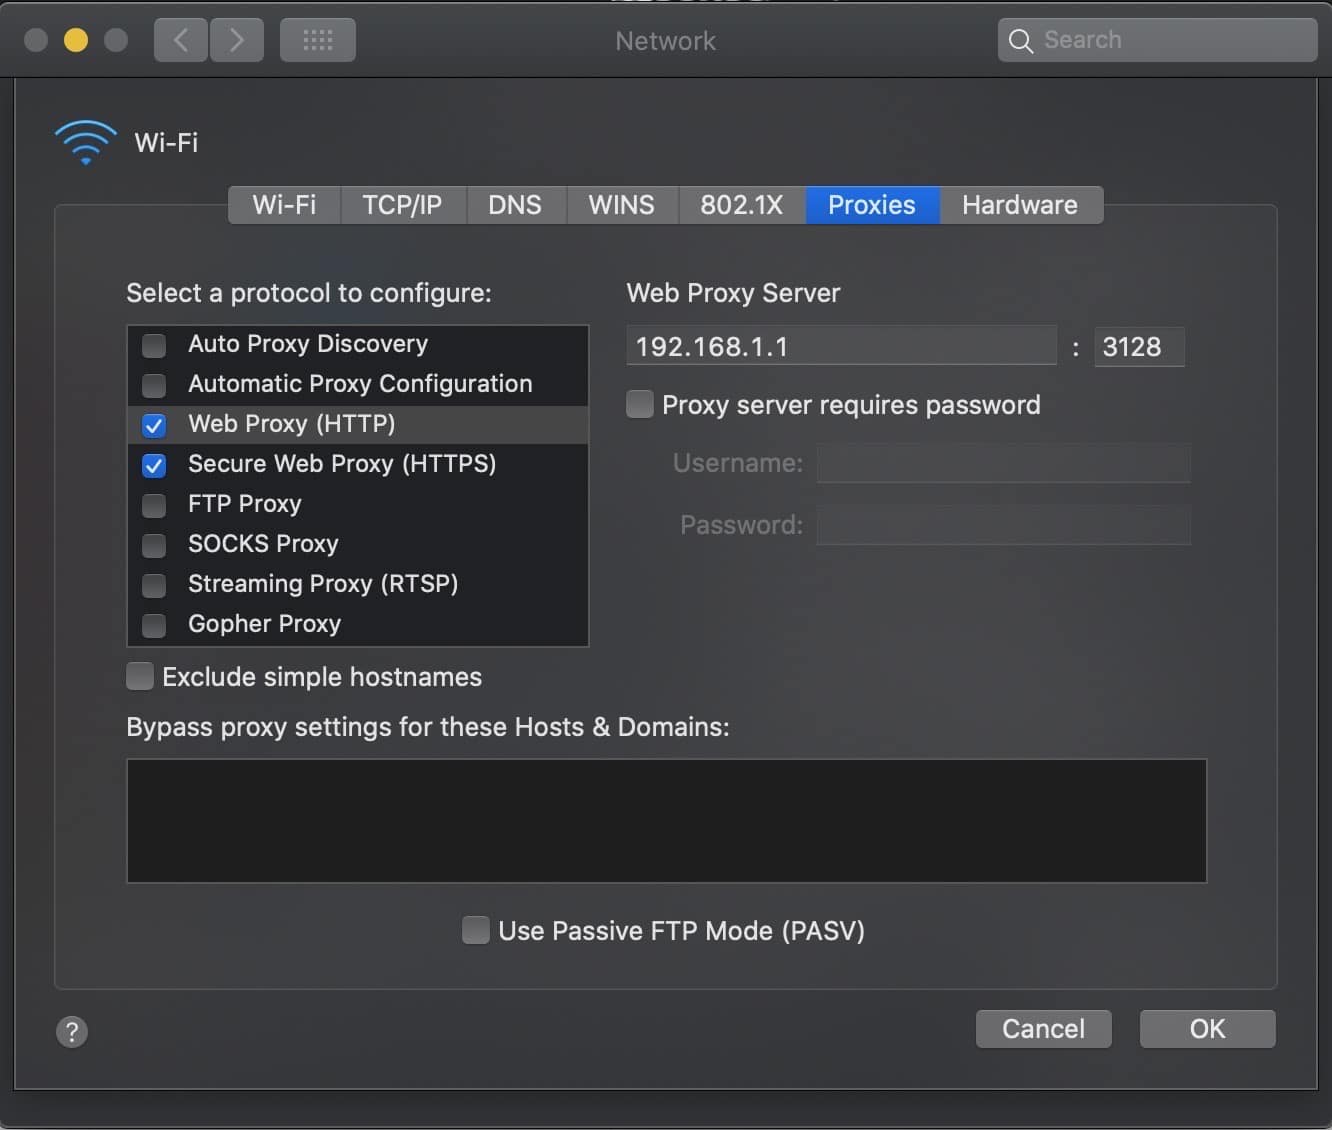
macOS
- Select Network from the System Preferences app.
- Select your current connection and click Advanced at the bottom right.
- Select the Proxies tab.
- Click the Web Proxy (HTTP) and the Secure Web Proxy (HTTPS) boxes.
- Enter the IP address of your OPNsense box and the proxy port. 192.168.1.1 and 3128 are the default values.
- Click OK and Apply.
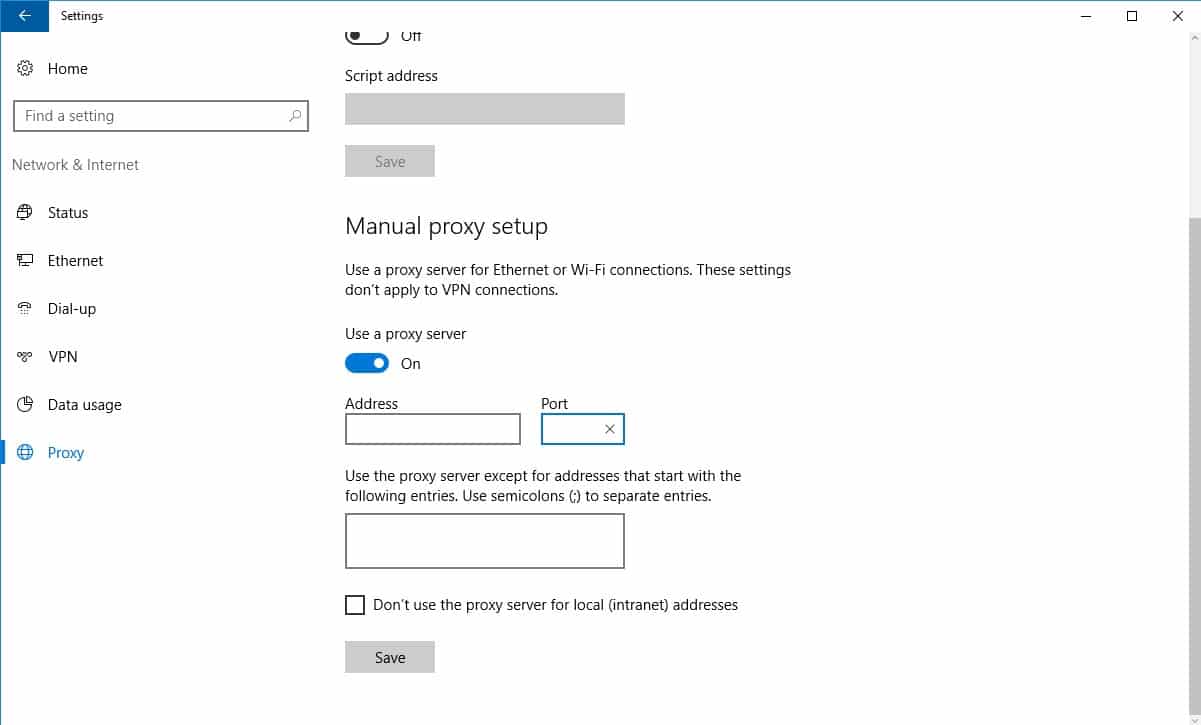
Windows
- Access the Settings app (Win+I keyboard shortcut).
- Select Network and Internet.
- Select the Proxy tab.
- Scroll down to find the Manual proxy setup section.
- Enable the Use a proxy server switch.
- Enter the IP address of your OPNsense box and the proxy port next to Server and Port. 192.168.1.1 and 3128 are the default values.
- Click Save.
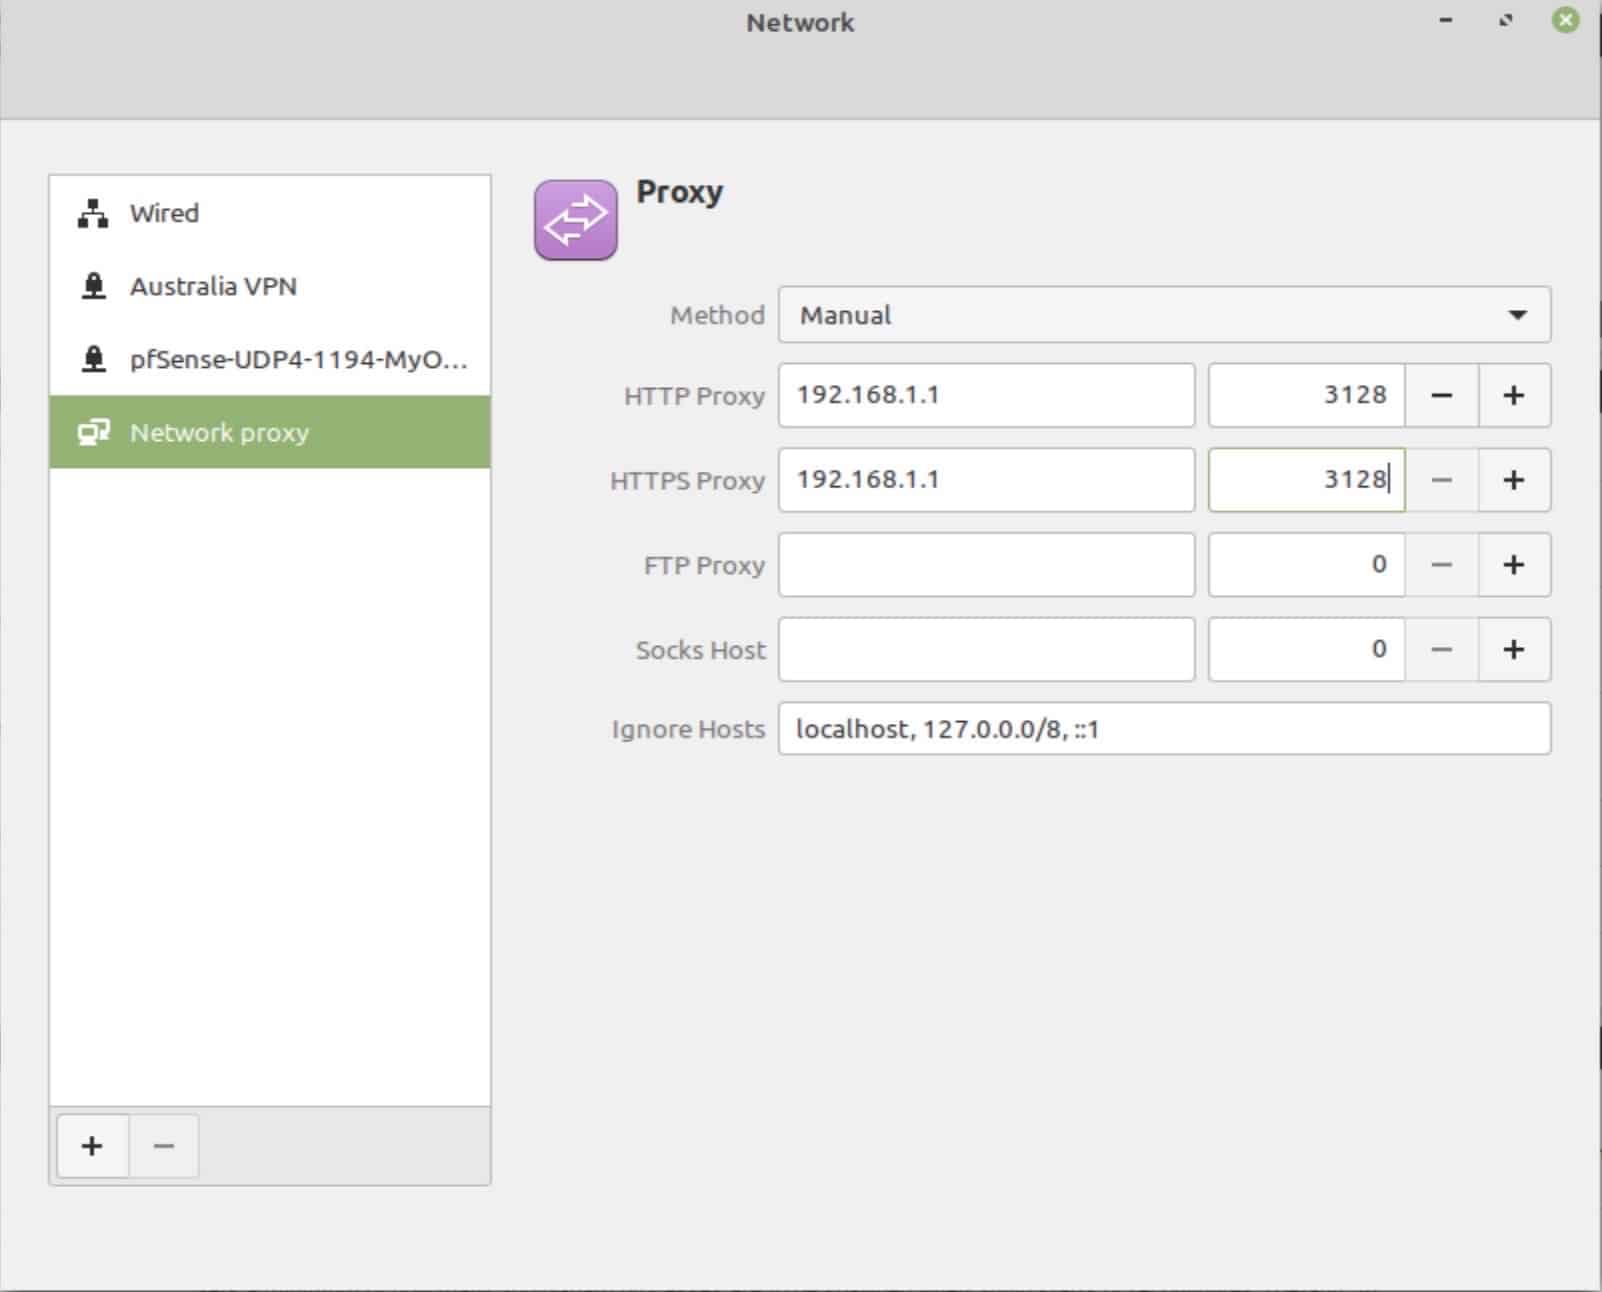
Linux
- Access the Network Settings window and select Network proxy.
- From the Method drop-down menu, select Manual.
- Enter the IP address of your OPNsense box and the proxy port next to HTTP Proxy and HTTPS Proxy. 192.168.1.1 and 3128 are the default values.
- Exit the Network Settings window.
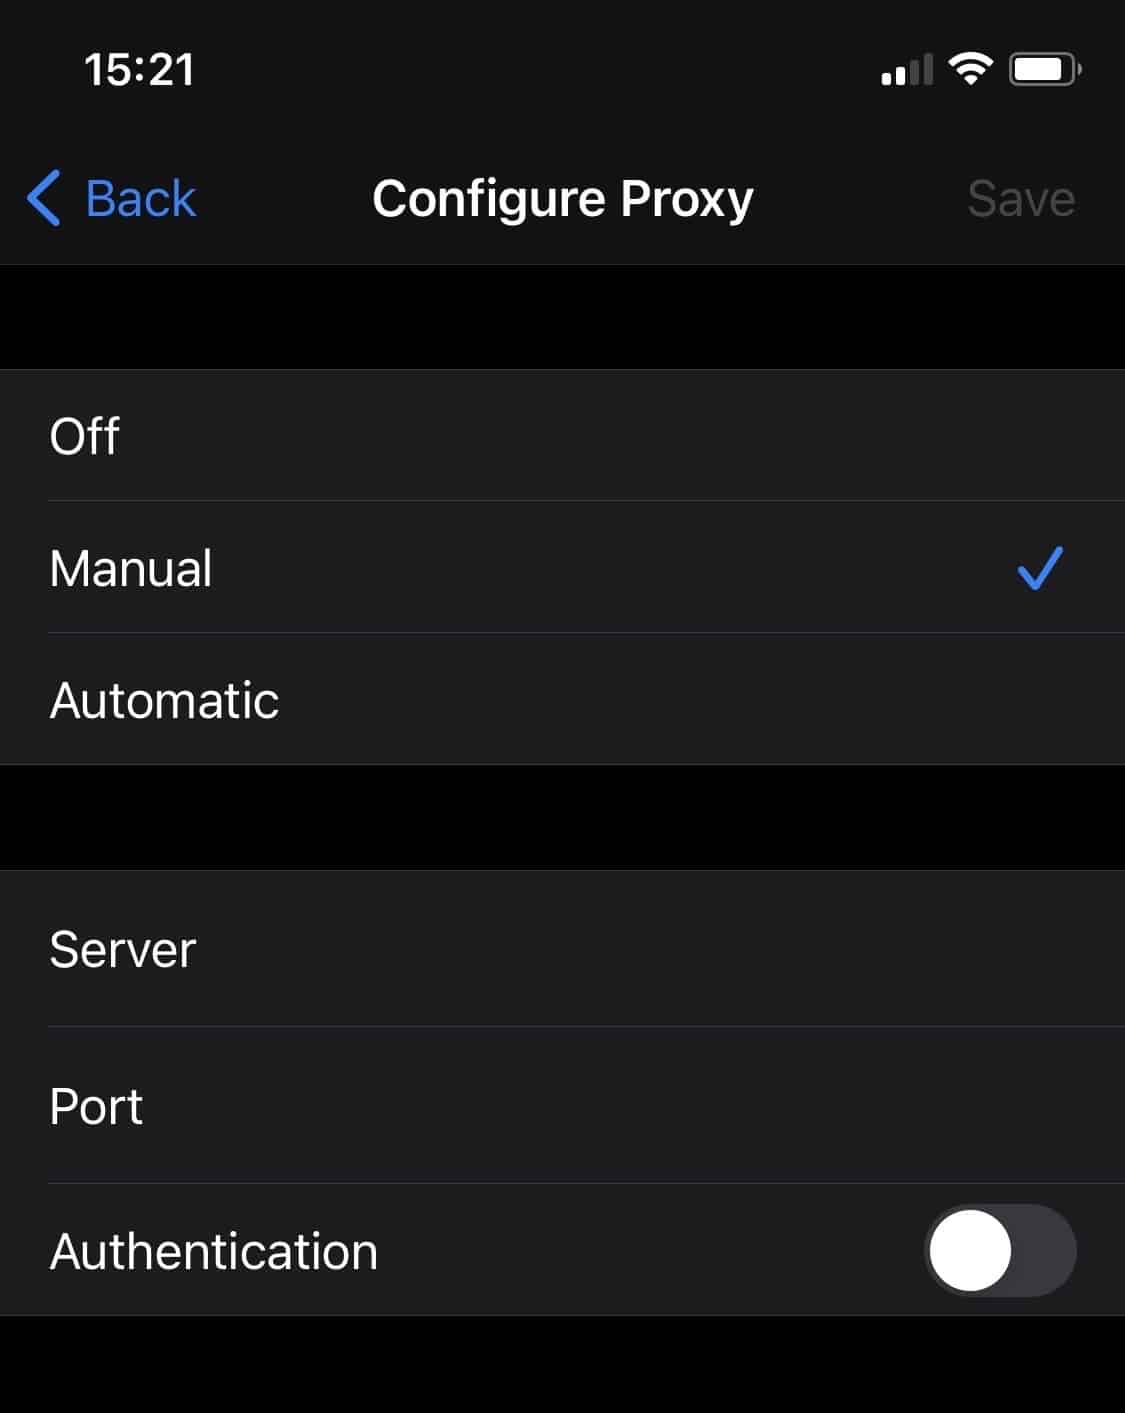
iOS
- Access the Settings app, select WiFi, and tap the “i” next to your WiFi connection.
- Scroll down the page and select Configure Proxy.
- Choose Manual.
- Enter the IP address of your OPNsense box and the proxy port next to Server and Port. 192.168.1.1 and 3128 are the default values.
- Exit the Settings app.
Android
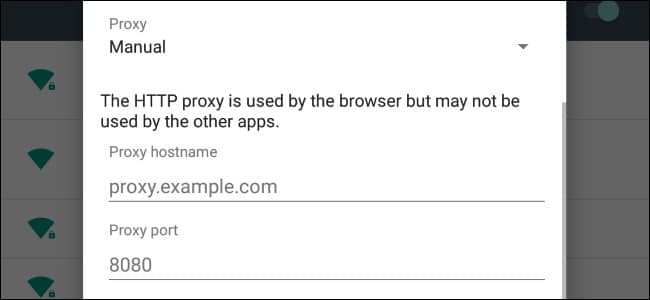
- Launch the Settings app and select WiFi.
- Long-press the current WiFi network.
- Choose Modify network.
- Expand the Advanced options.
- From the Proxy drop-down menu, select Manual.
- Enter the IP address of your OPNsense box and the proxy port – 192.168.1.1 and 3128 are the default values – under Proxy hostname and Proxy port.
- Click Save.
You may have noticed that these settings only apply to Wi-Fi. In order to use the proxy with mobile data on iOS or Android, you would need to install a mobile device management (MDM) profile, which is beyond the scope of this tutorial.
Troubleshooting
Sites are not being blocked
If domains on your blacklist remain accessible:
- Confirm that Squid is enabled
- Verify that the client is configured to use the proxy
- Check that the blacklist domain was entered correctly
- Ensure you clicked Apply after making changes
Remote ACL categories are not working
If URL-list filtering does not appear to be functioning:
- Verify that the ACL download completed successfully
- Check that the relevant categories remain selected
- Re-download the ACL list and reapply the configuration
HTTPS sites still show advertisements
This is often expected behavior. URL-list filtering can block domains, but it cannot inspect encrypted HTTPS traffic without SSL inspection. Some websites serve content and advertising from the same domain, making selective blocking difficult.
Users can bypass the proxy
If users can still access websites directly, implement the optional firewall rules described below to block direct HTTP and HTTPS connections that do not pass through the proxy.
Disabling proxy bypass (optional)
You can also remove the ability for clients on your LAN interface (and any other LAN-type interface you want to proxy) to bypass the proxy server by setting up two firewall rules:
- A rule blocking port 80 (HTTP) outside the proxy;
- A rule blocking port 443 (HTTPS) outside the proxy.
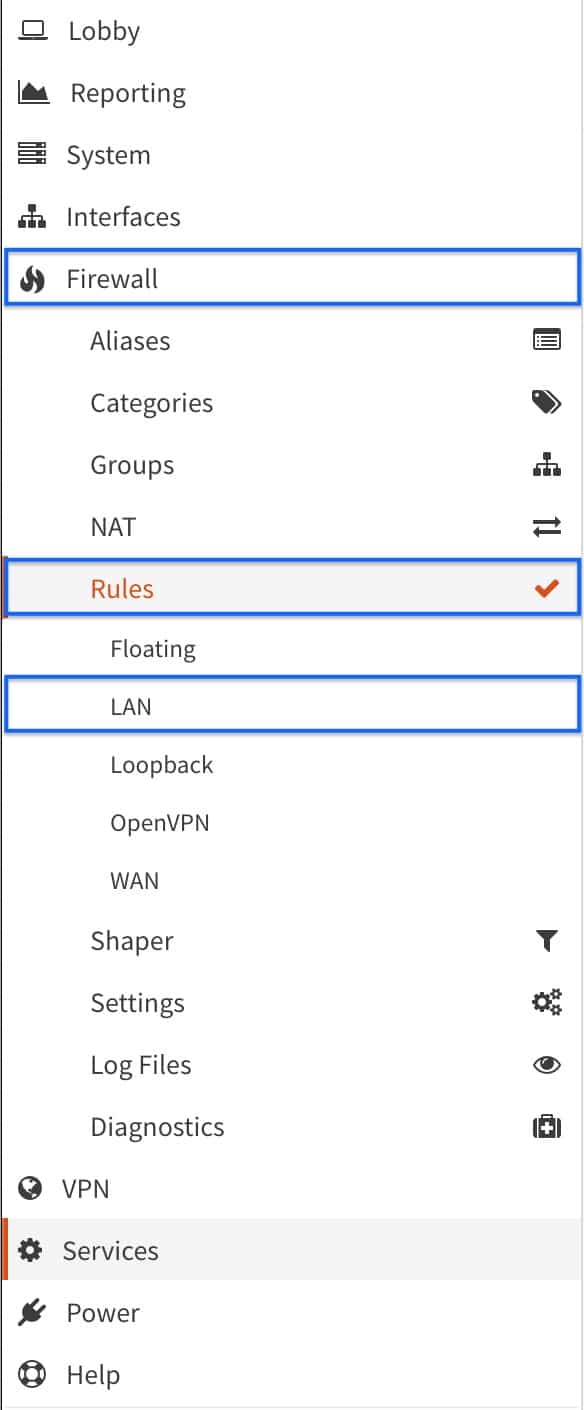
- From the side menus, select Firewall > Rules > LAN. The LAN Firewall Rules page is displayed.
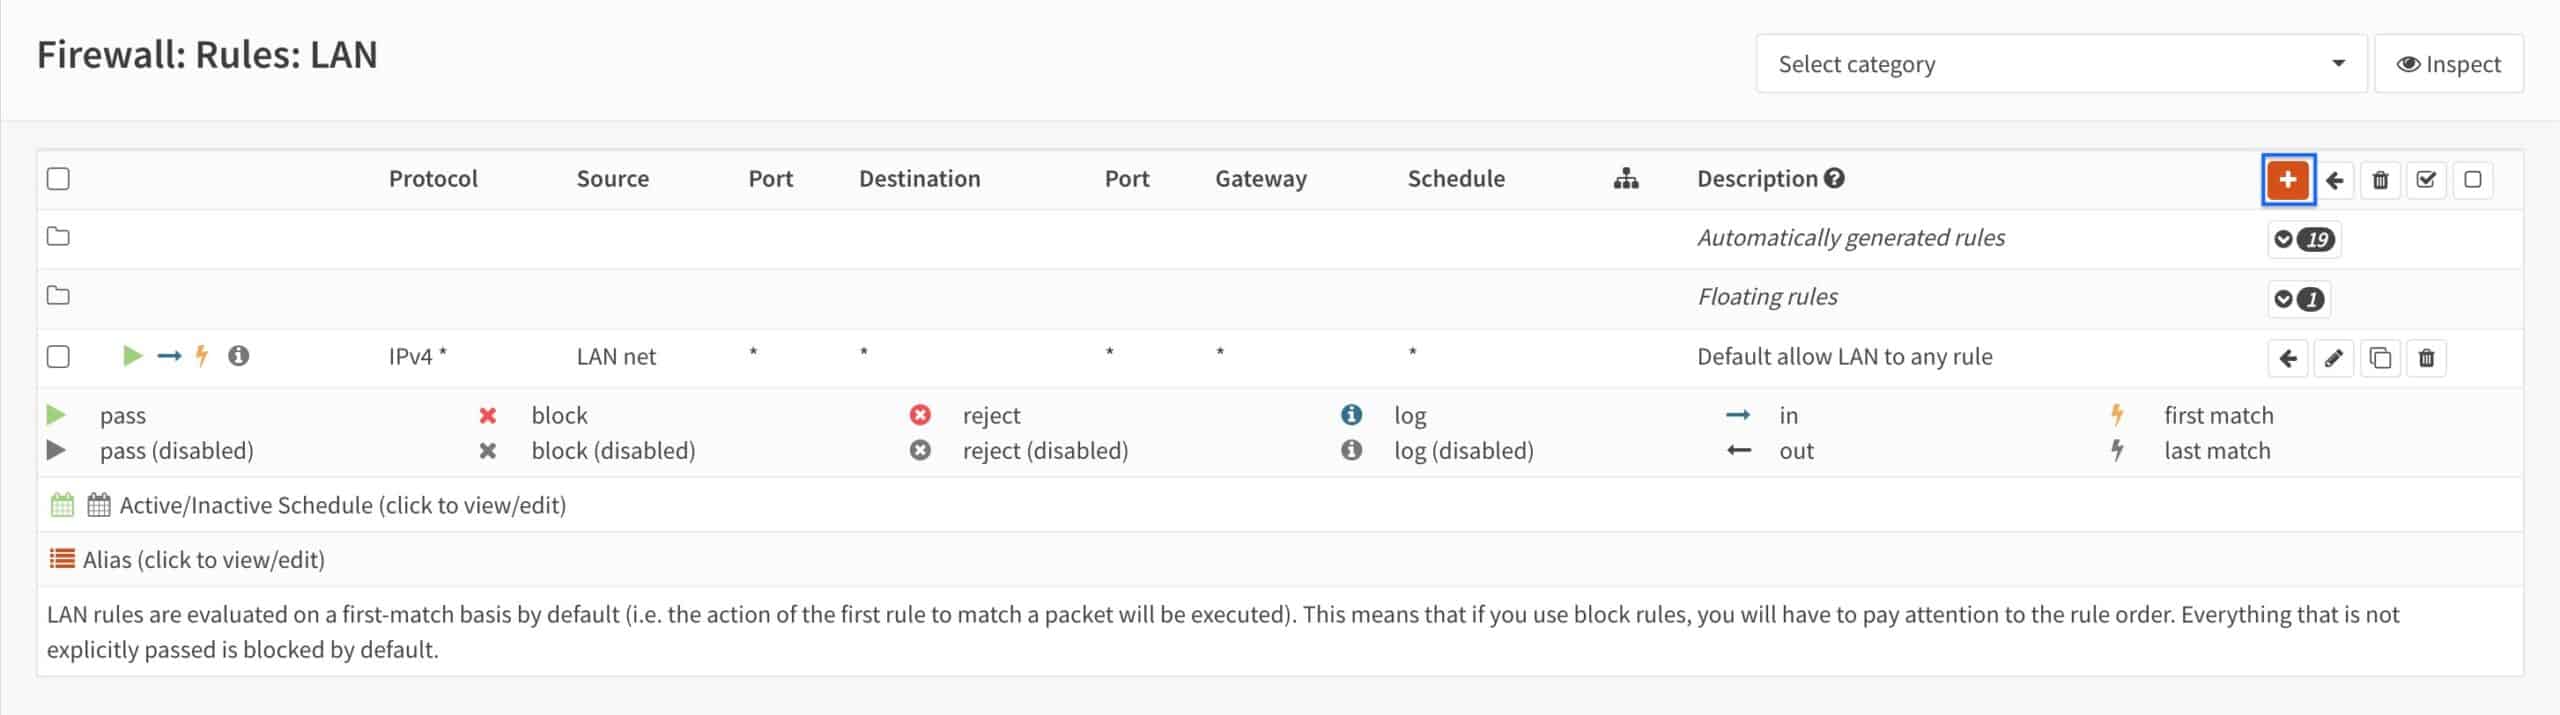
- Click the + sign to add a new rule. The Firewall Rule Configuration page is displayed.
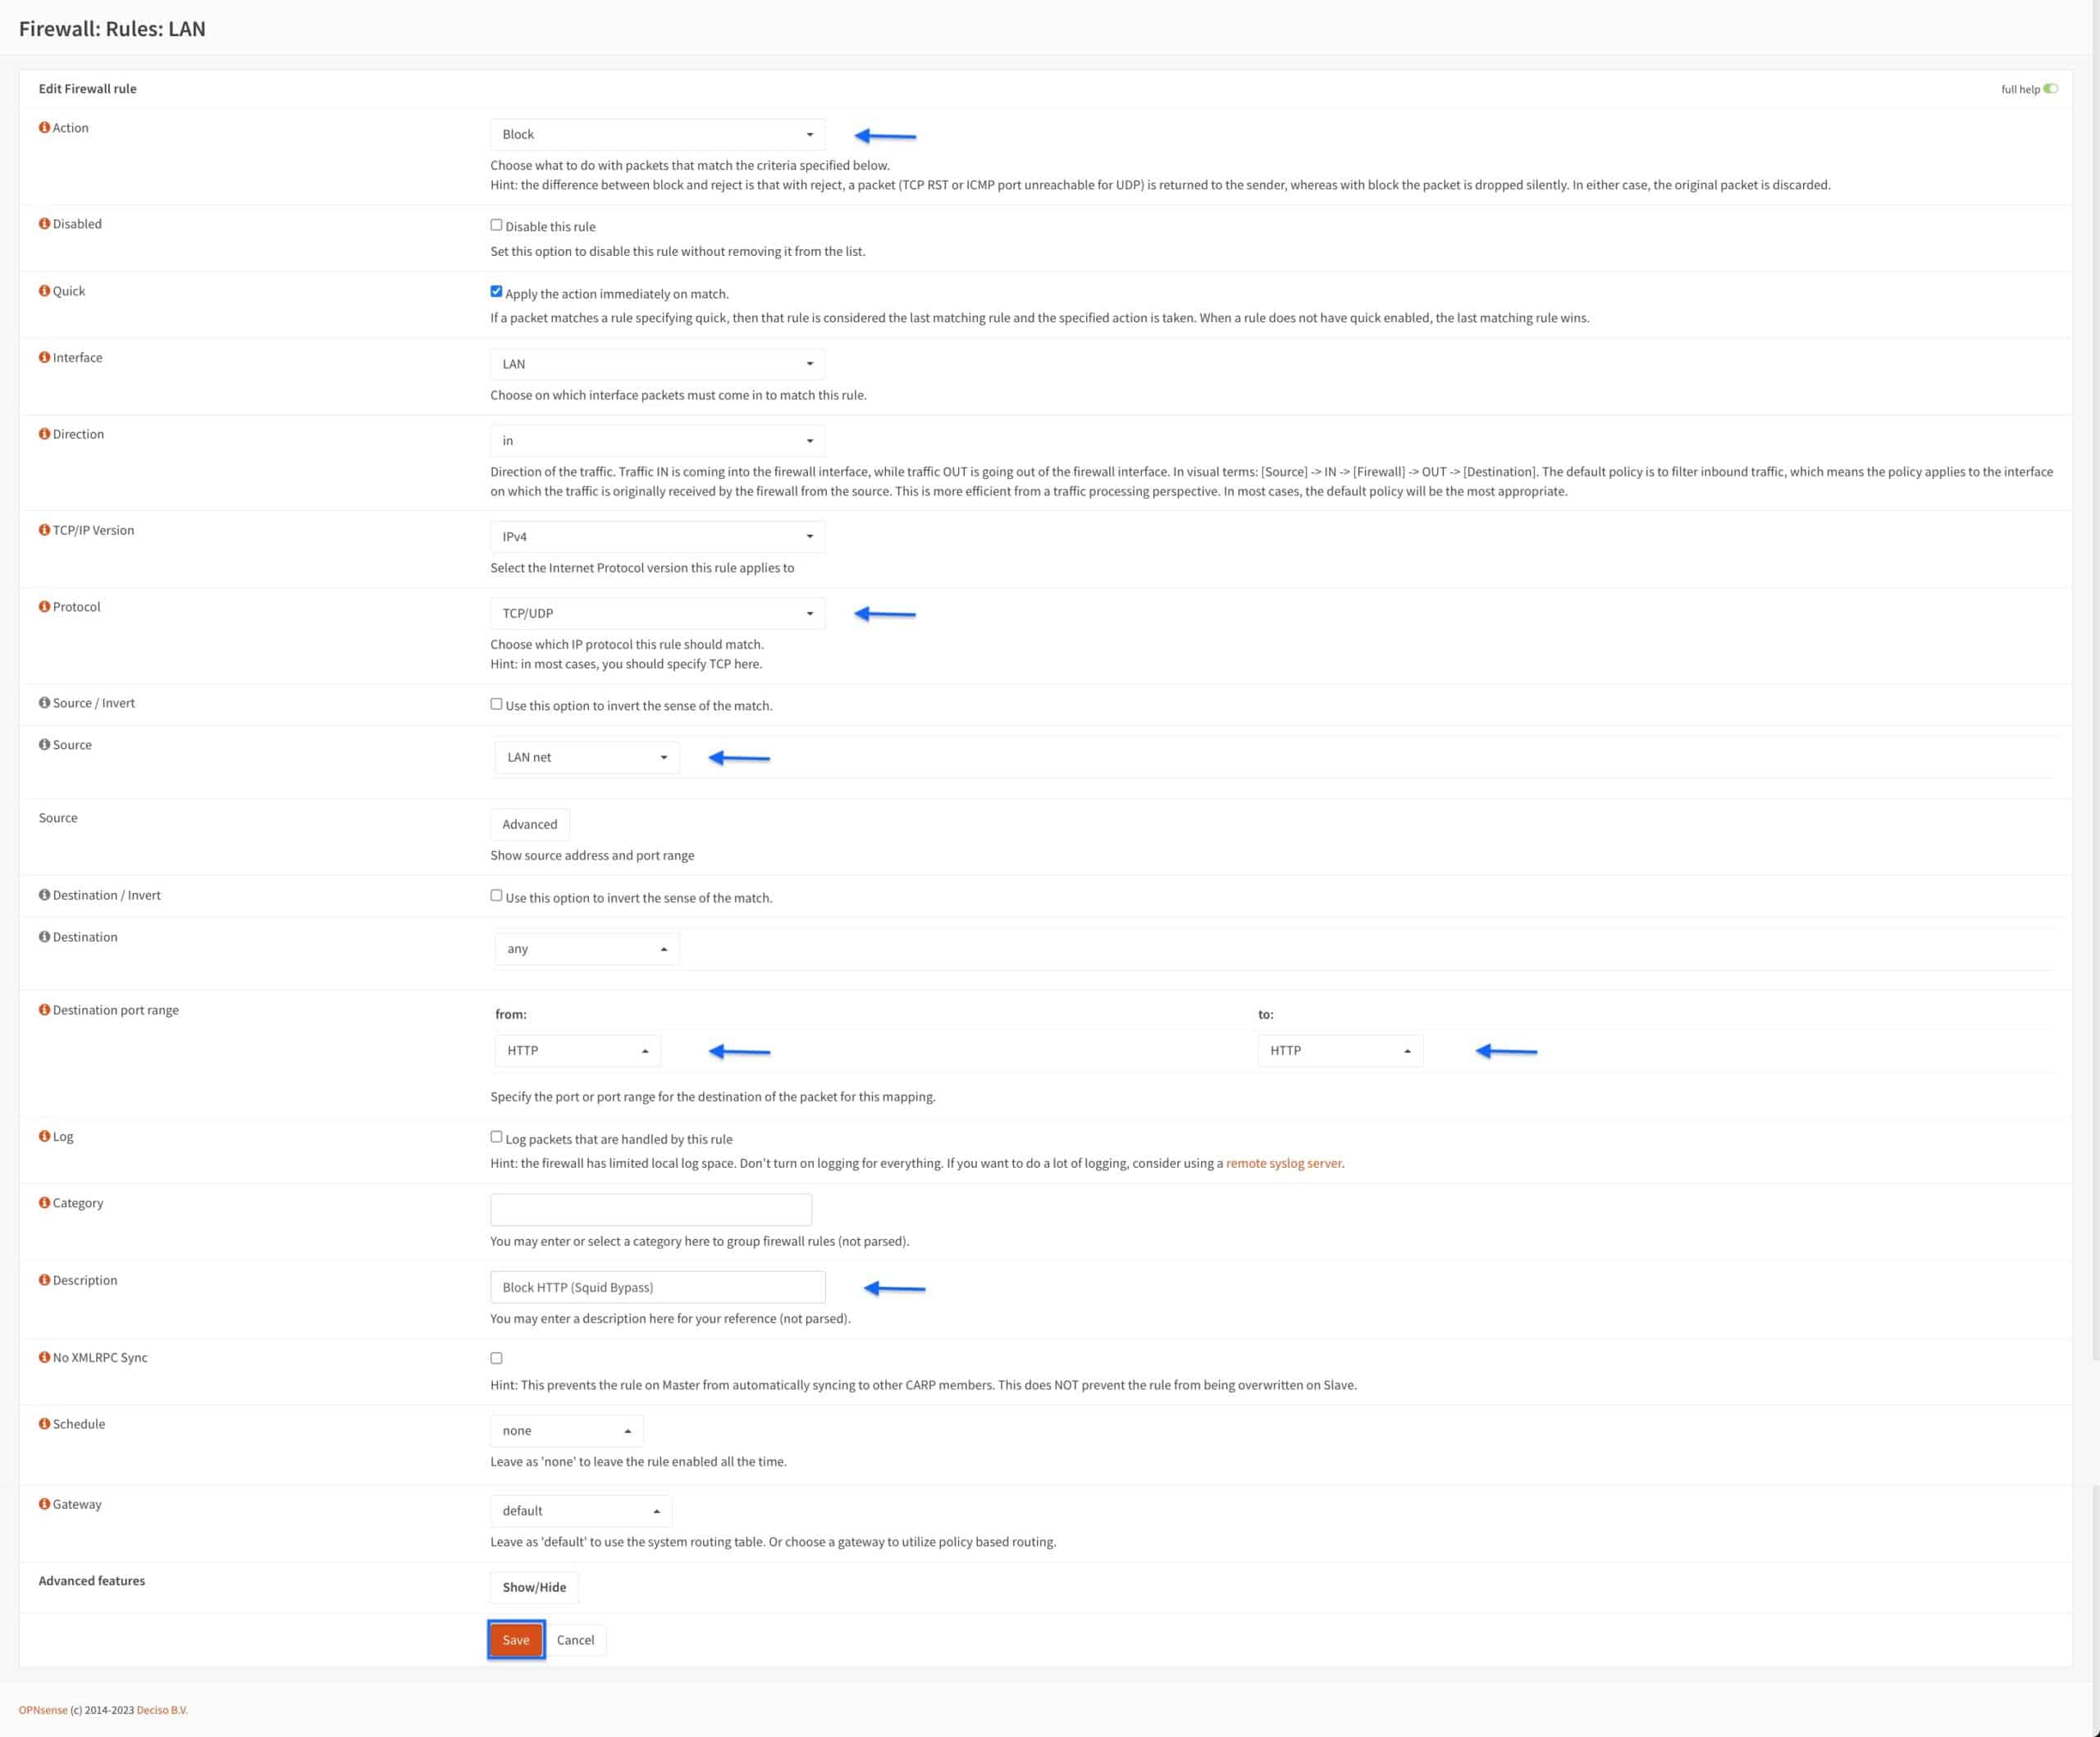
- Set the Action drop-down menu to Block.
- Set the Protocol drop-down menu to TCP/UDP.
- Set the Source drop-down menu to LAN.net.
- Set the Destination port range drop-down menus to HTTP.
- Enter a description for your rule in the Description box (optional).
- Click Save.
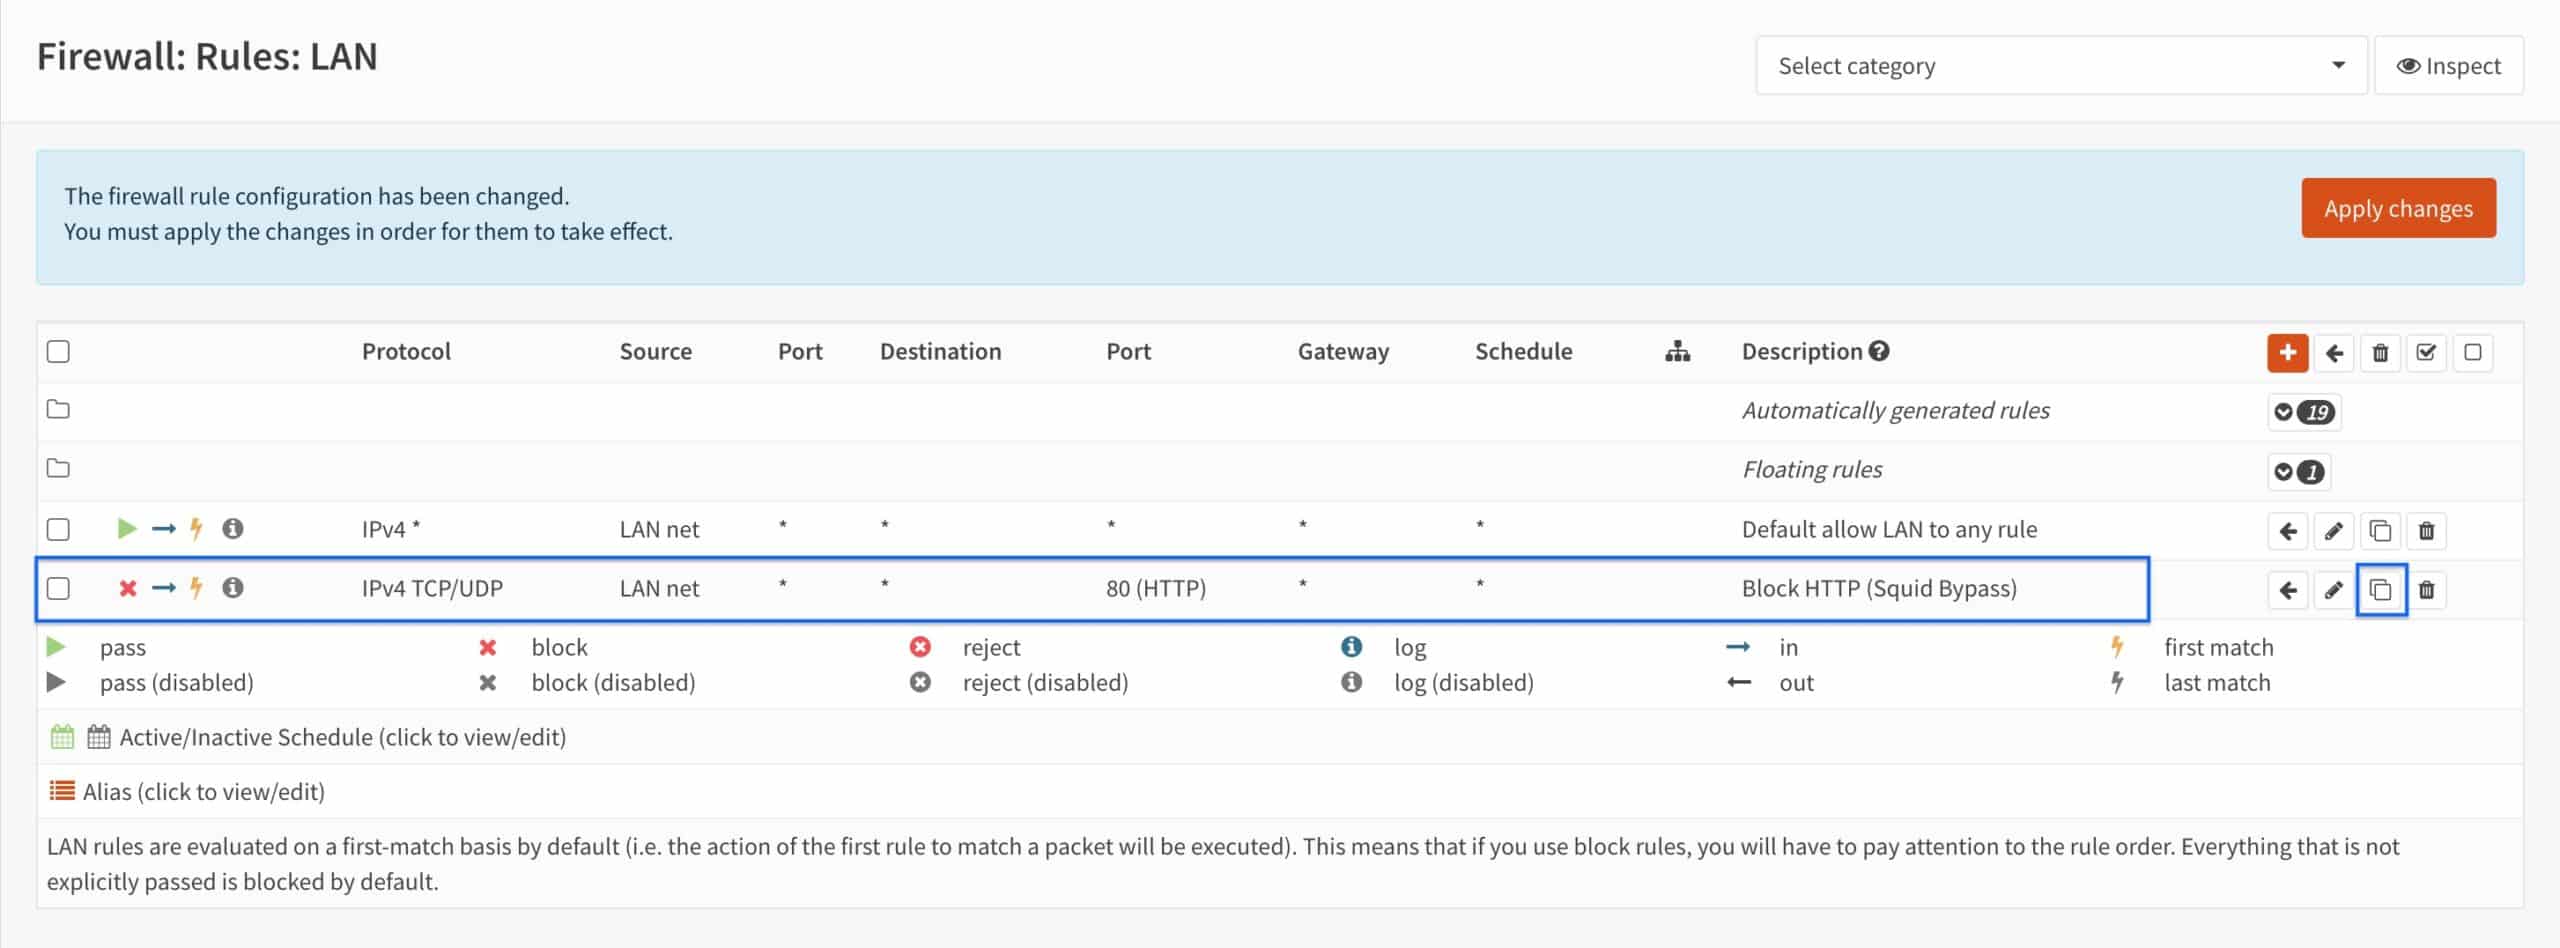
- You’re taken back to the LAN Firewall Rules page, and we can see that our rule has been created. Click the Copy icon to create a copy of that rule and edit it.
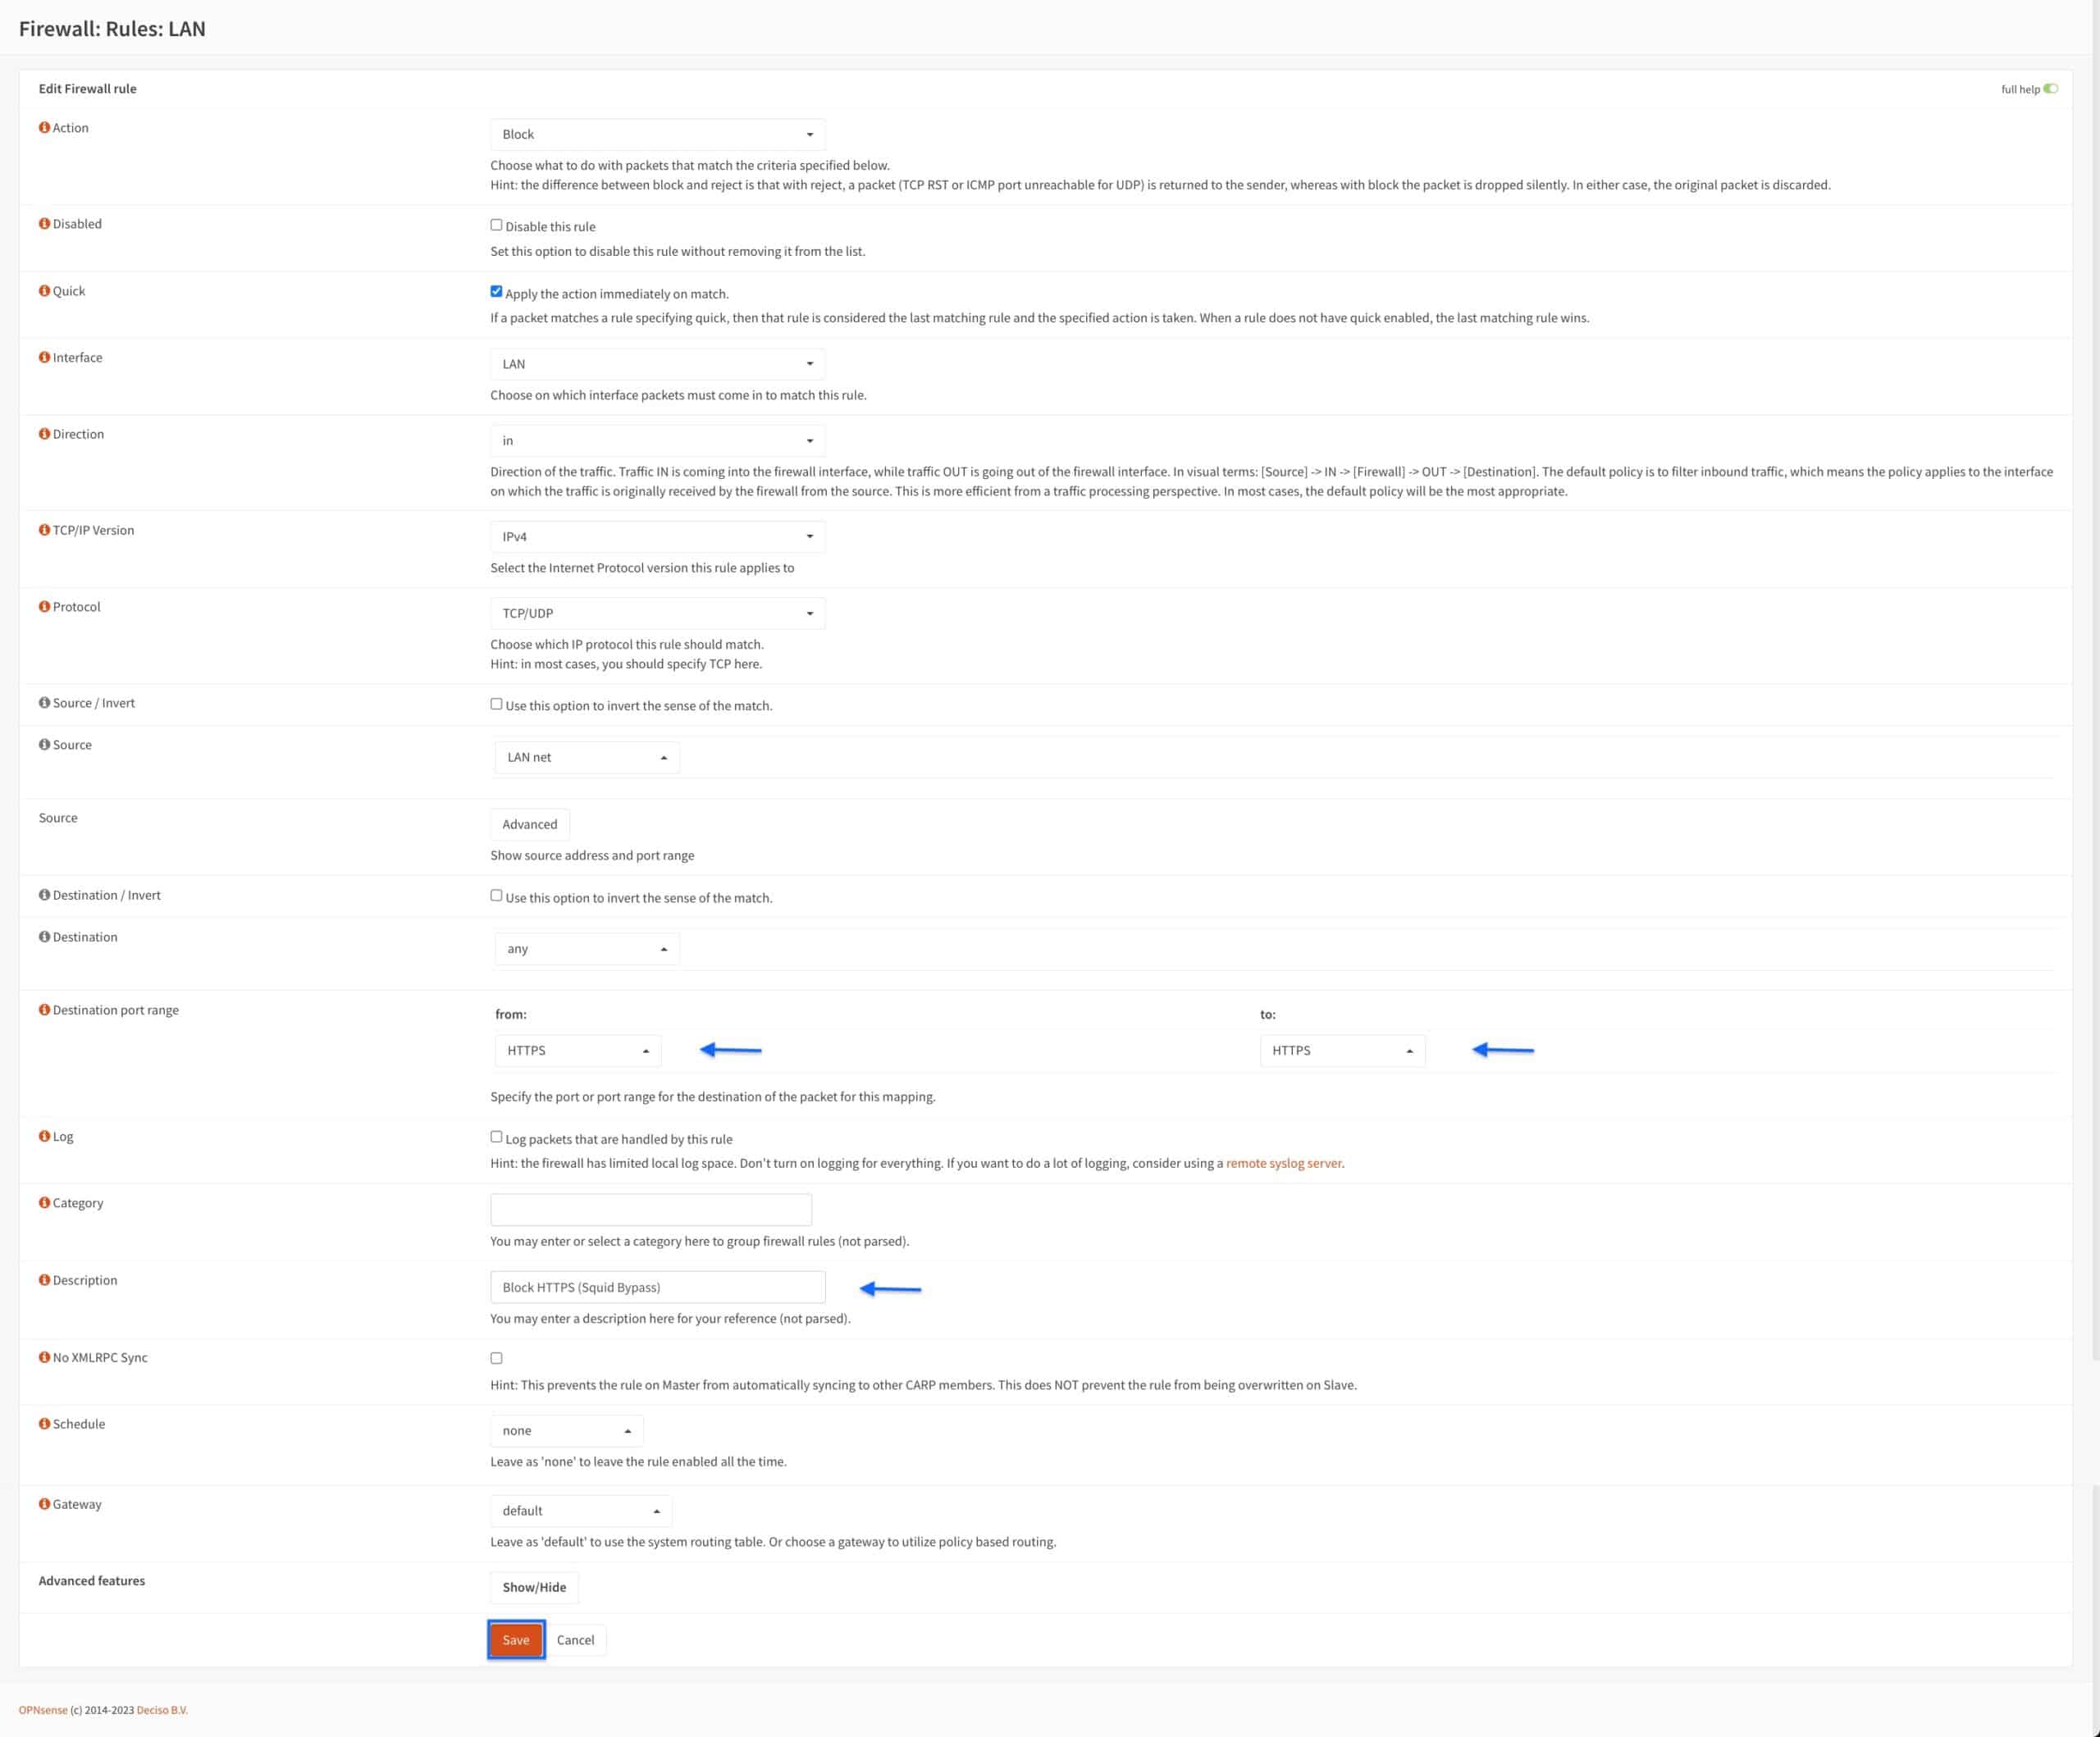
- Scroll down to the Destination port range drop-down menus and select HTTPS instead of HTTP.
- Update the rule description in the Description field (optional).
- Click Save.
- You’re taken back to the LAN Firewall Rules page, and we can see that our two rules have been created.
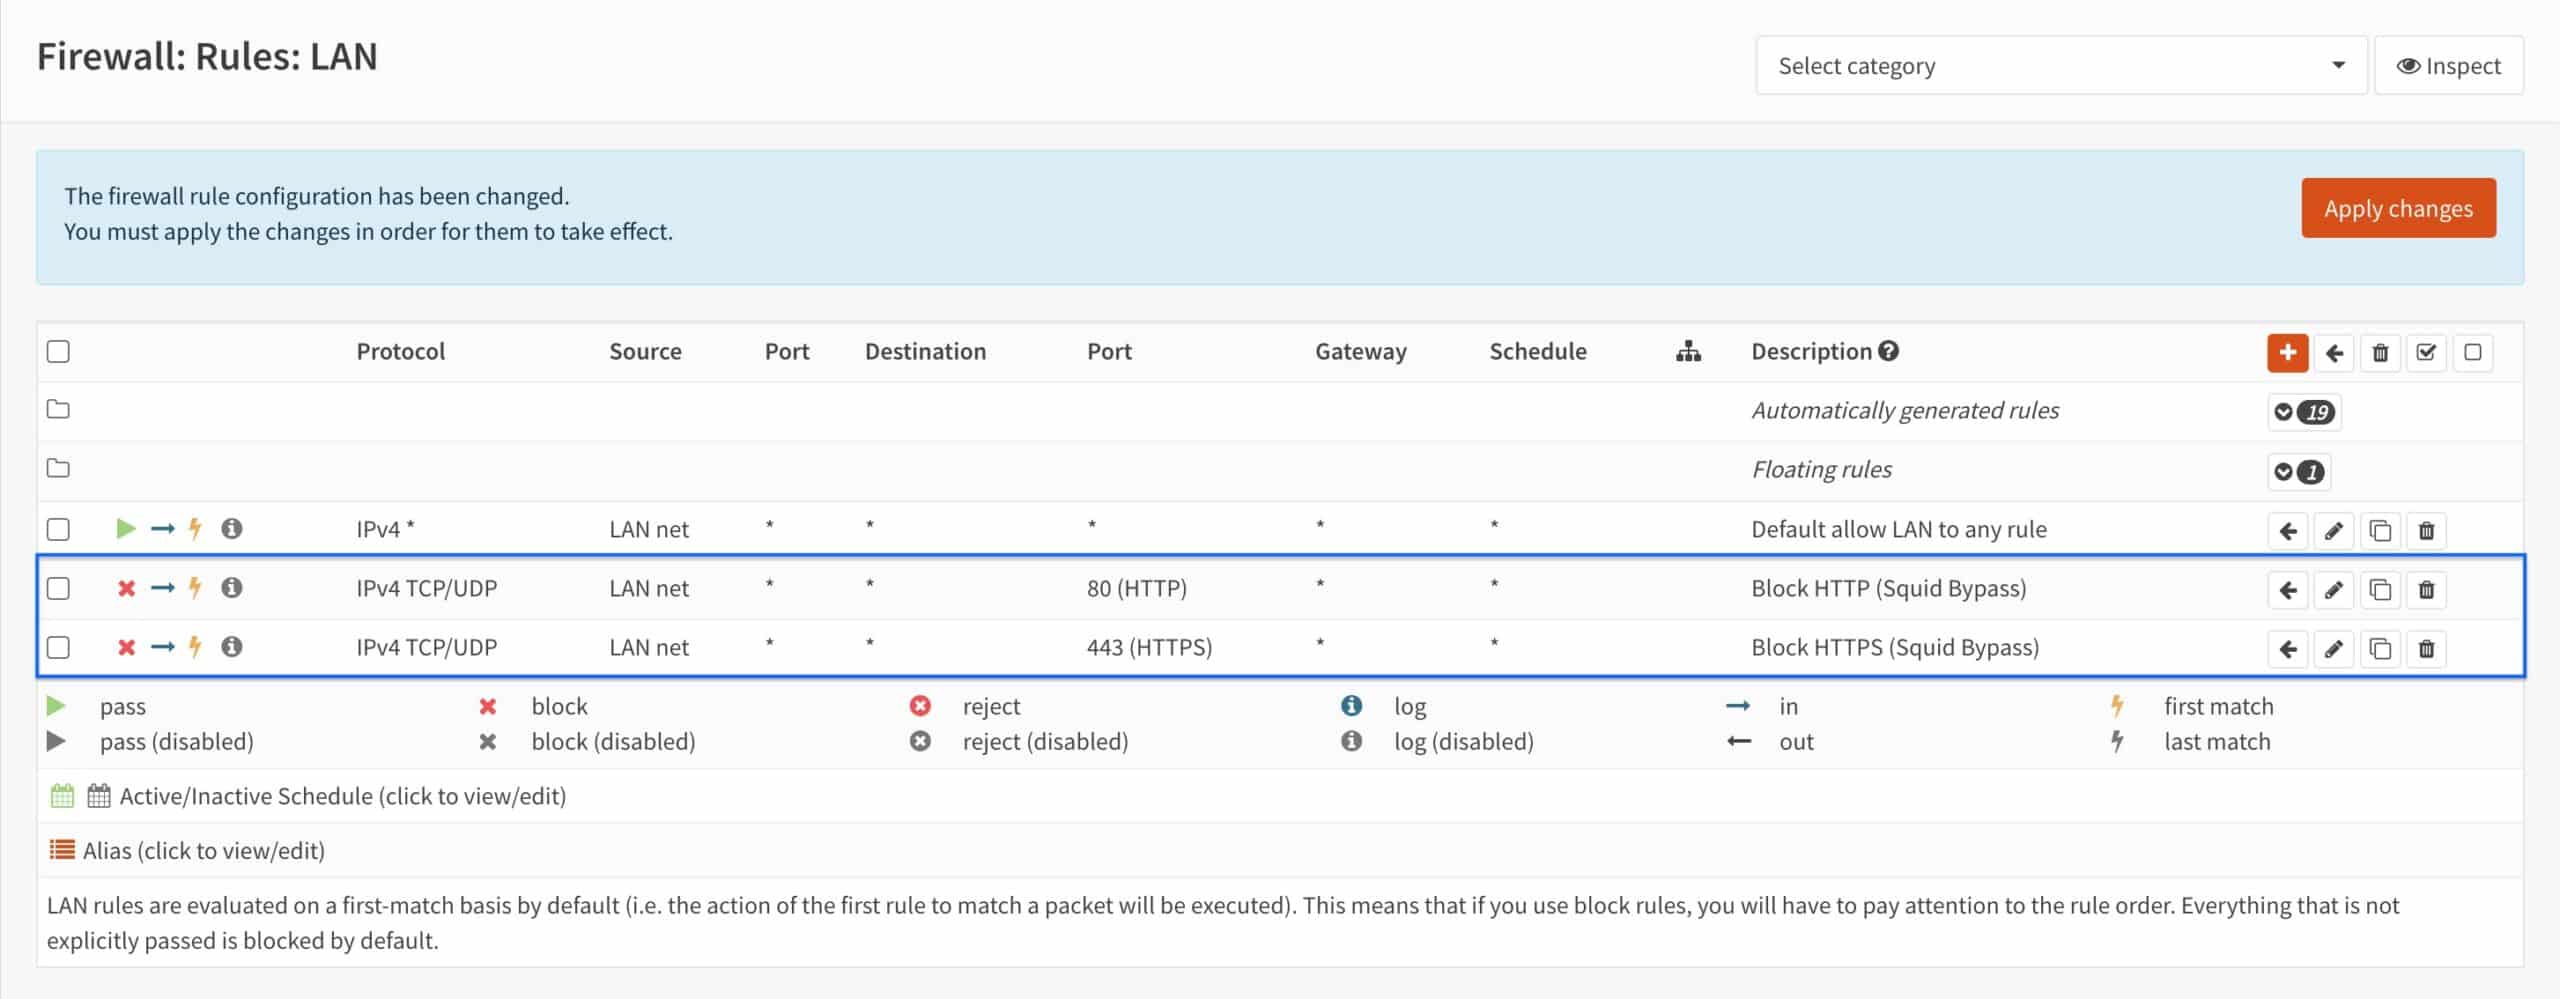
- Tick both rules’ selection boxes and click the Left Arrow icon next to the Default allow LAN to any rule. That will move the selected rules on top of the Default allow LAN to any rule. OPNsense applies firewall rules in a top-down order, so it’s critical that our “block” rules be above our “allow” rule.
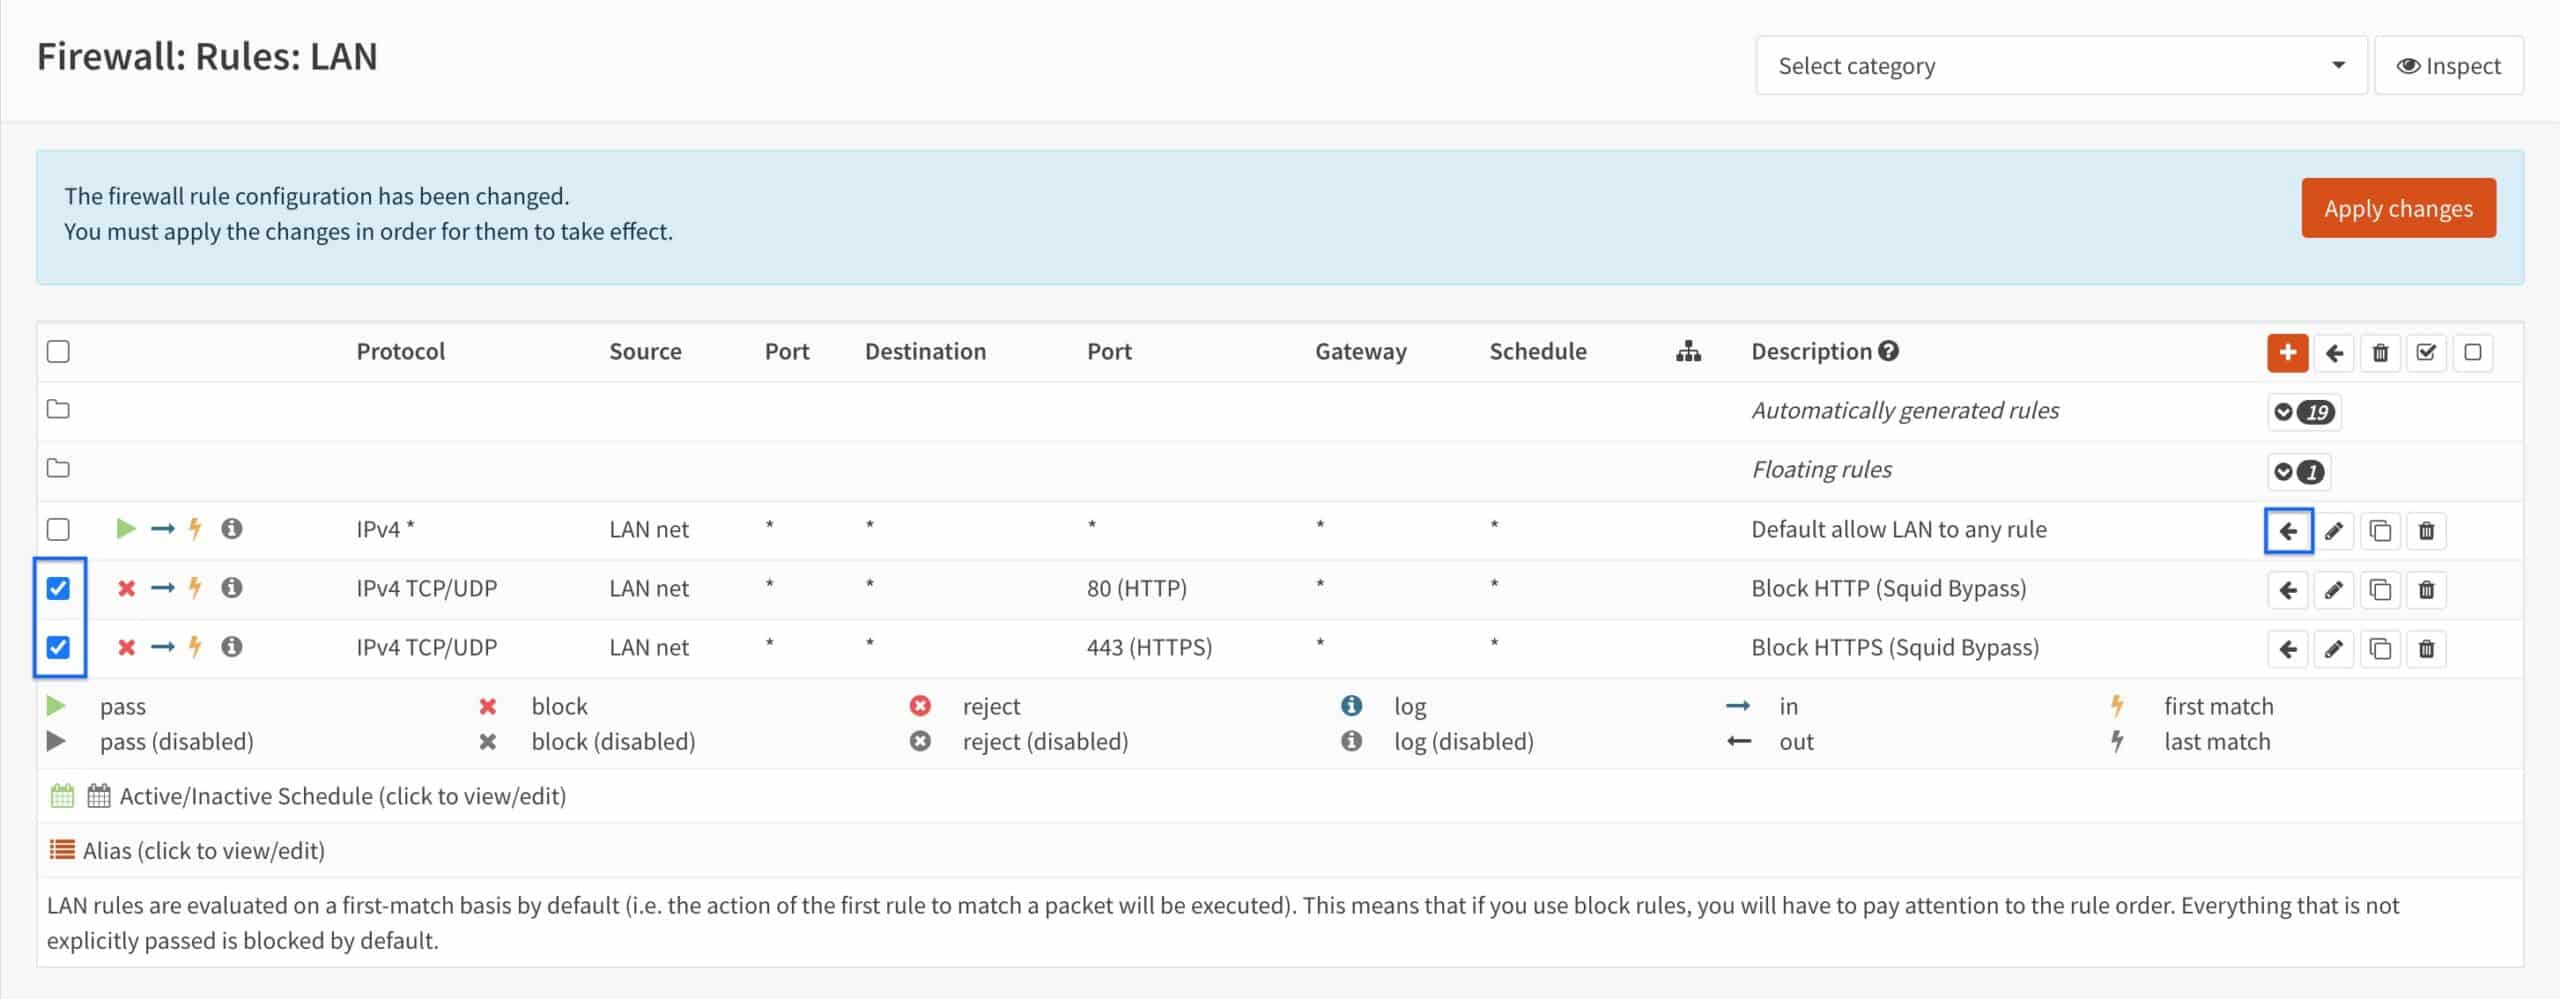
- Our “block” rules are now in the correct position. Click Apply changes.
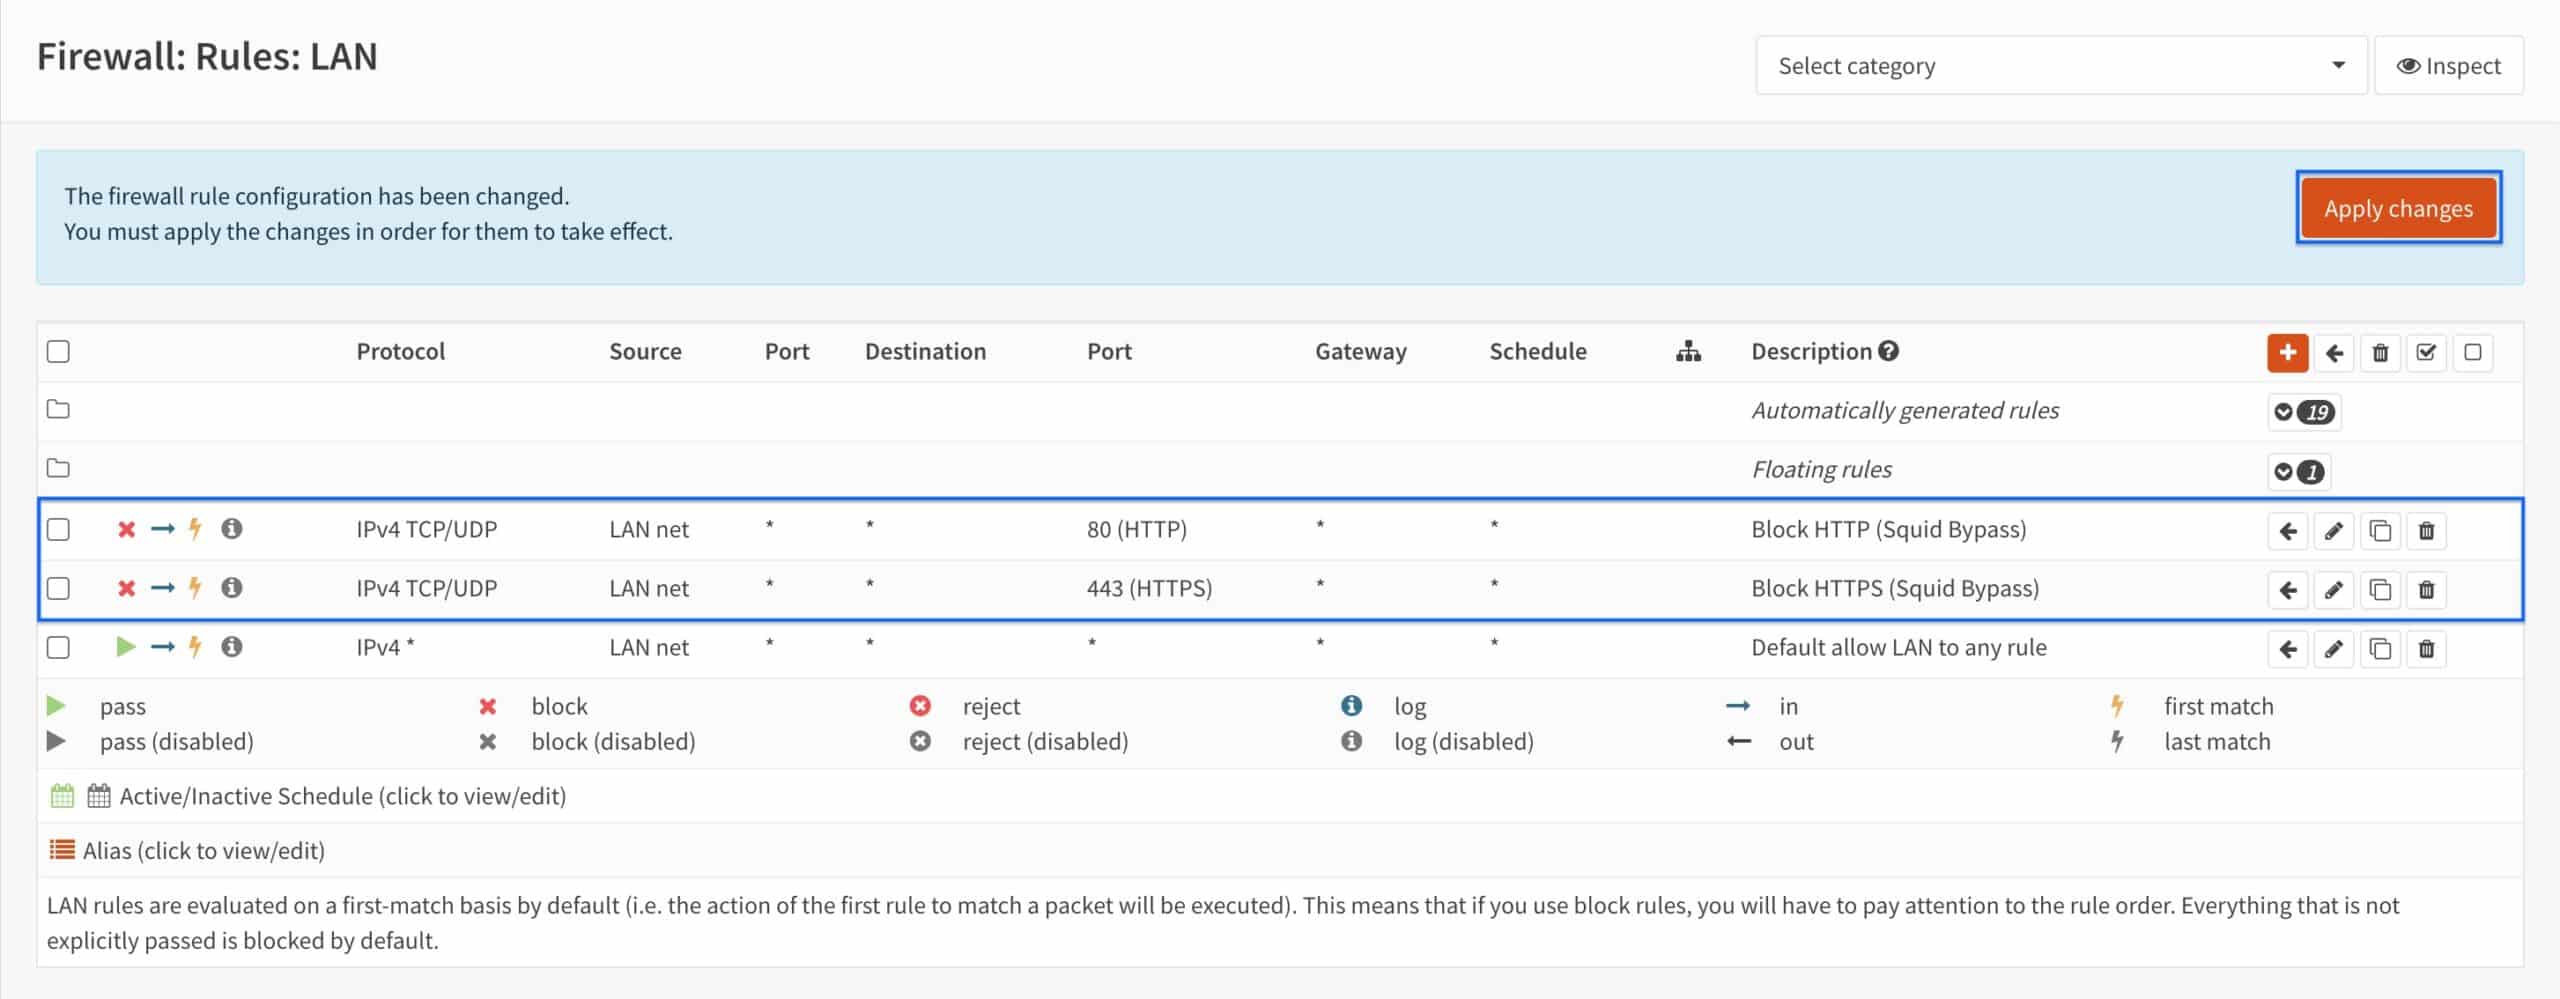
- Our firewall rules are applied, and now, users on your LAN cannot bypass the proxy server.
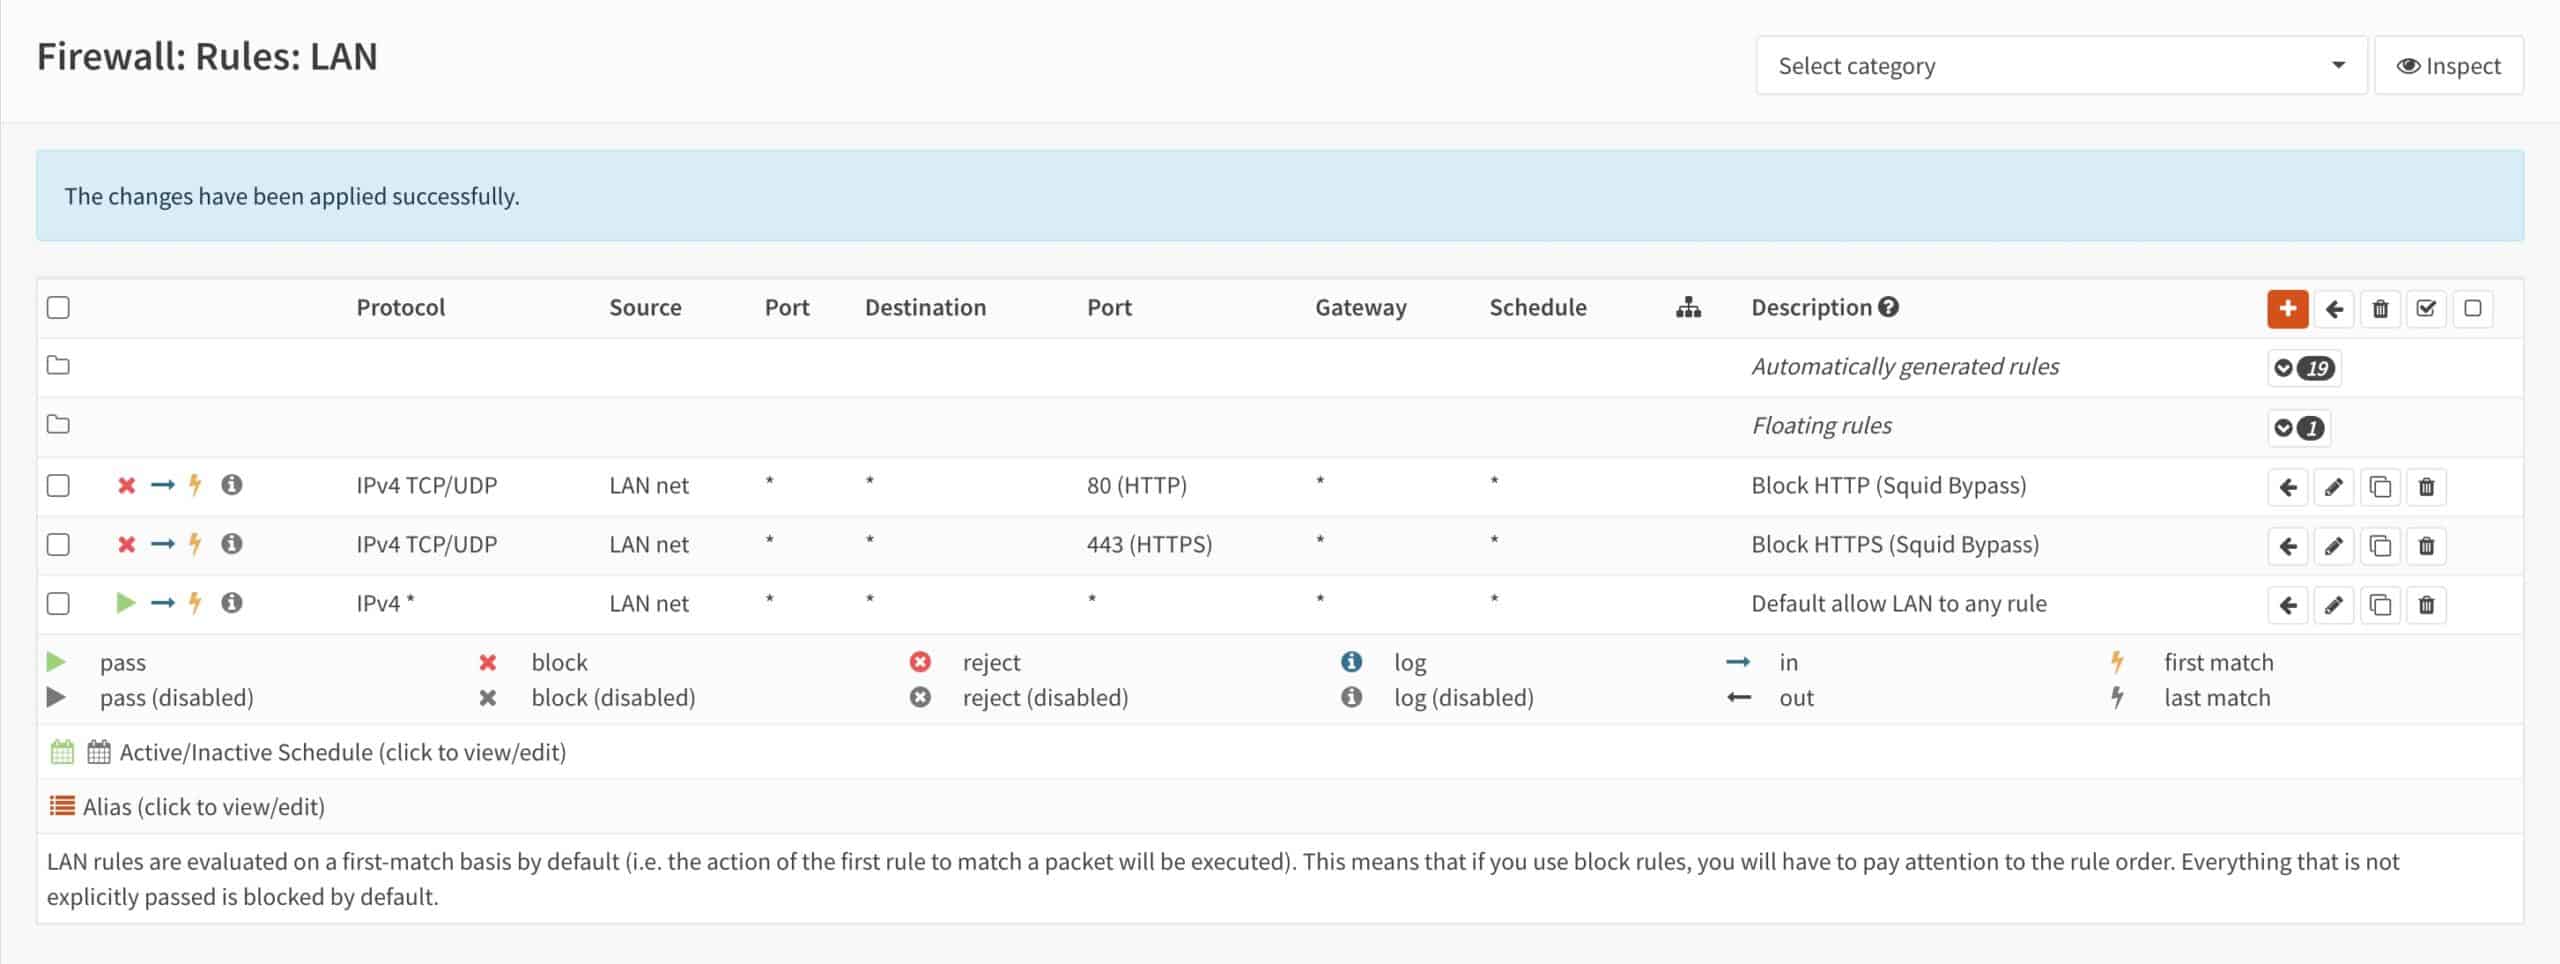
Note: If you’re wondering why we didn’t need to create firewall rules to send LAN traffic through the proxy, it’s because Squid takes care of this behind the scenes.
Wrapping up
You should now have a functioning Squid proxy with URL-list filtering running on OPNsense.
This configuration can reduce bandwidth consumption, speed up access to frequently requested content through caching, and block many advertising, tracking, and unwanted domains across your network. It also provides a familiar alternative for users migrating from pfSense who relied on Squid and SquidGuard.
While URL-list filtering remains useful, it’s important to understand its limitations on today’s HTTPS-heavy web. Combining Squid with DNS filtering, browser-based blocking, or other network security controls can provide more comprehensive protection where needed.
For most home labs and small networks, however, OPNsense’s built-in Squid implementation provides a straightforward way to reproduce the core functionality traditionally delivered by Squid and SquidGuard in pfSense.
As always, stay safe.
Related:


